
Firestore security rules skill for Claude Code — open paths, missing auth
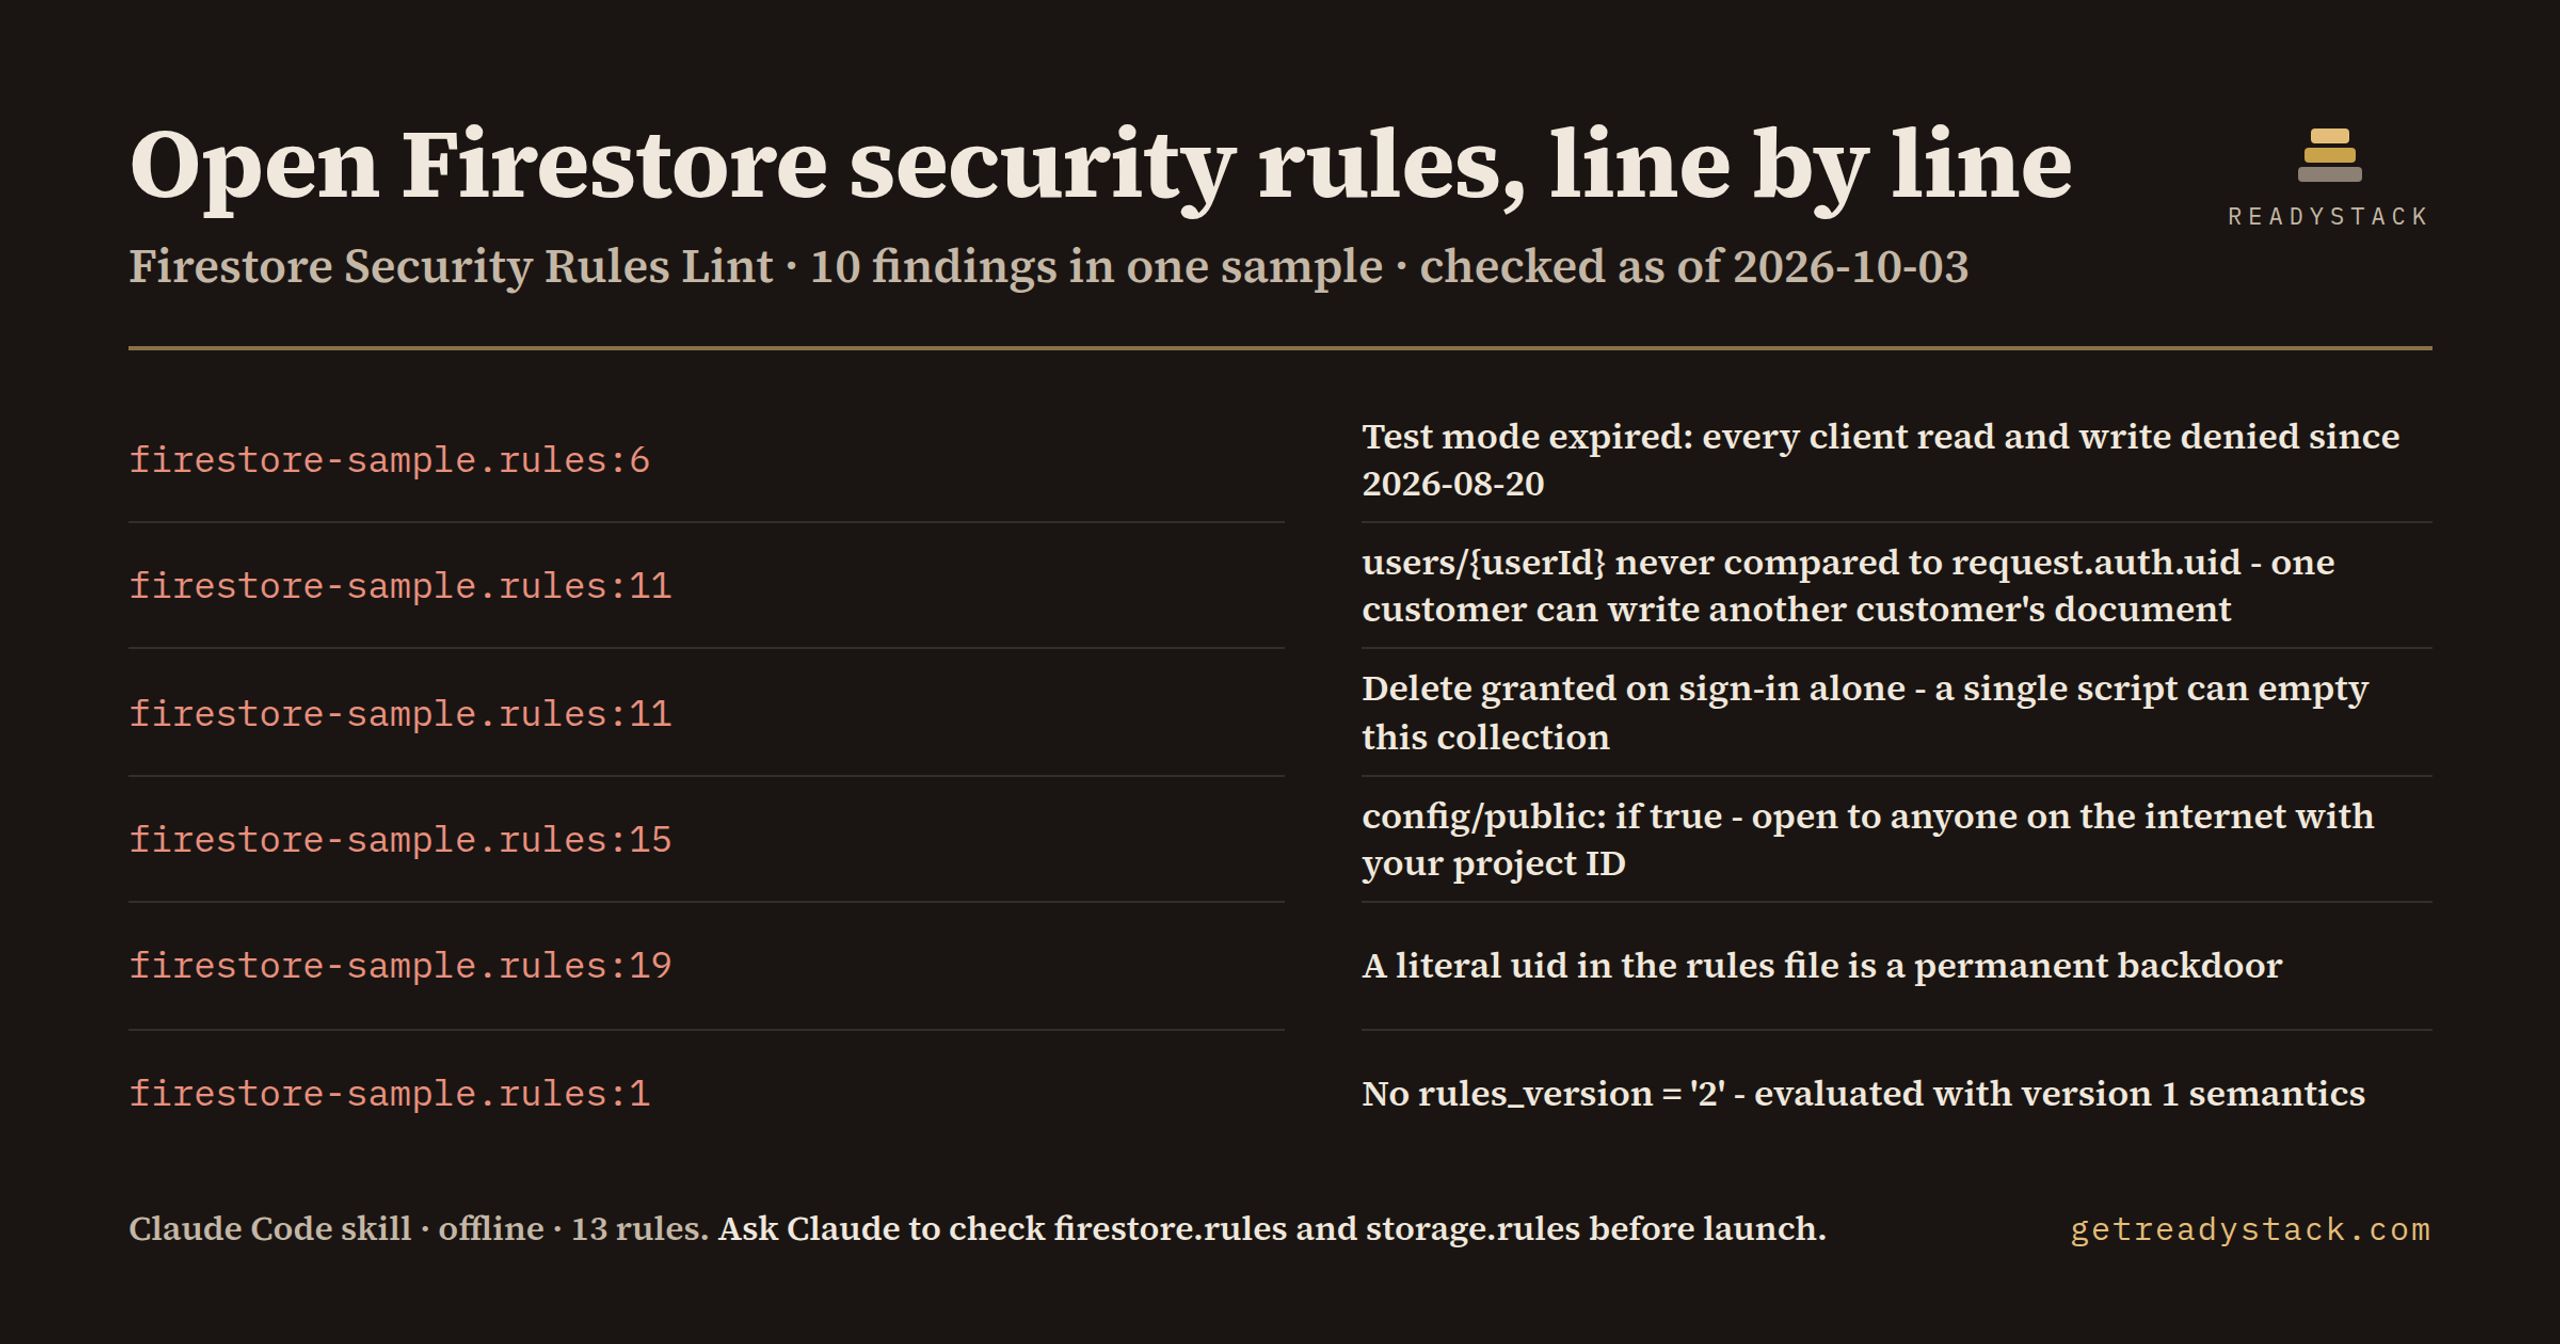
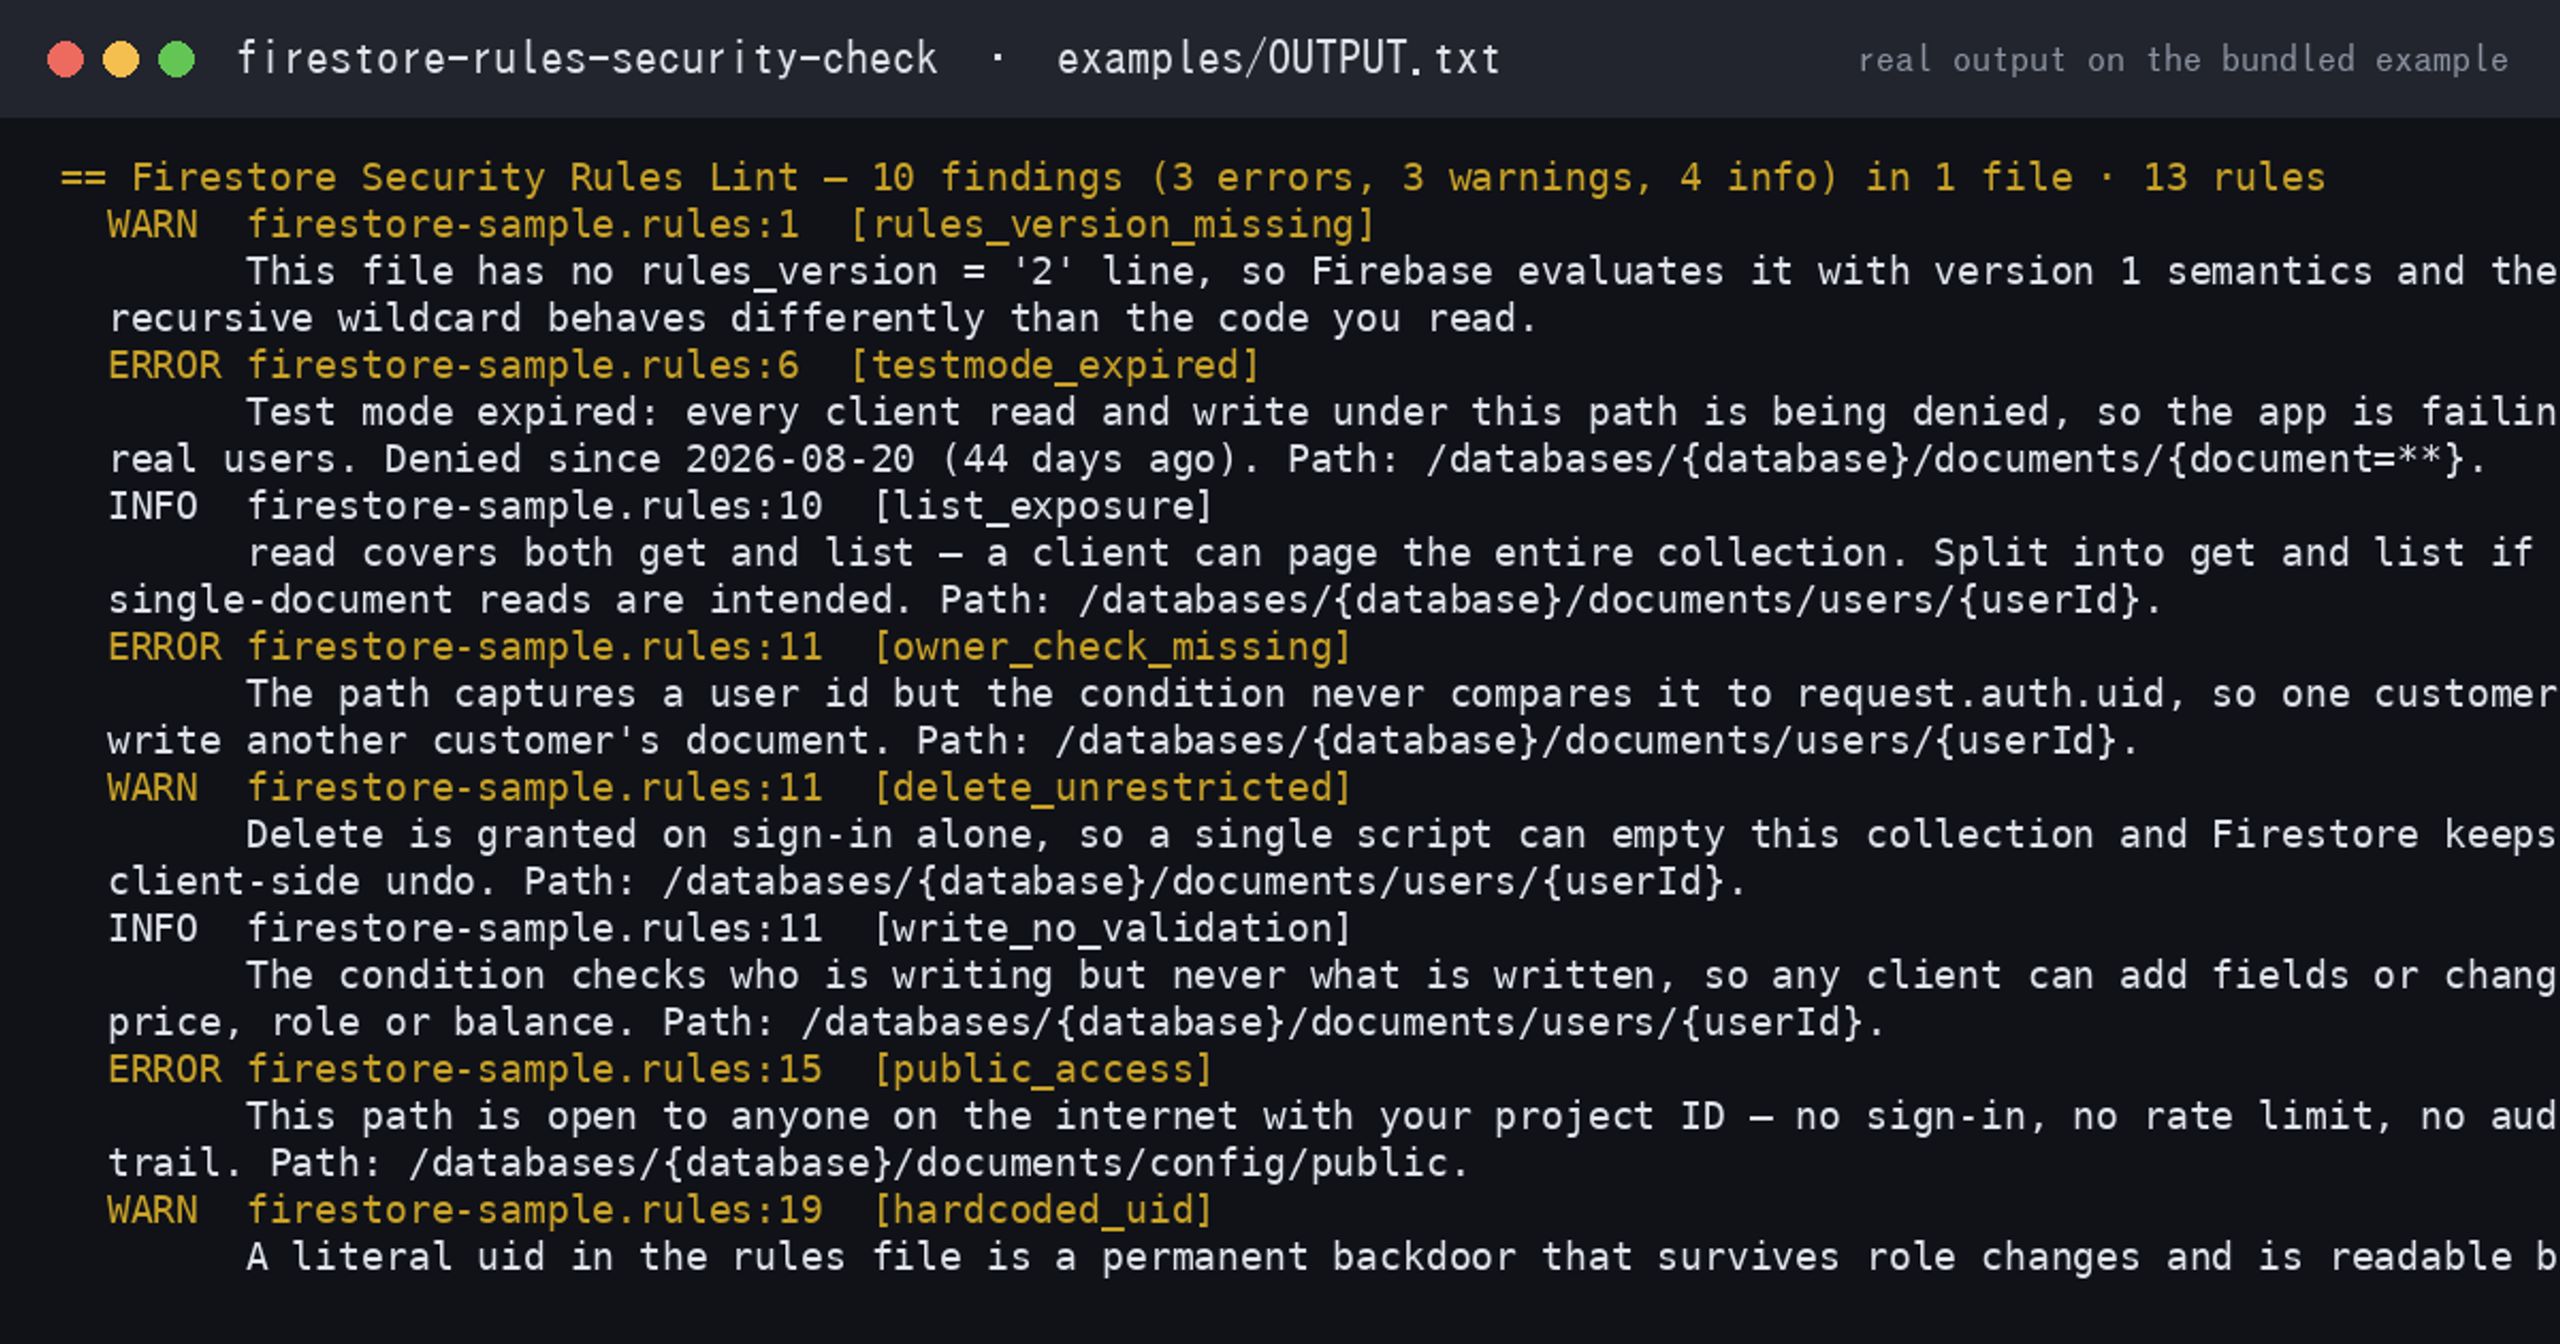
10 findings in one firestore.rules file, each with the path a client can reach
On the bundled sample: 10 findings (3 errors, 3 warnings, 4 info) in 1 file from 13 rules, including test mode denied since 2026-08-20.
Who it’s for
Firebase developers who keep firestore.rules or storage.rules in git - often first drafted in test mode or by a coding assistant - and are about to launch.
What breaks, and when
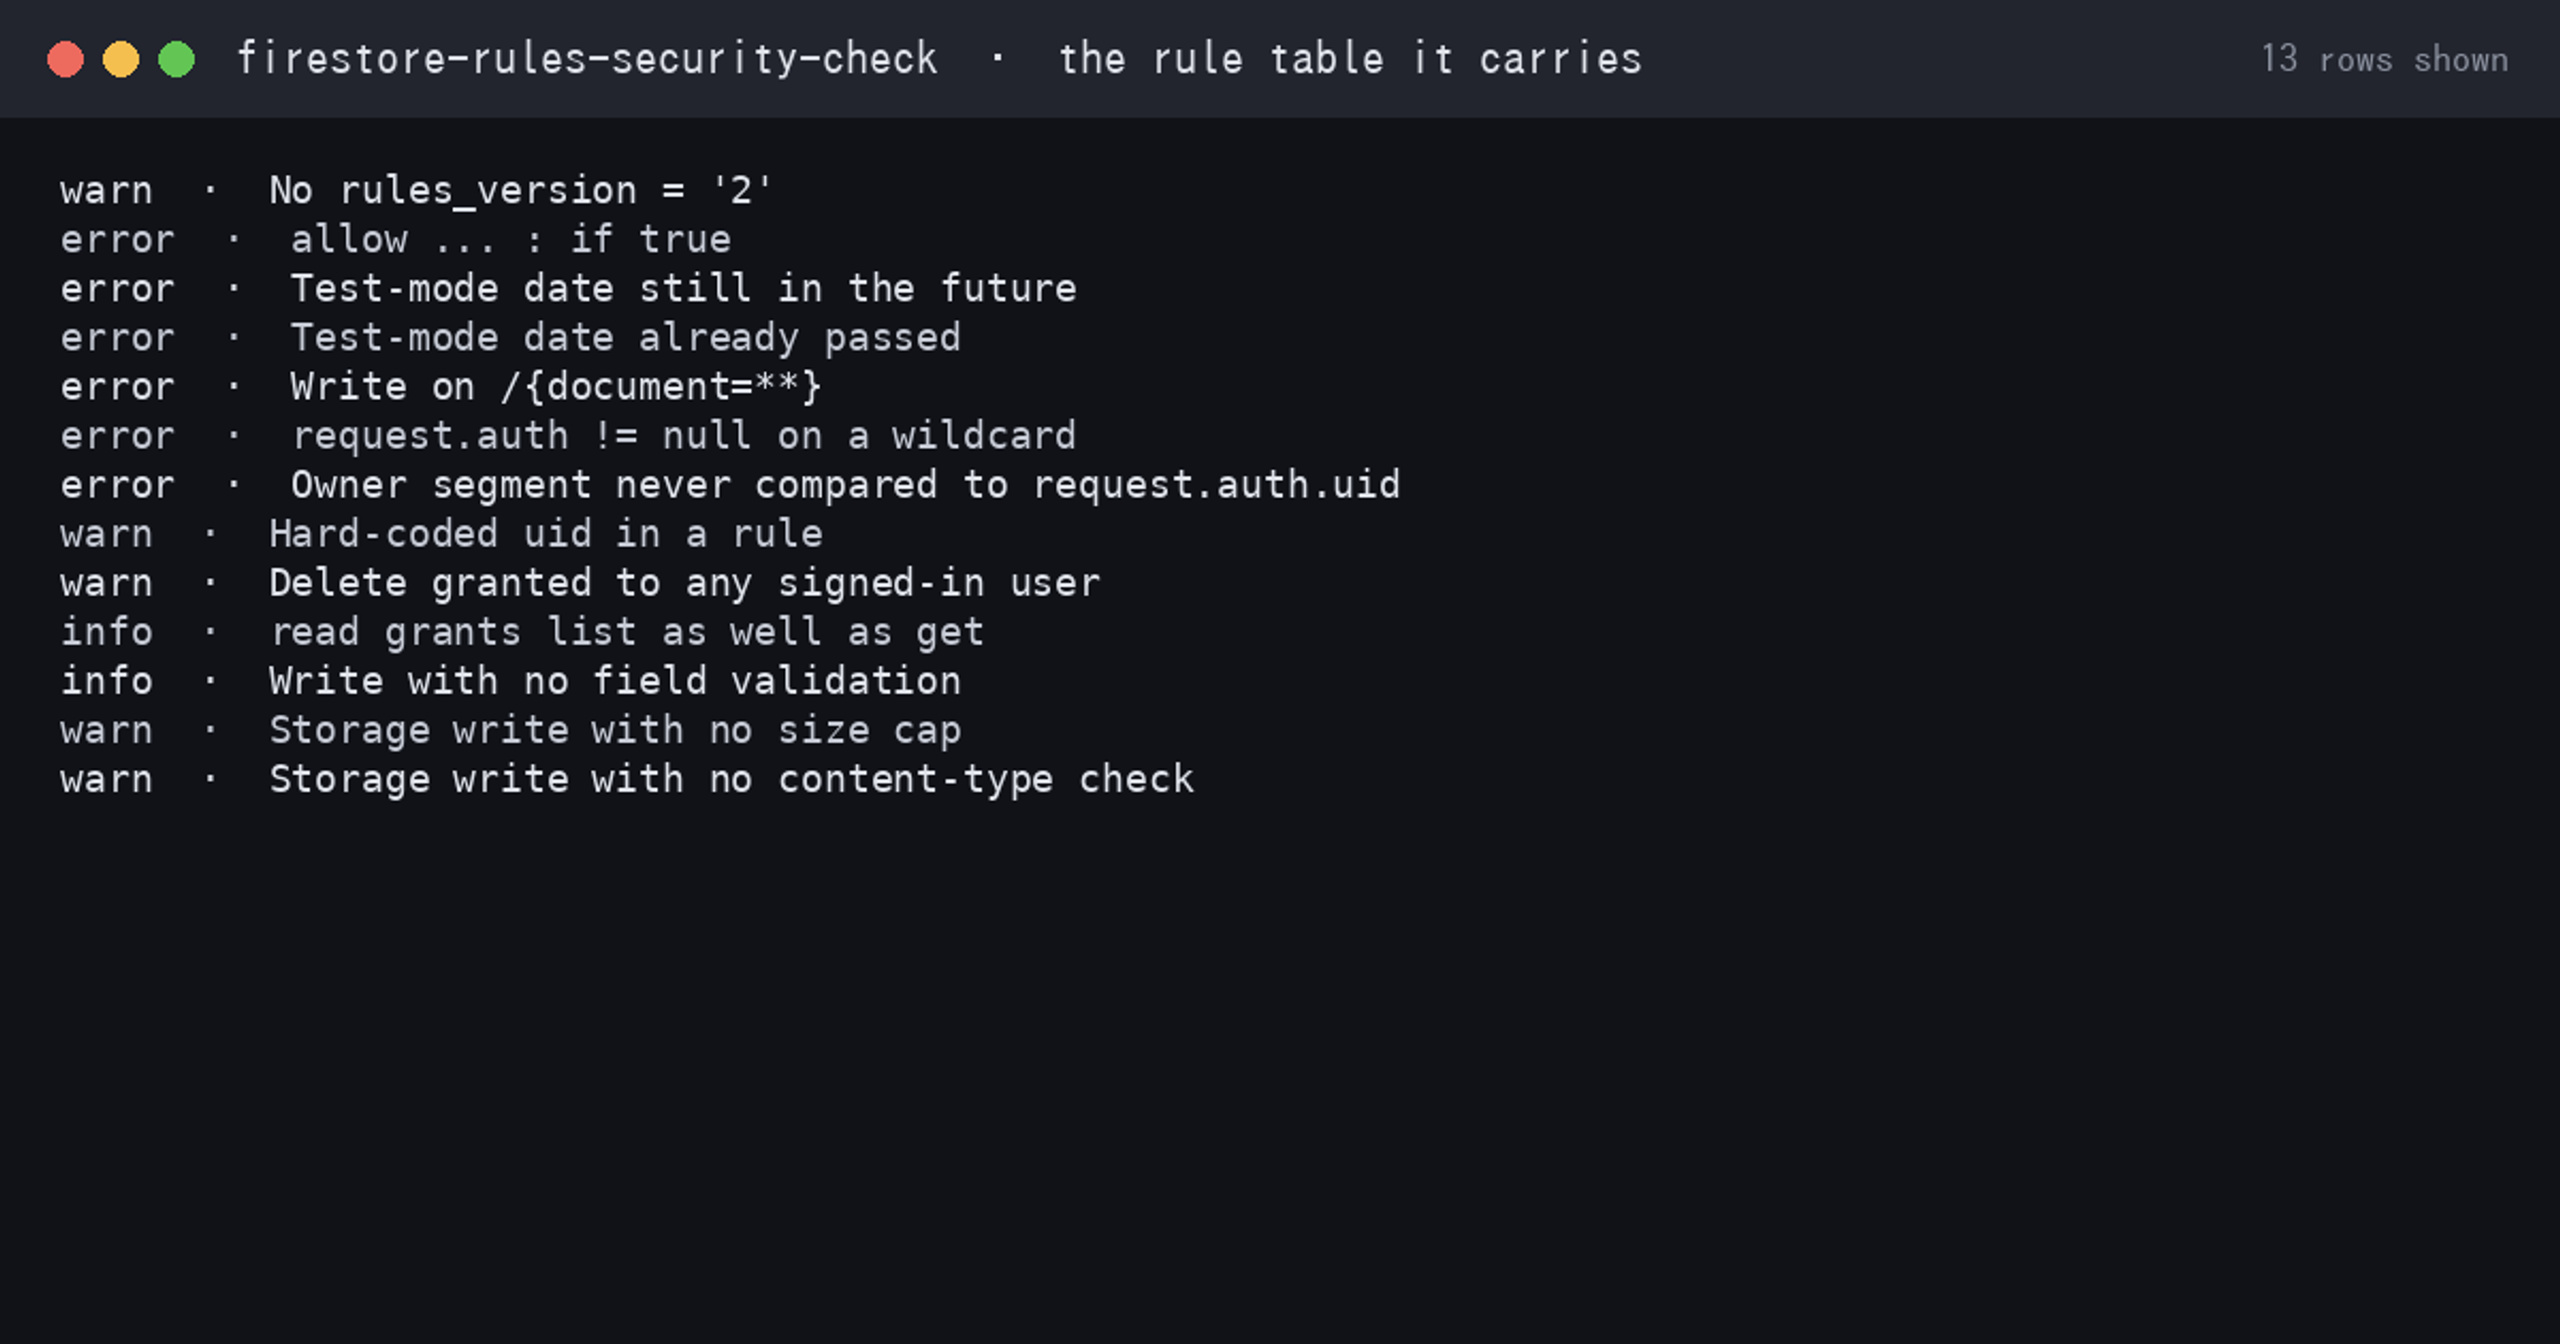
With allow … : if true the path is open to anyone on the internet with your project ID. Once a test-mode date passes, every client read and write is denied.
What you get
• SKILL.md, an offline Node scanner and the 13-rule table
• file:line, severity and the match path of every flagged allow
See it first
The real output of the bundled example is on getreadystack.com/skills/firestore-rules-security-check/ — free, no sign-up, so you see what it finds before you pay.
Install in 30 seconds
Unzip into ~/.claude/skills/, then ask Claude Code: “We’re launching our Firebase app next week. Can one user read or overwrite another user’s data with our current rules? Don’t edit anything yet.”. Needs Node 16+.
What it does not do
It does not connect to Firebase or evaluate helper functions; it reads *.rules text only.
FAQ
Q: How is this different from asking Claude without the skill?
A: The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of guessing from memory.
Q: How do I get the files?
A: In your Whop library after paying: the lesson “firestore-rules-security-check.zip”.