
Firmware release security Skill
Find the sdkconfig and prj.conf lines that must not ship in production firmware
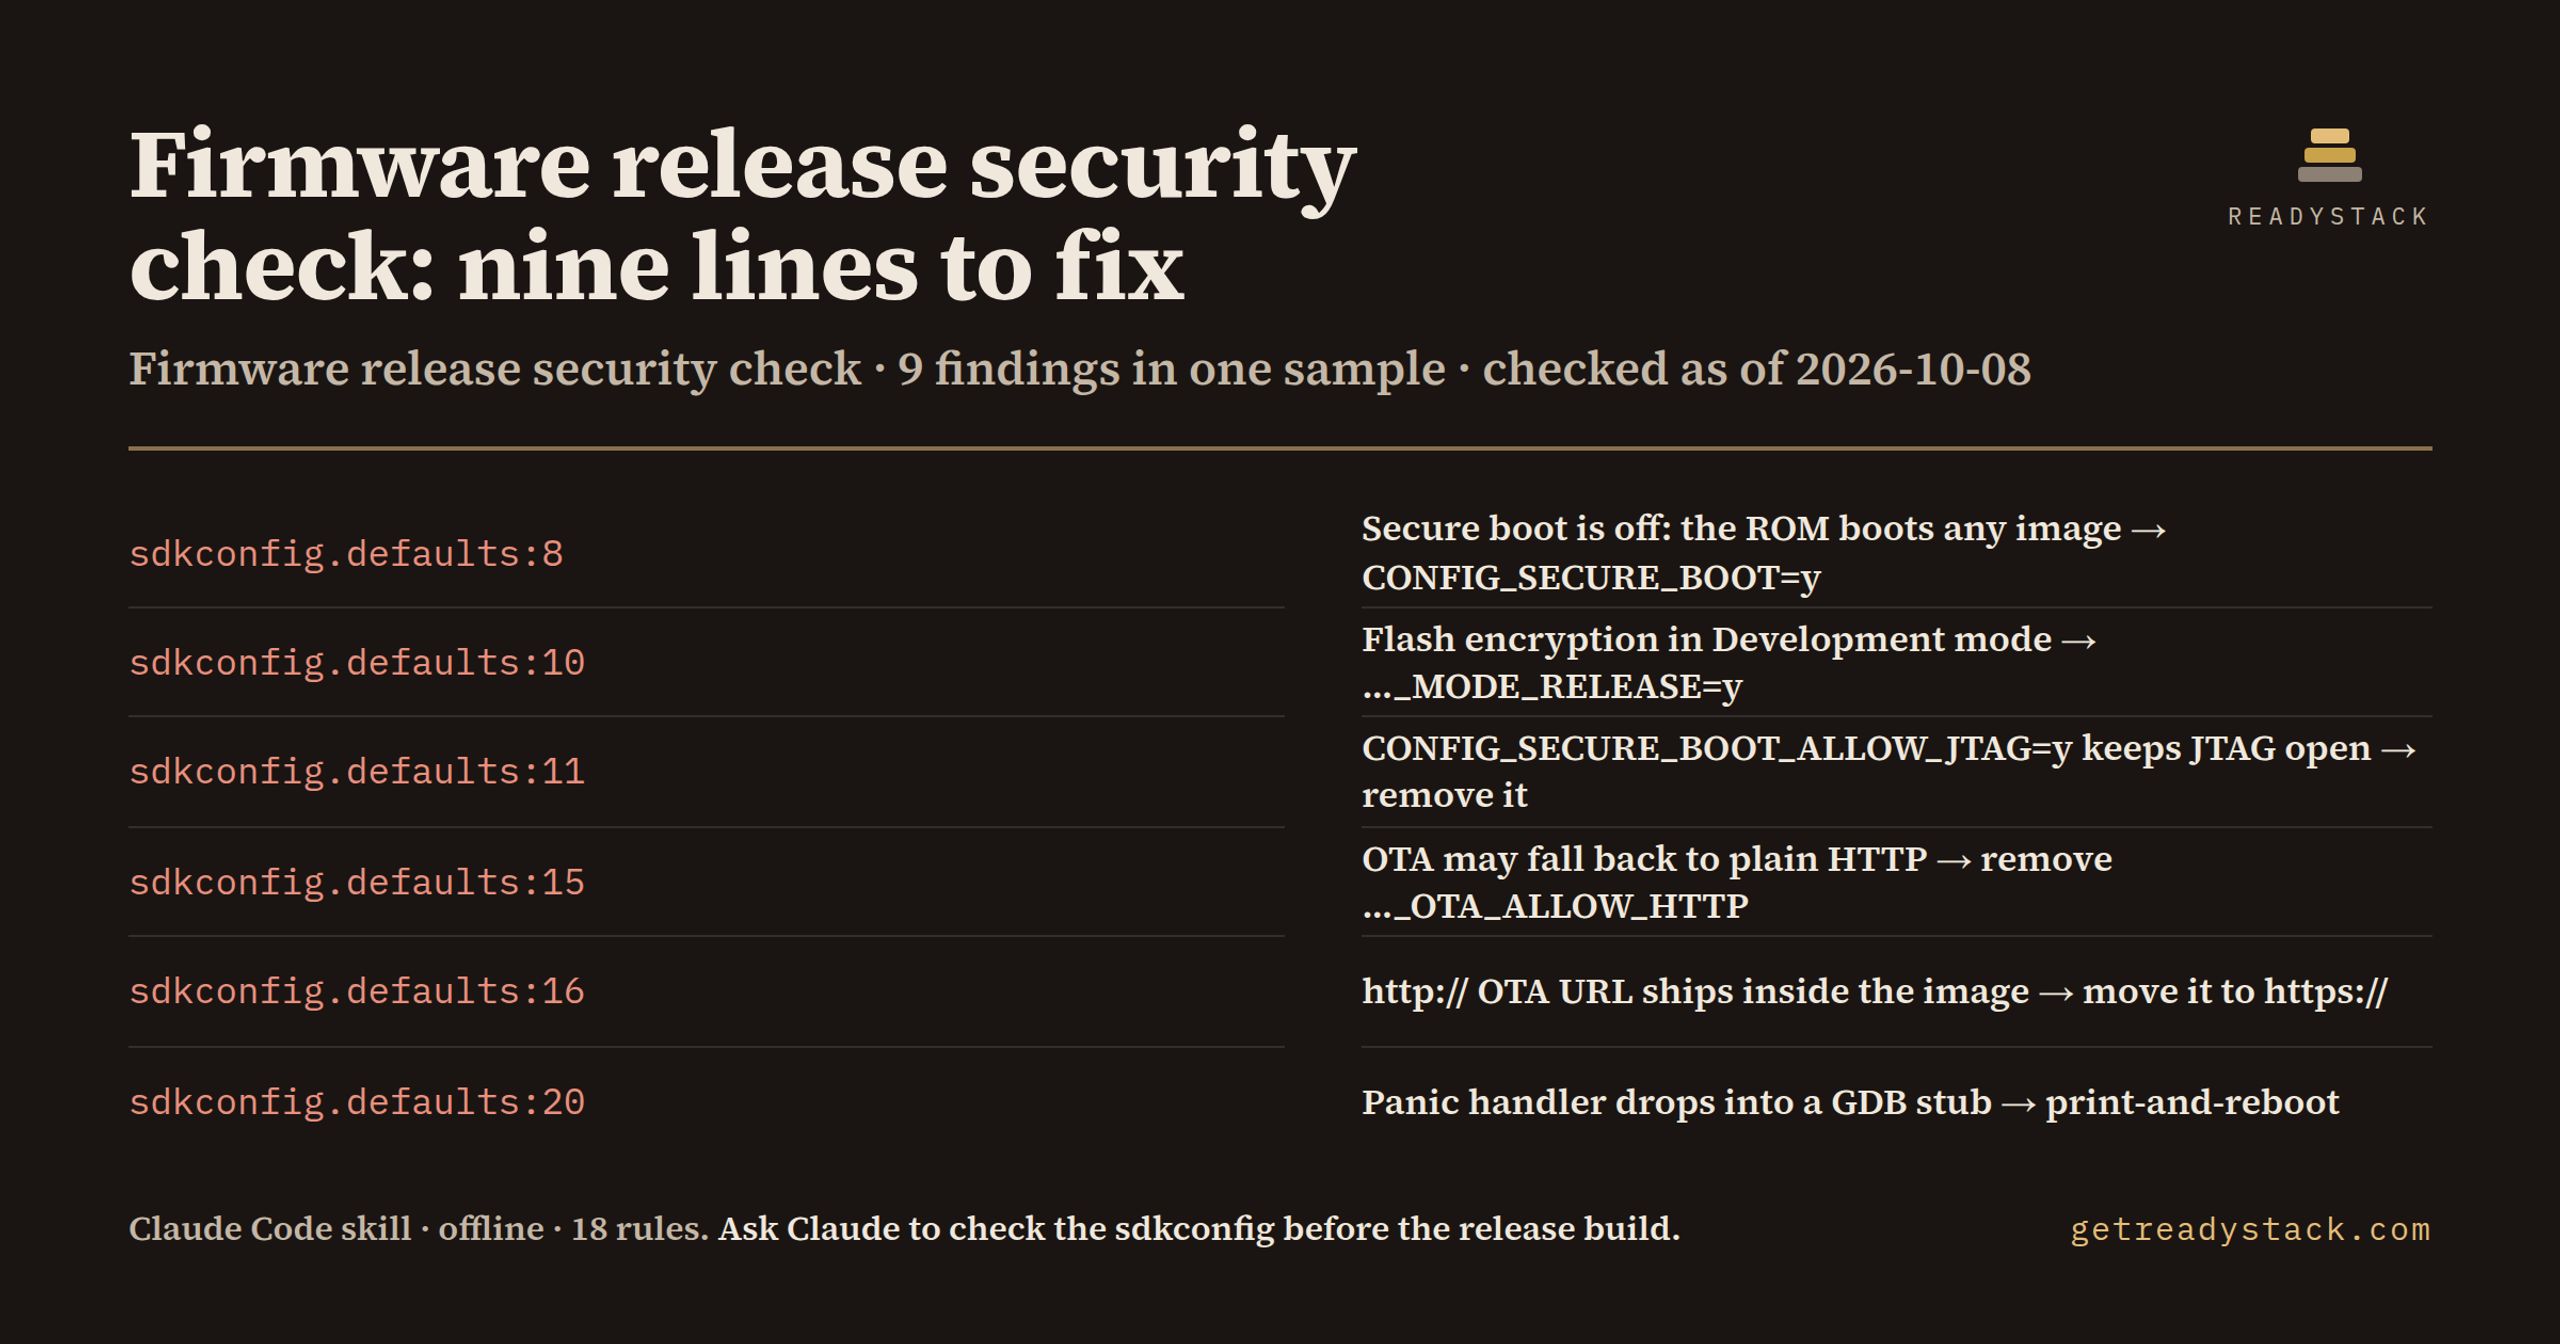
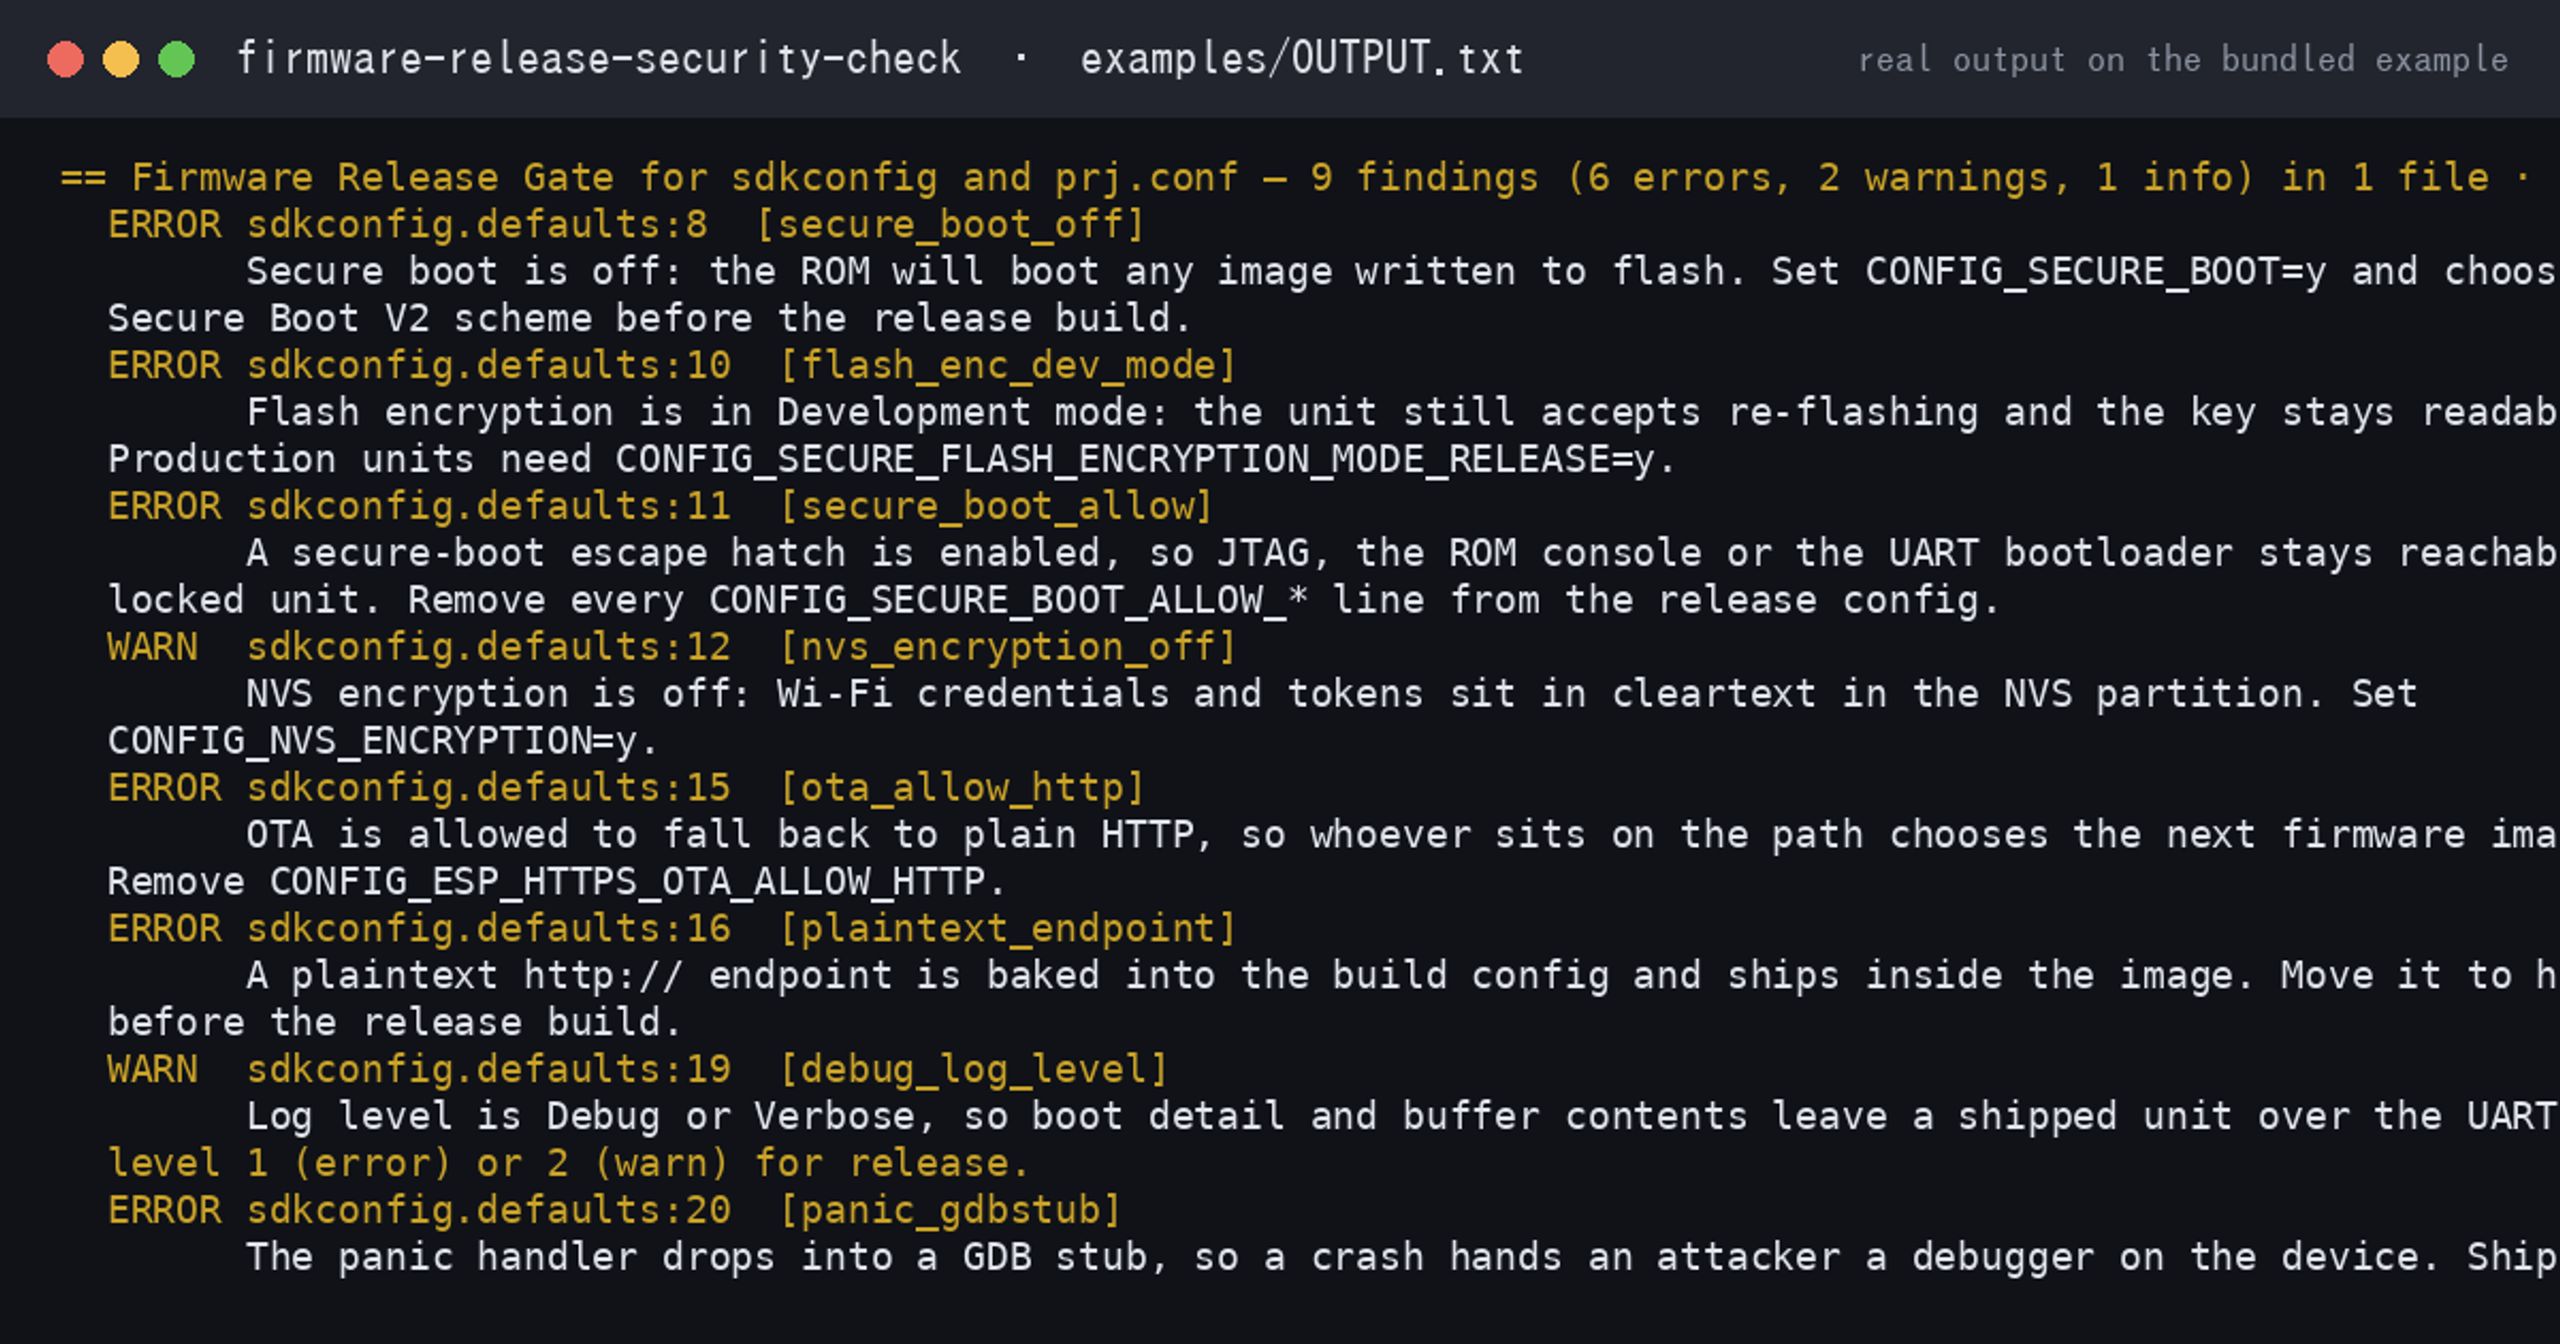
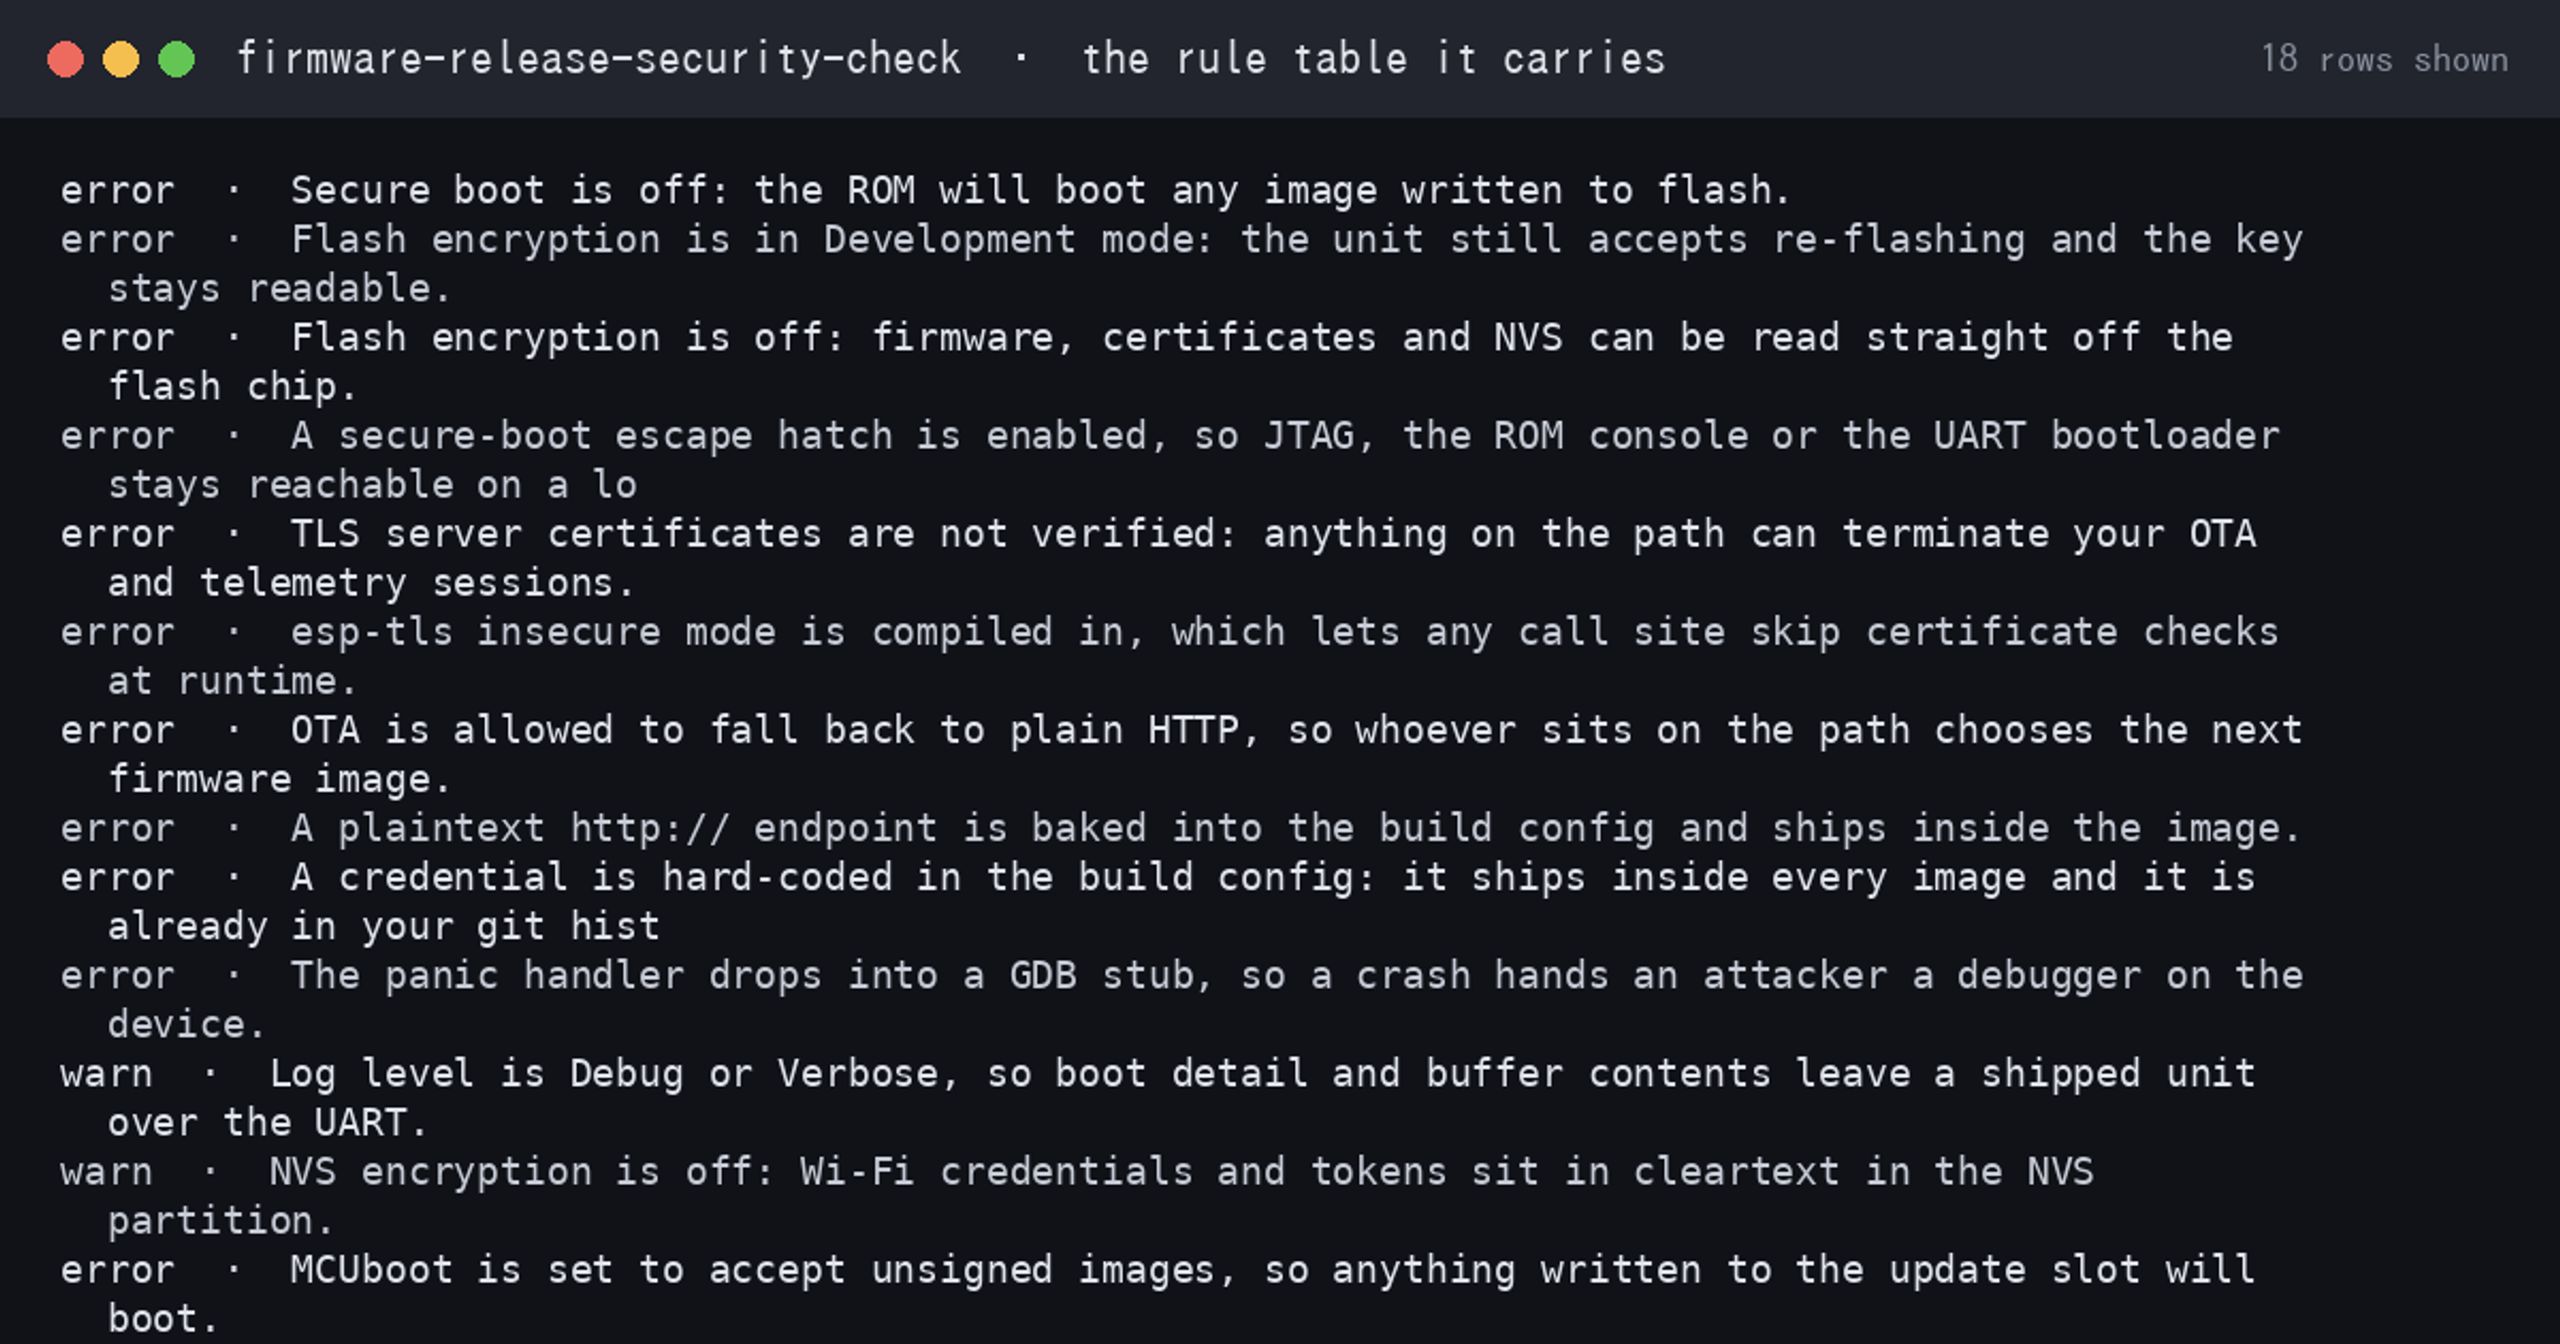
On the bundled sdkconfig.defaults: 9 findings (6 errors, 2 warnings, 1 info) in 1 file from 18 rules, including secure boot off and OTA over plain HTTP.
Who it’s for
For ESP32 and Zephyr firmware engineers cutting a production image from a config that started on the bring-up branch.
What breaks, and when
Ship it and every unit boots any image written to flash, accepts OTA over plain HTTP and keeps JTAG reachable, and the release build is the moment it gets locked in.
What you get
• SKILL.md, an offline Node scanner and the 18-rule table
• file:line, severity and the CONFIG_ setting to use instead
See it first
The real output of the bundled example is on getreadystack.com/skills/firmware-release-security-check/ — free, no sign-up, so you see what it finds before you pay.
Install in 30 seconds
Unzip into ~/.claude/skills/, then ask Claude Code: “We’re cutting the production firmware build for our ESP32 gateway this week. Is the sdkconfig in this repo safe to ship to customers? Don’t edit anything yet.”. Needs Node 16+.
What it does not do
It does not build the image, run menuconfig or touch eFuses; it reads config text only.
FAQ
Q: How is this different from asking Claude without the skill?
A: The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of guessing from memory.
Q: How do I get the files?
A: In your Whop library after paying: the lesson “firmware-release-security-check.zip”.