
OWASP Dependency-Check config Skill
Finds why your OWASP Dependency-Check scan cannot update or never fails
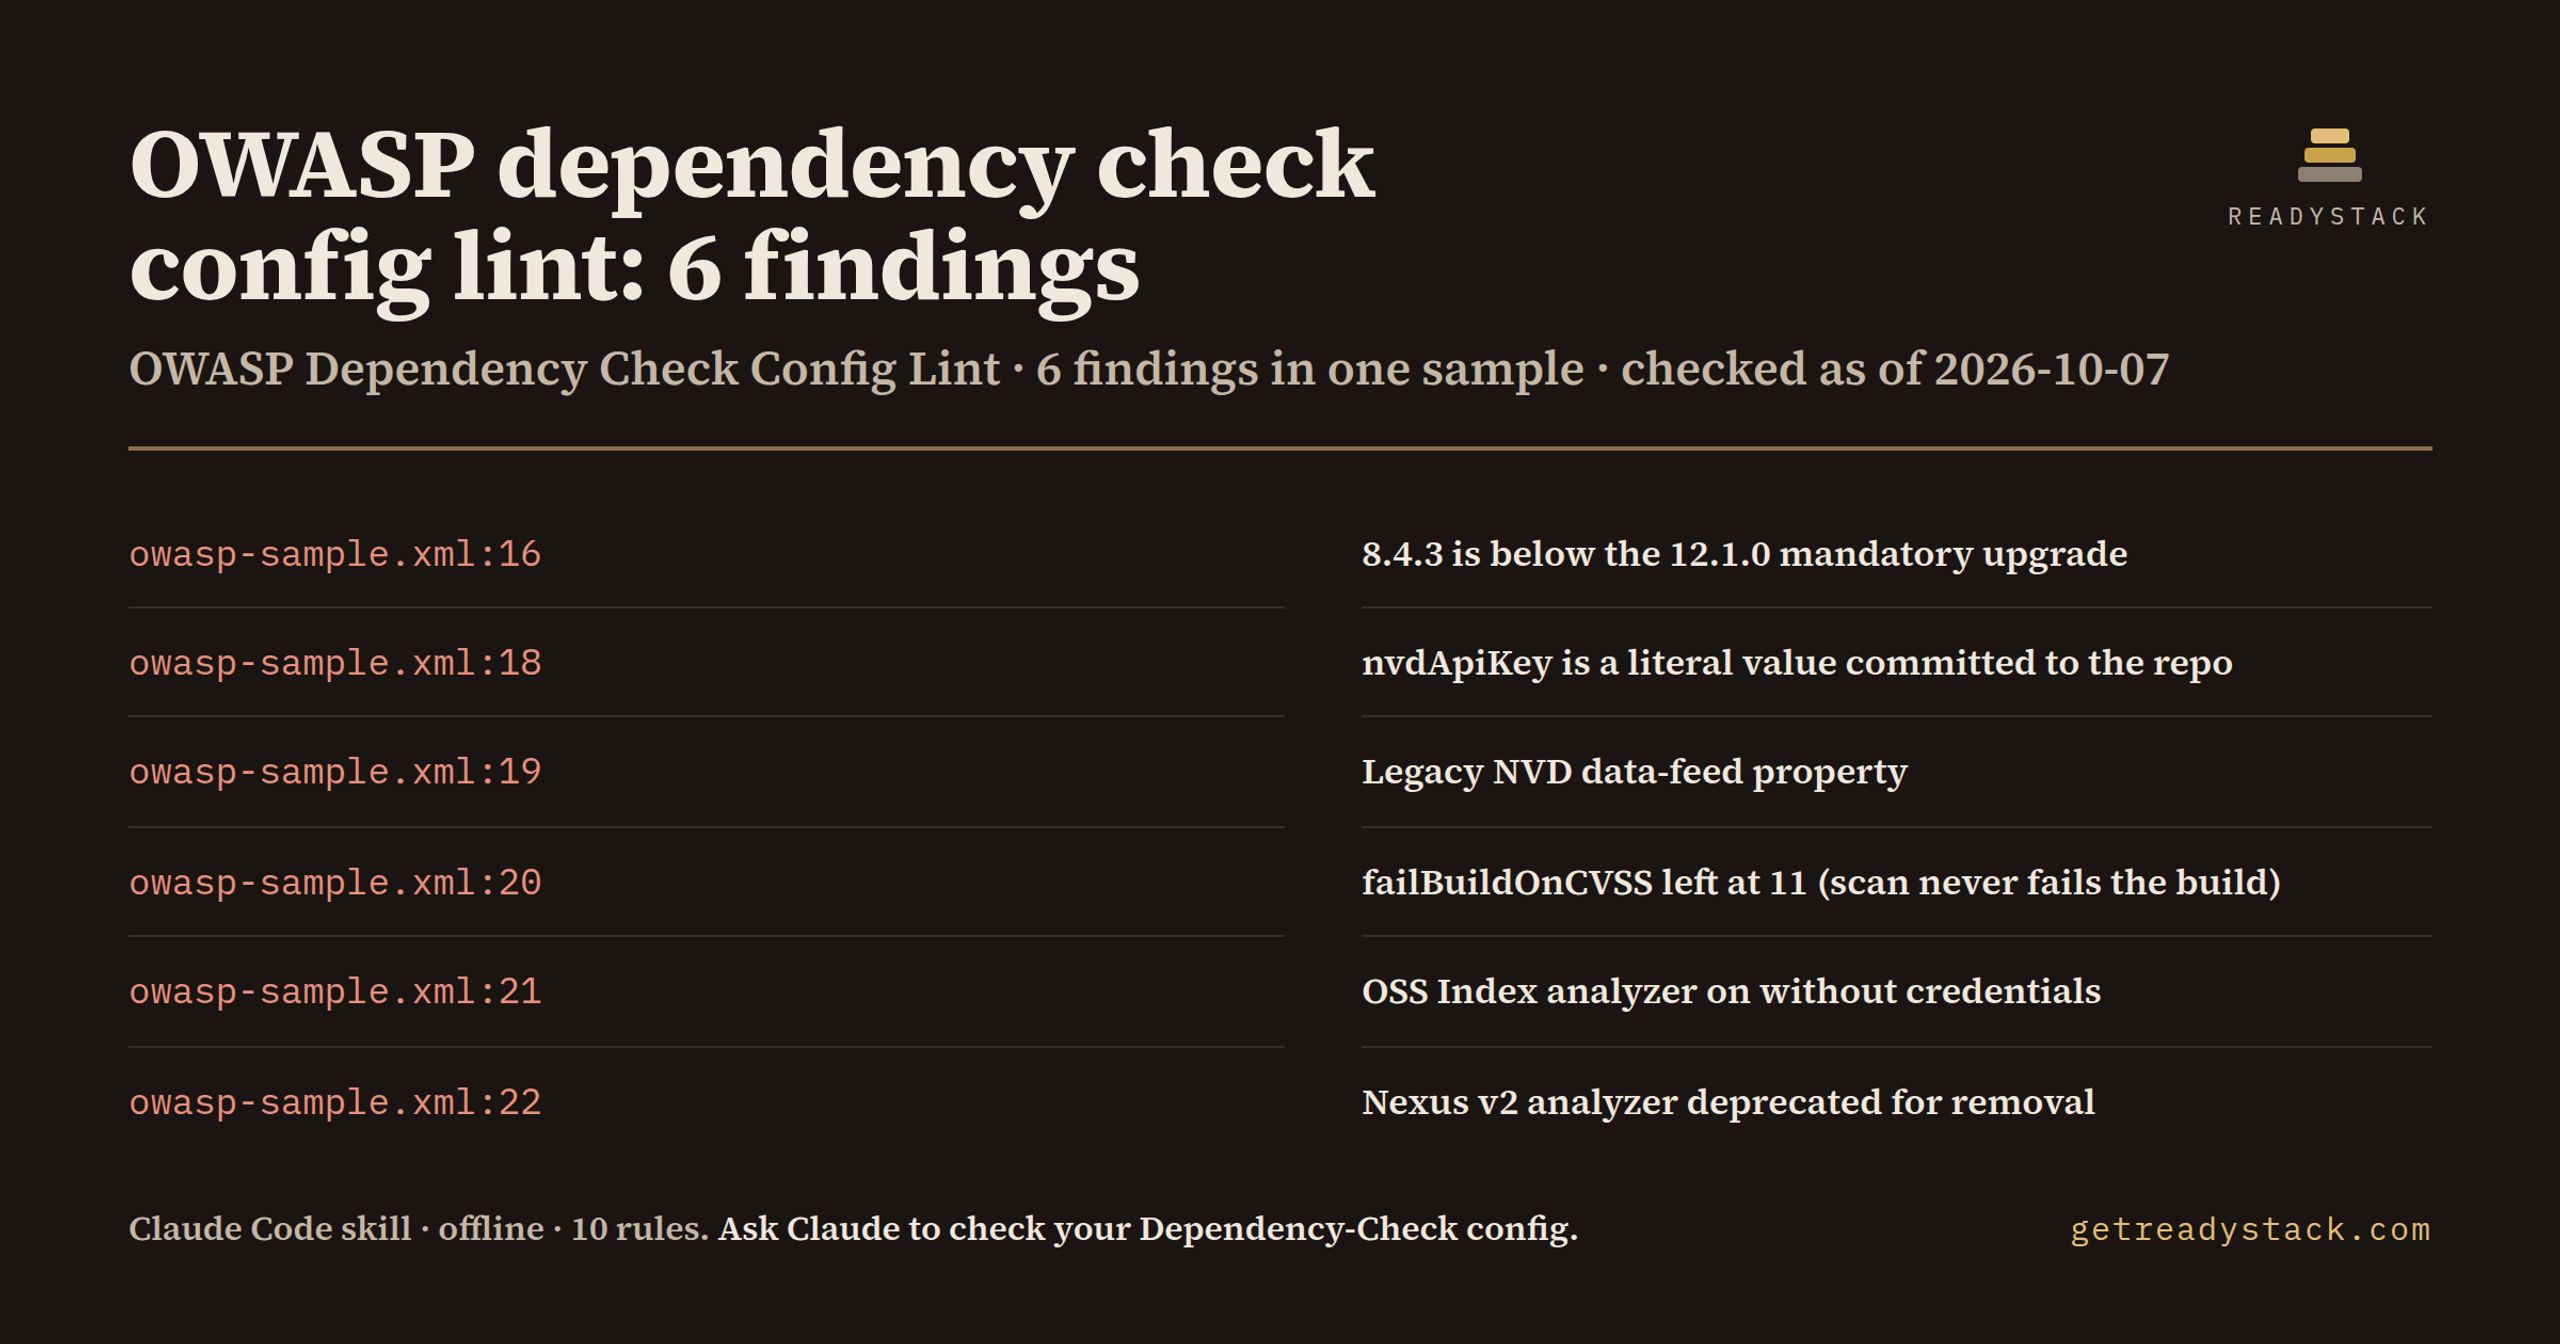
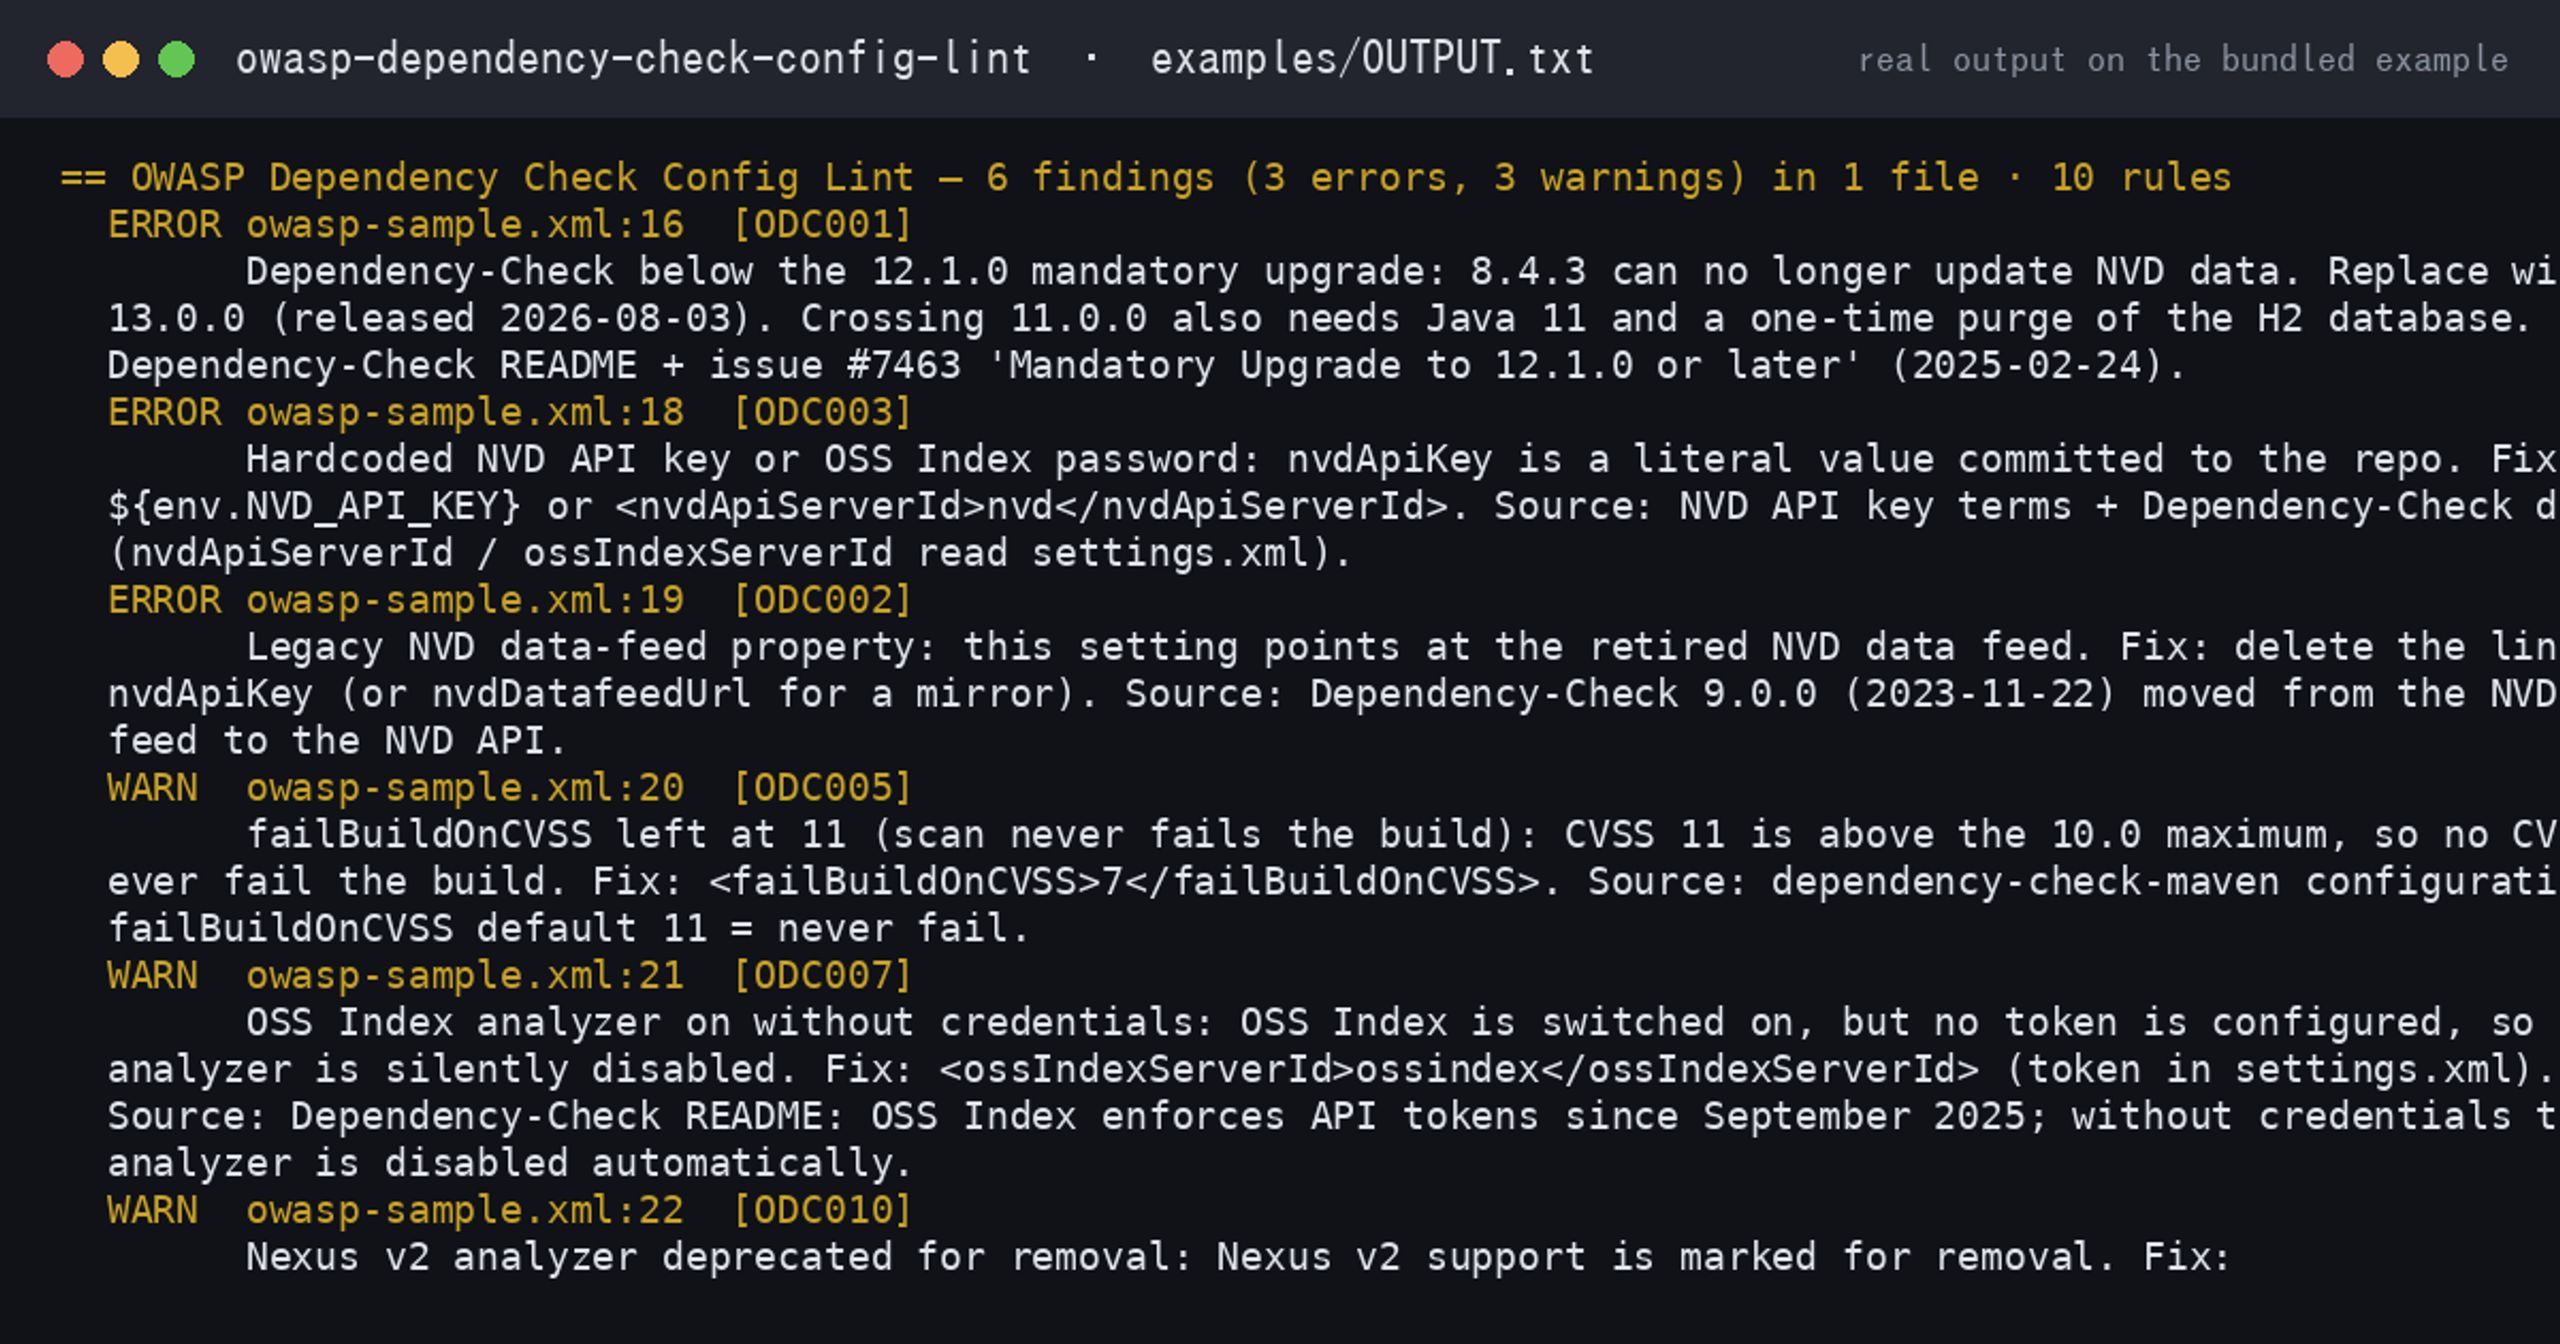
On one 35-line pom.xml it printed 6 findings (3 errors, 3 warnings) from 10 rules, each with file:line, the fix and a dated source.
Who it’s for
For Java teams who run OWASP Dependency-Check in Maven, Gradle or CI and treat a green scan as proof the build is clean.
What breaks, and when
Below the 12.1.0 mandatory upgrade (2025-02-24) the scan can no longer update NVD data, and failBuildOnCVSS 11 means no CVE can ever fail the build.
What you get
• A scanner Claude runs over every pom.xml, Gradle and CI file - not a guess…
See it first
The real output of the bundled example is on getreadystack.com/skills/owasp-dependency-check-config-lint/ — free, no sign-up, so you see what it finds before you pay.
Install in 30 seconds
Unzip into ~/.claude/skills/, then ask Claude Code: “Our OWASP dependency-check scan in Maven seems to pass every time and the NVD update is slow. Can you review our build and CI config and tell me what is wrong? Don’t edit anything yet.”. Needs Node 16+.
What it does not do
Reads build and CI files only; it does not run Dependency-Check, download NVD data or look up CVEs.
FAQ
Q: How is this different from asking Claude without the skill?
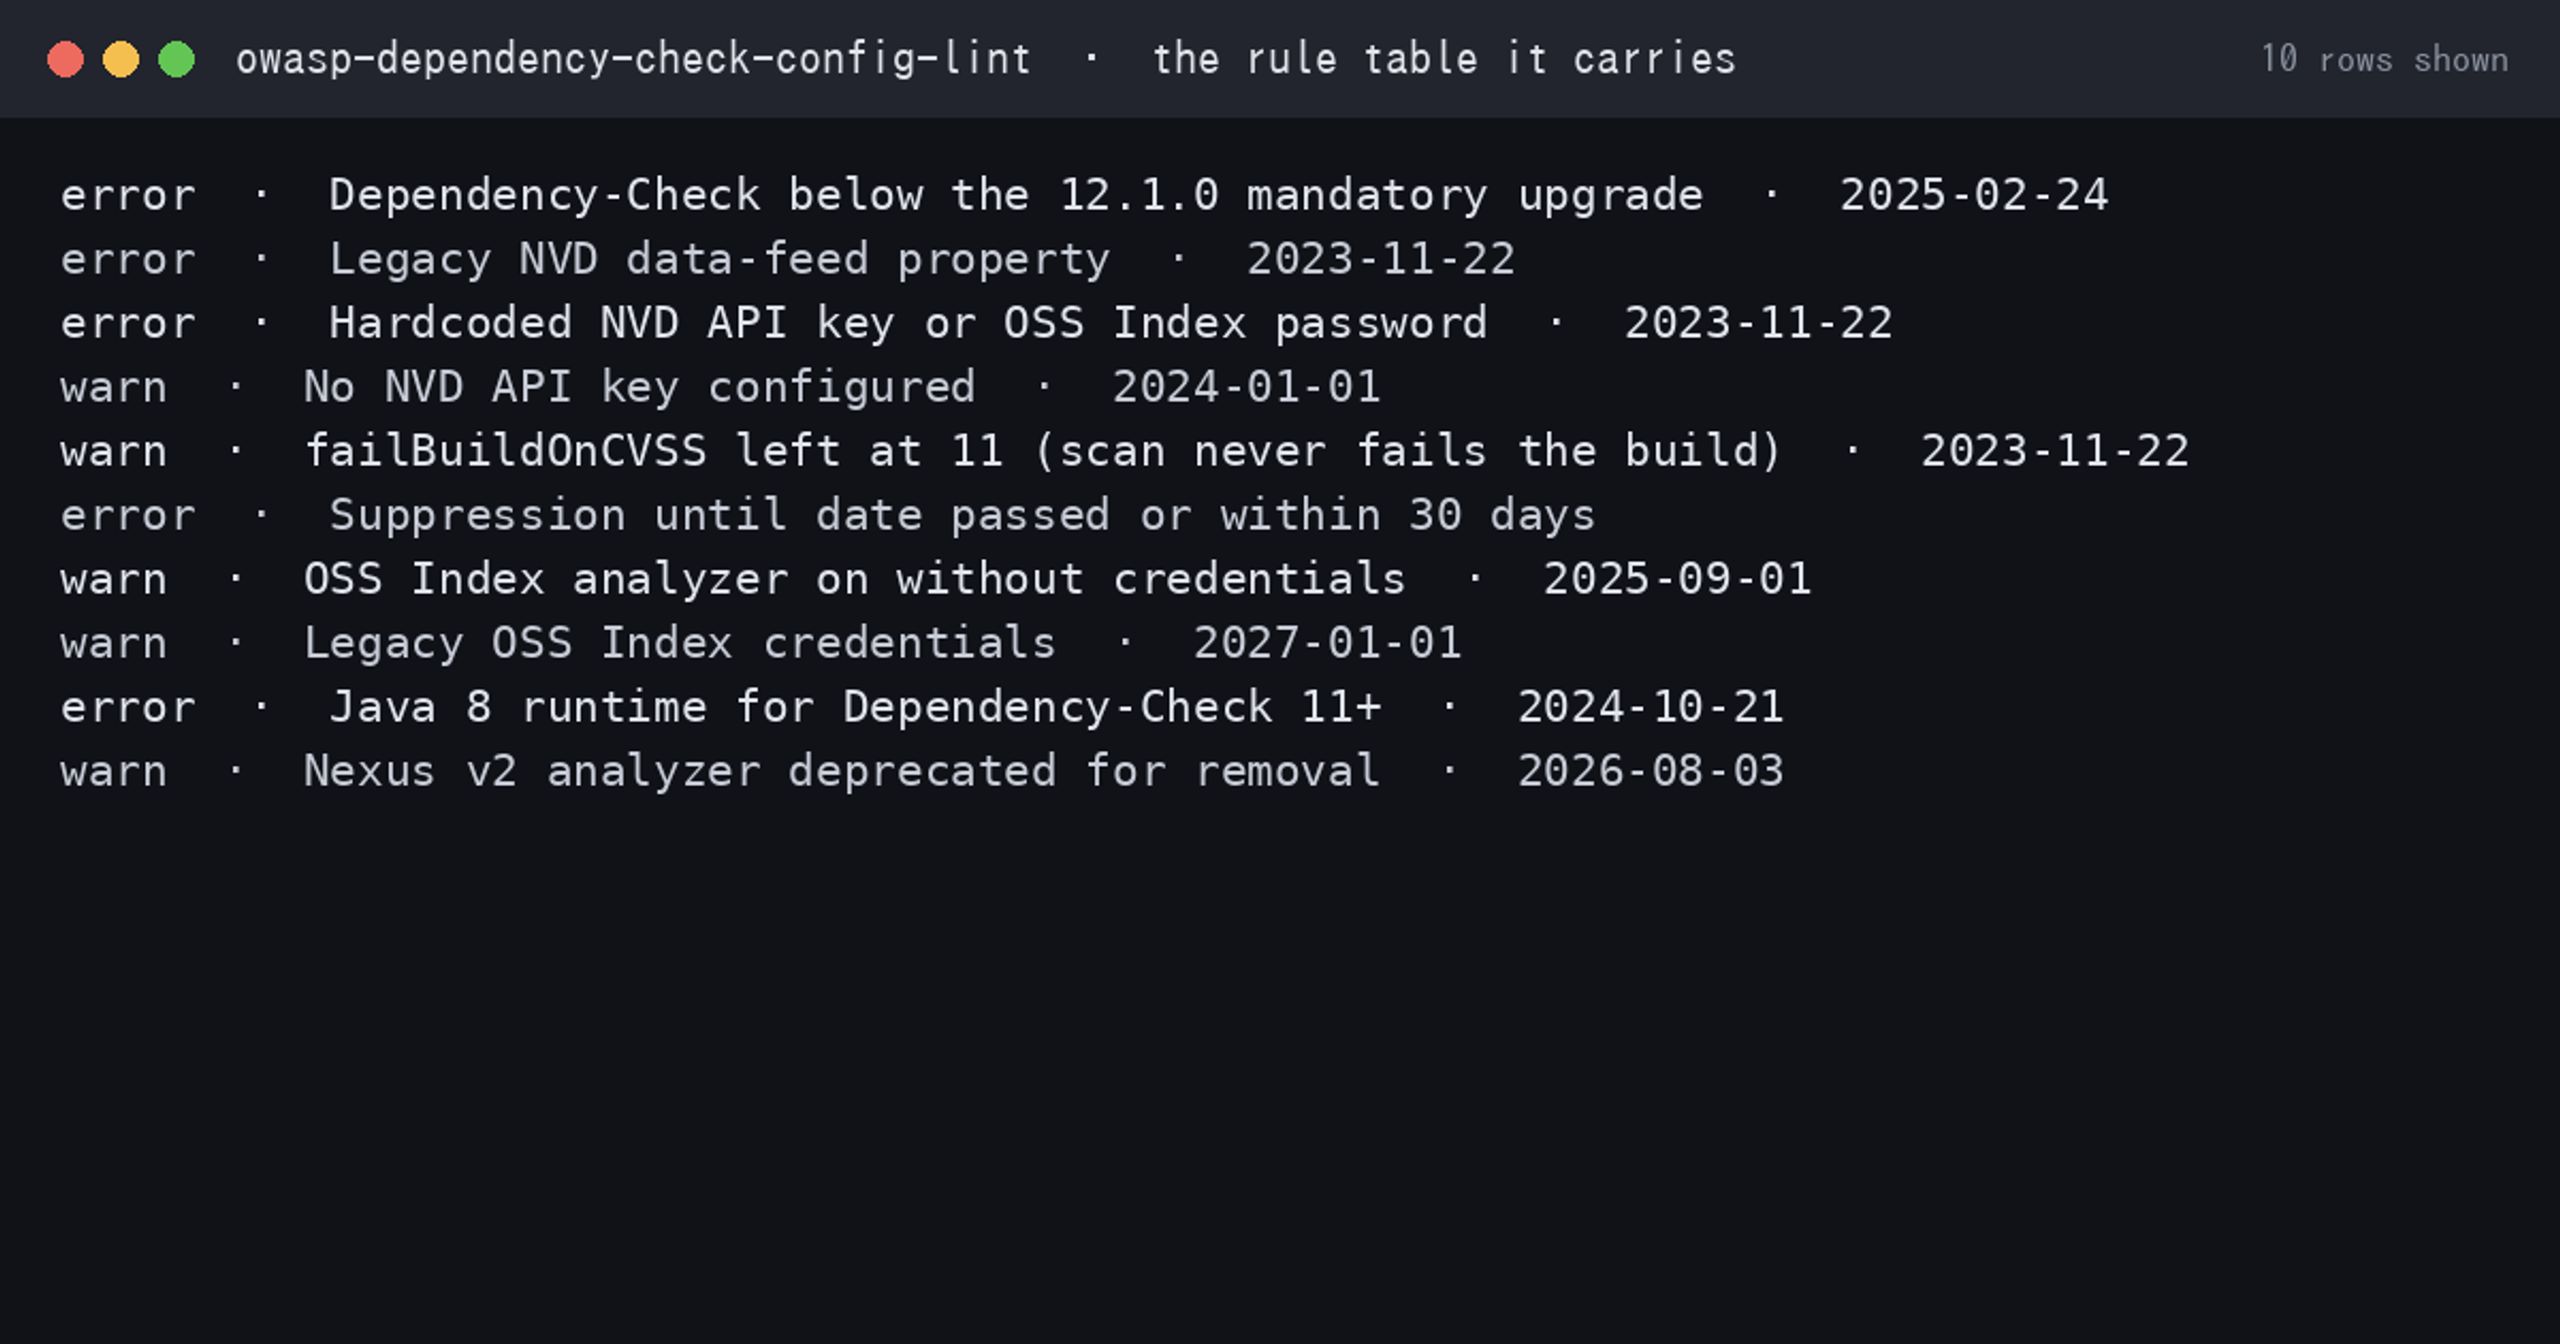
A: The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of guessing from memory.
Q: How do I get the files?
A: In your Whop library after paying: the lesson “owasp-dependency-check-config-lint.zip”.