
Rails ERB XSS audit skill for Claude Code — raw/html_safe, script-tag escaping
Finds each raw, html_safe, ‹%== and ‹script› value that skips Rails escaping
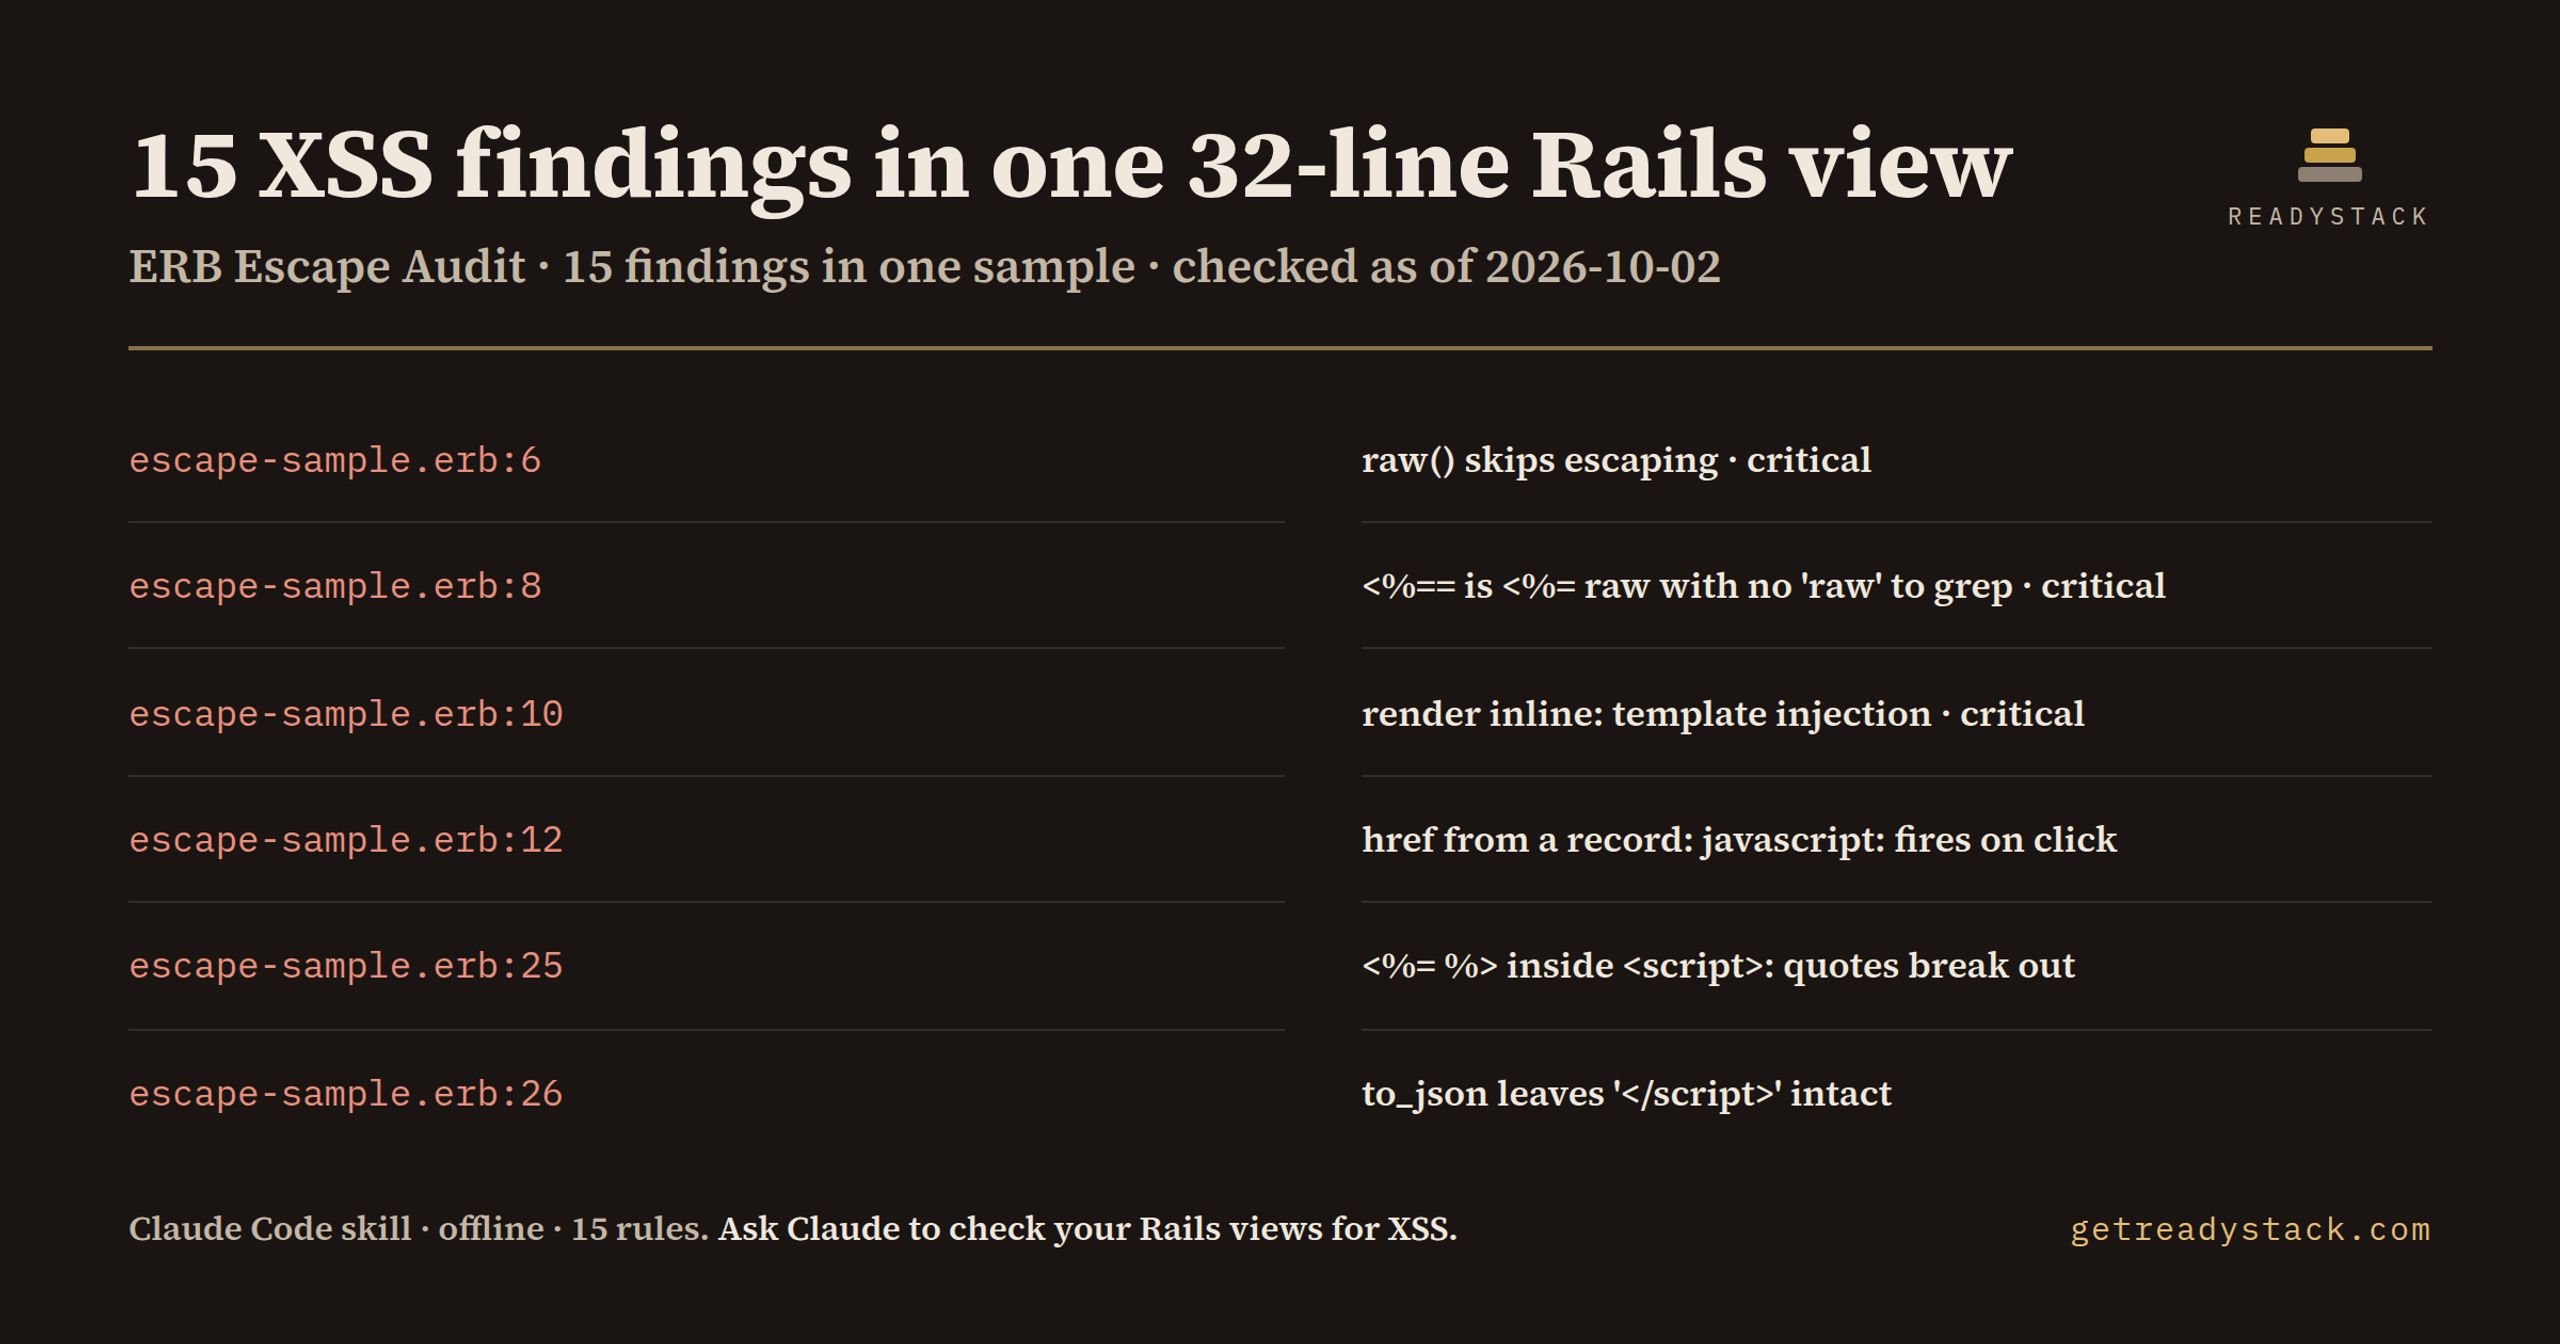
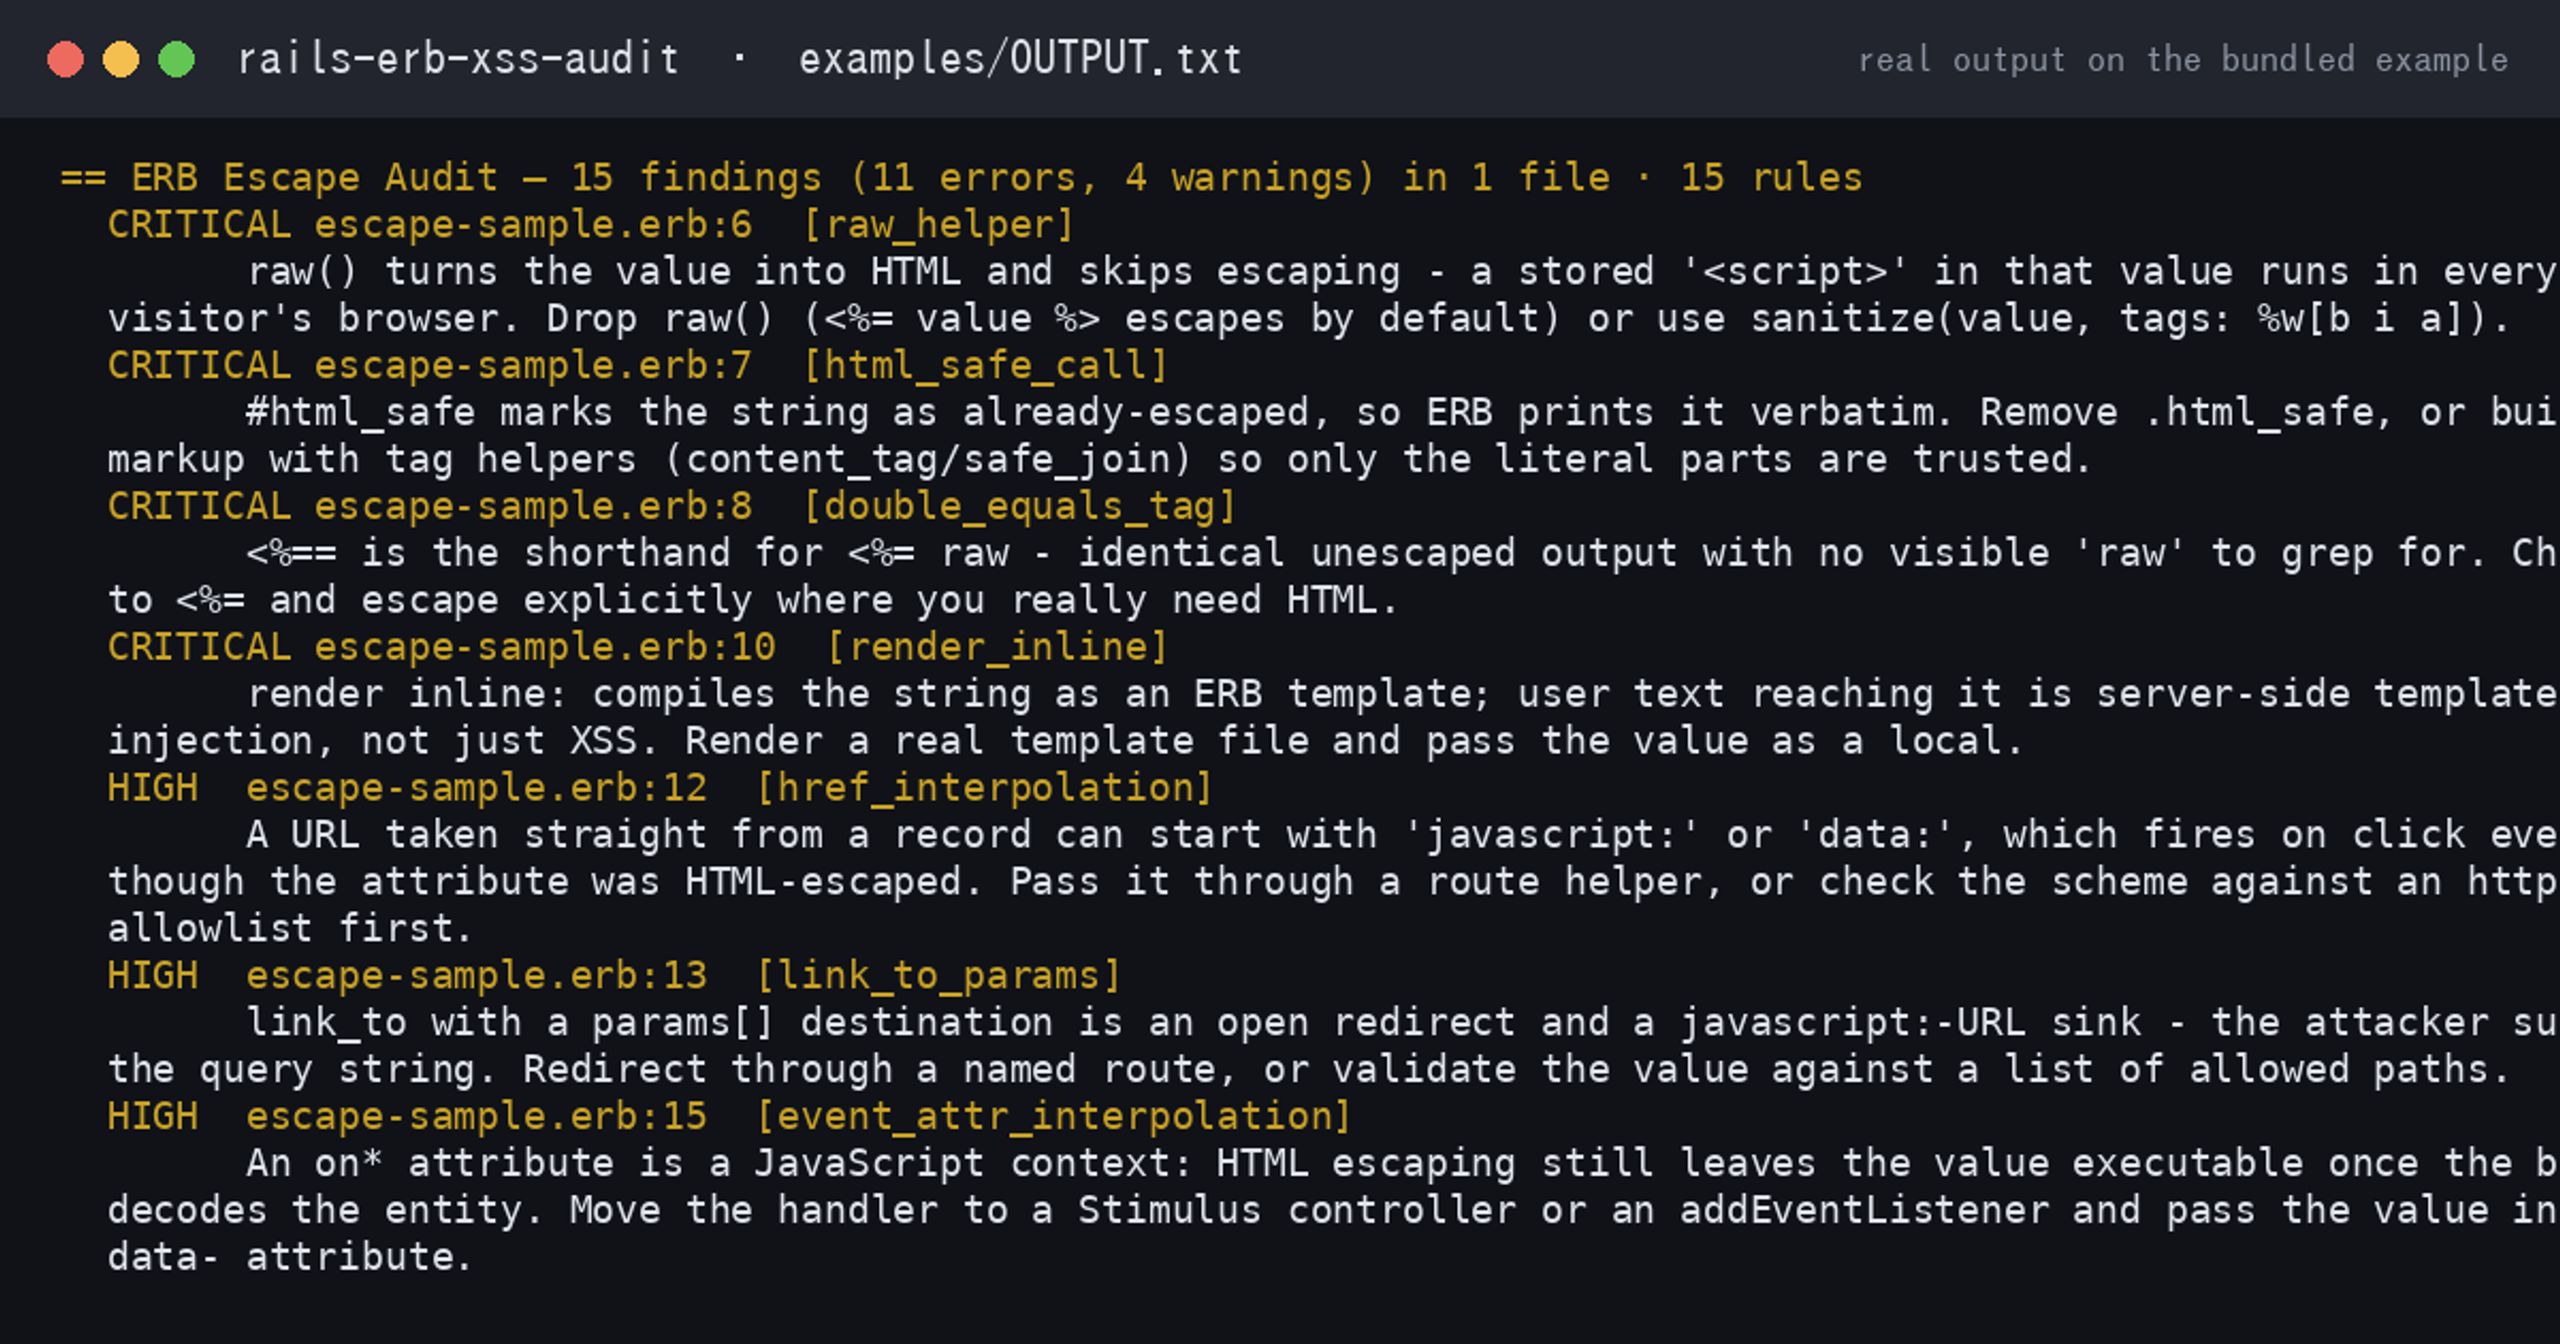
On one 32-line Rails product page it printed 15 findings (11 errors, 4 warnings) from 15 rules, each with file:line, what breaks and the replacement line.
Who it’s for
For Rails teams whose ERB views render user-supplied data.
What breaks, and when
One raw() or .html_safe on user input lets a visitor run script in your users’ sessions; on the 32-line sample page there were 11 such errors.
What you get
• A scanner Claude runs over every .erb view, partial, layout and mailer template - not a guess from memory
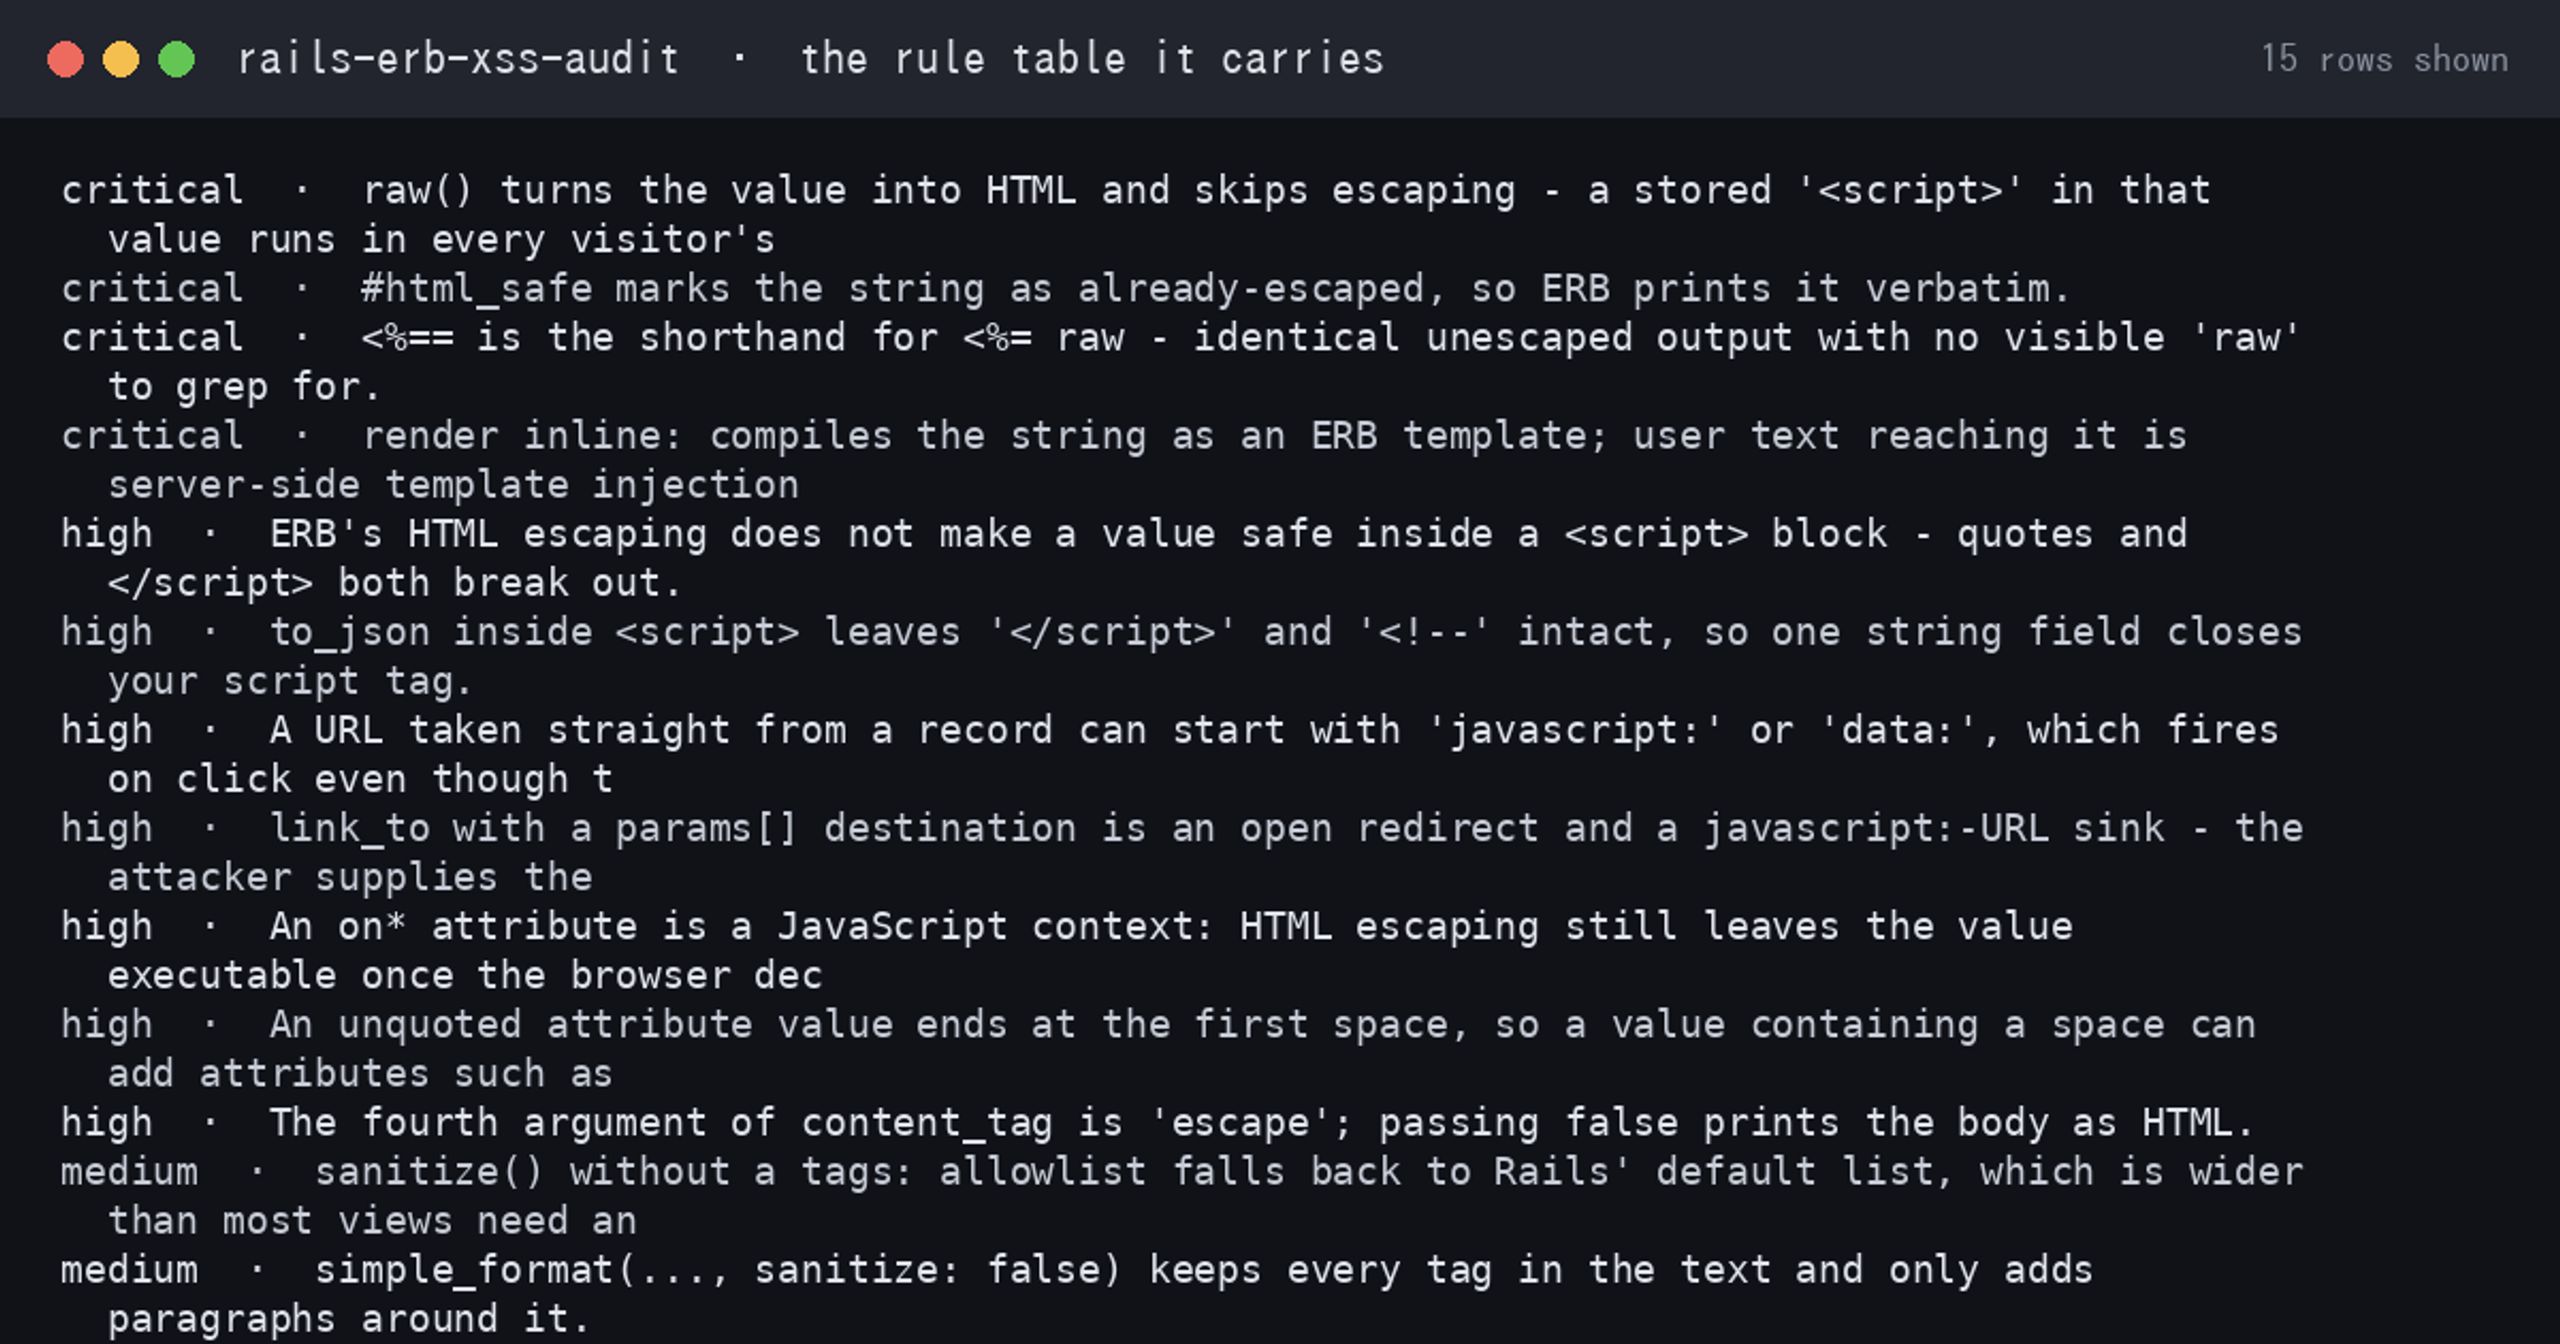
• 15 rules: raw(), .html_safe, ‹%==, render inline:, ‹script›/‹style› interpolation, to_json, href/on*…
See it first
The real output of the bundled example is on getreadystack.com/skills/rails-erb-xss-audit/ — free, no sign-up, so you see what it finds before you pay.
Install in 30 seconds
Unzip into ~/.claude/skills/, then ask Claude Code: “Can you check our Rails views for XSS? Don’t edit anything yet.”. Needs Node 16+.
What it does not do
Reads .erb files only - no Ruby helpers, Haml or Slim; it does not boot Rails or trace data flow, and it is not a replacement for Brakeman.
FAQ
Q: How is this different from asking Claude without the skill?
A: The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of guessing from memory.
Q: How do I get the files?
A: In your Whop library after paying: the lesson “rails-erb-xss-audit.zip”.