

Security Headers Skill for Claude
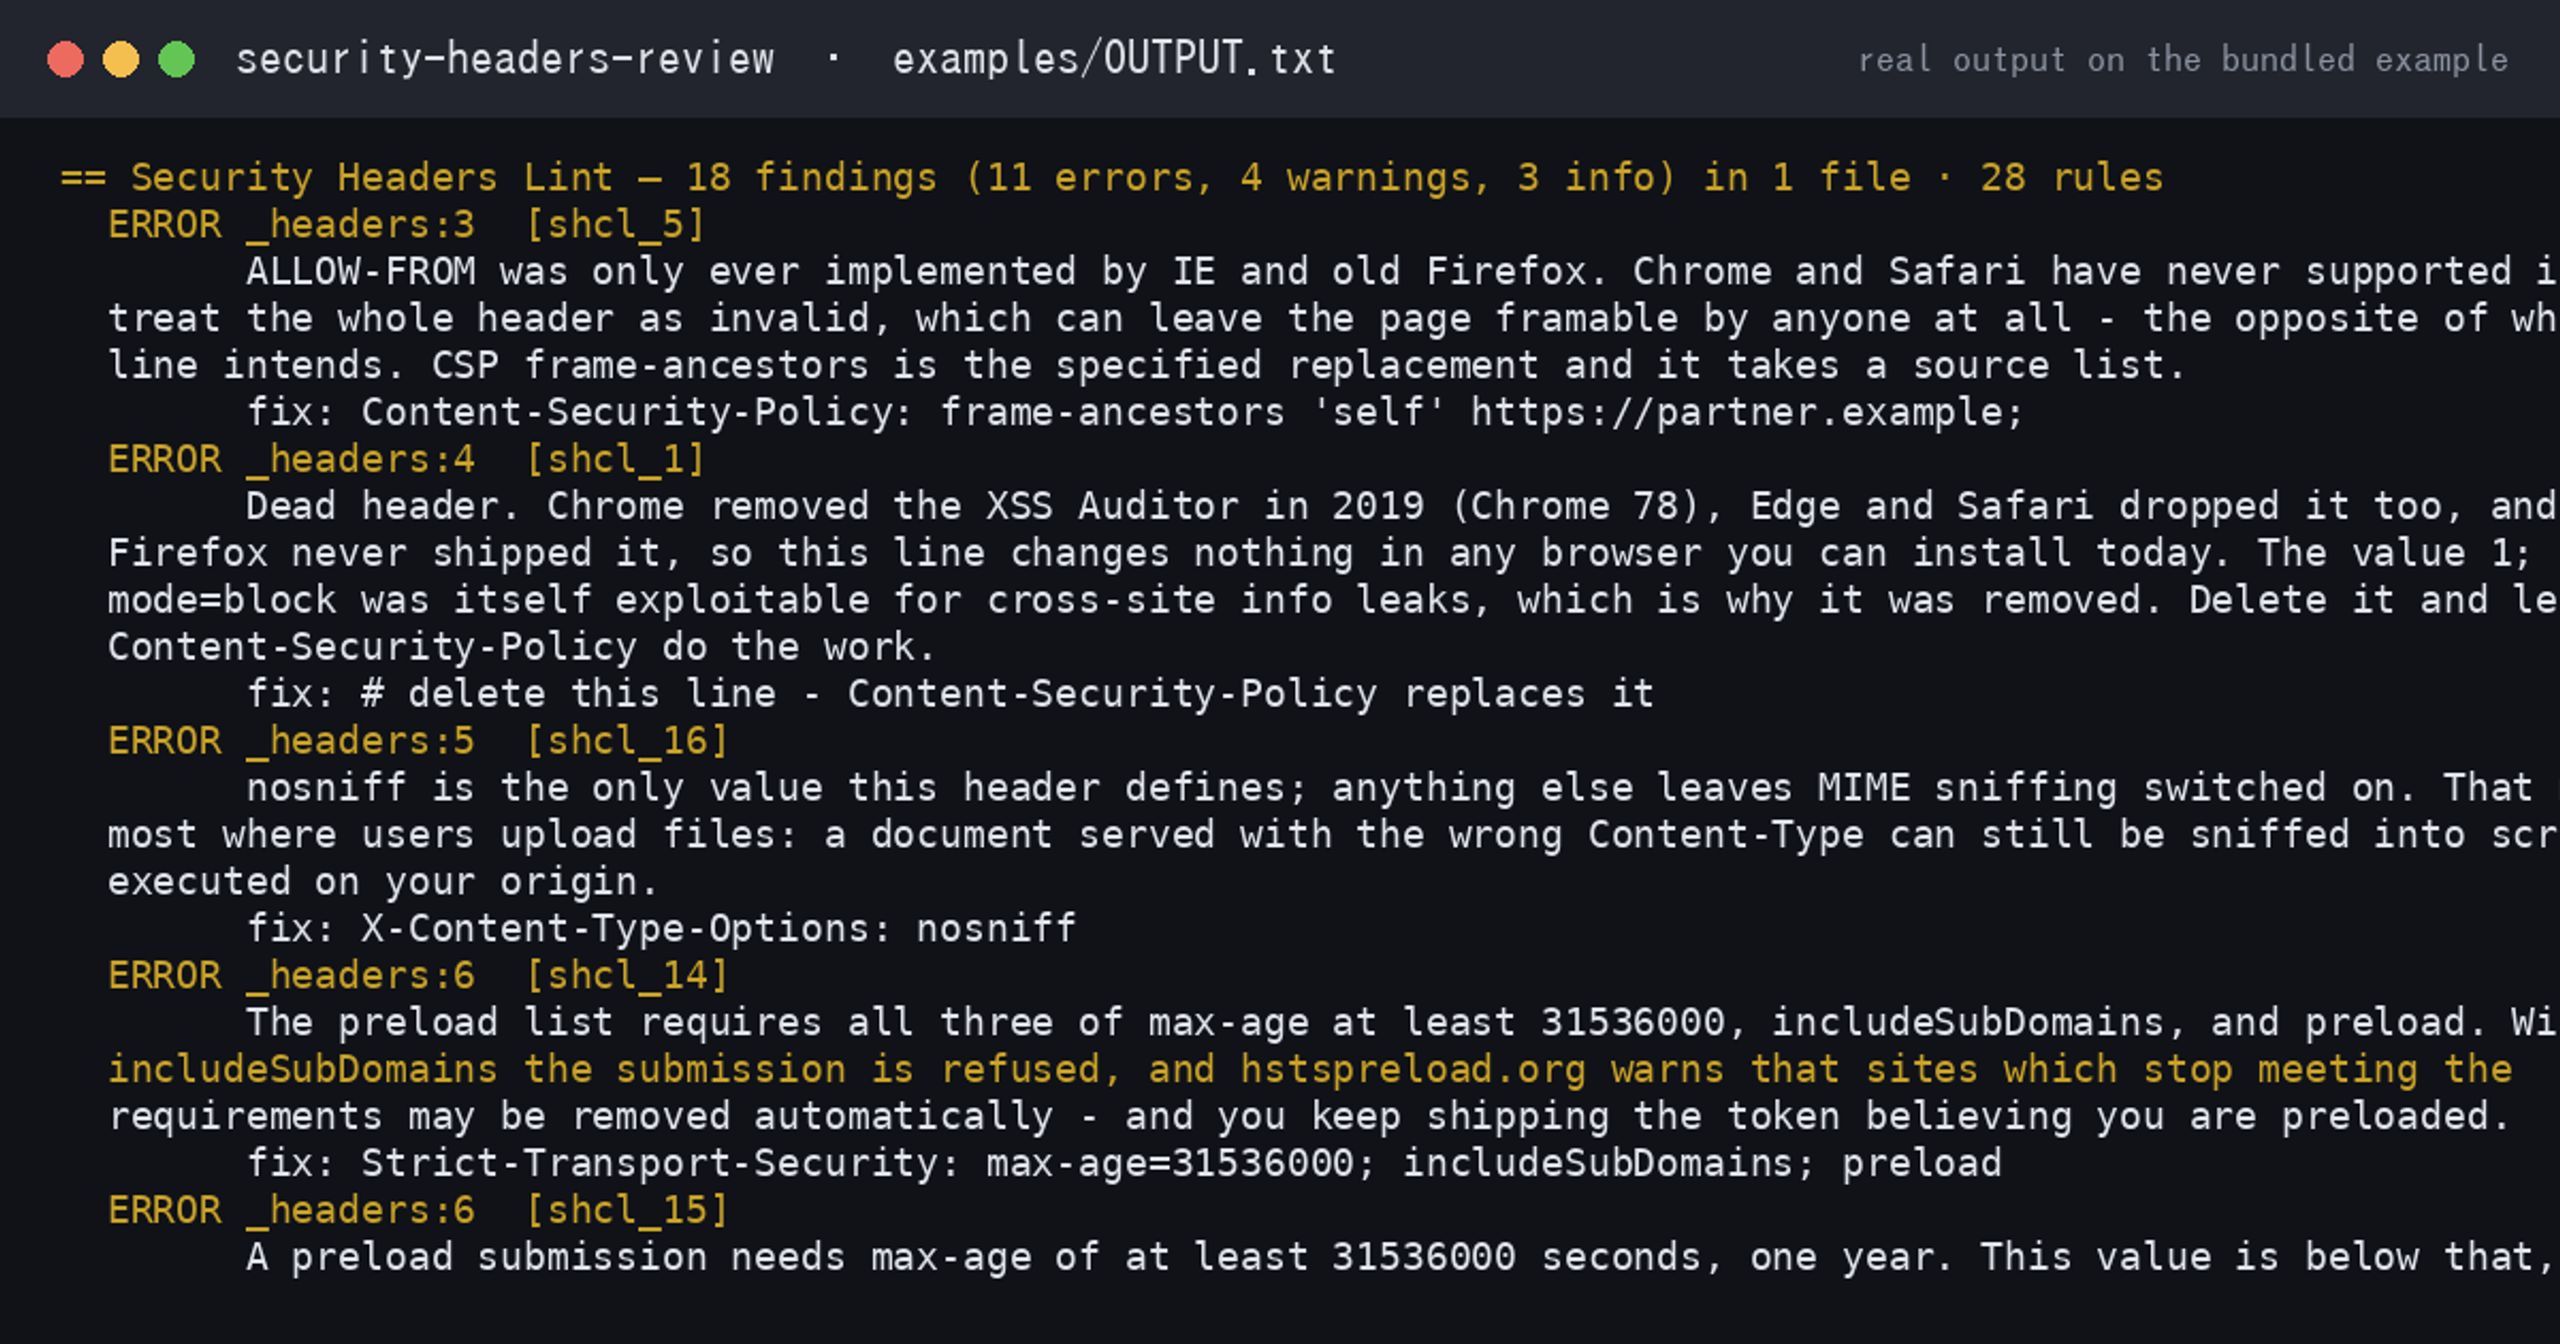
18 header findings in one _headers file, each with file:line and the reason
On the bundled sample: 18 findings (11 errors, 4 warnings, 3 info) in 1 file from 28 rules, including ALLOW-FROM, X-XSS-Protection, an unquoted CSP self and a hard-coded nonce.
Who it’s for
For developers who set security headers in a _headers file, nginx, Apache or a framework config.
What breaks, and when
Chrome removed the XSS Auditor in 2019 (Chrome 78) and HPKP in 2019 (Chrome 72), and stopped enforcing Expect-CT in 2022 — these lines still look like protection and protect nothing.
What you get
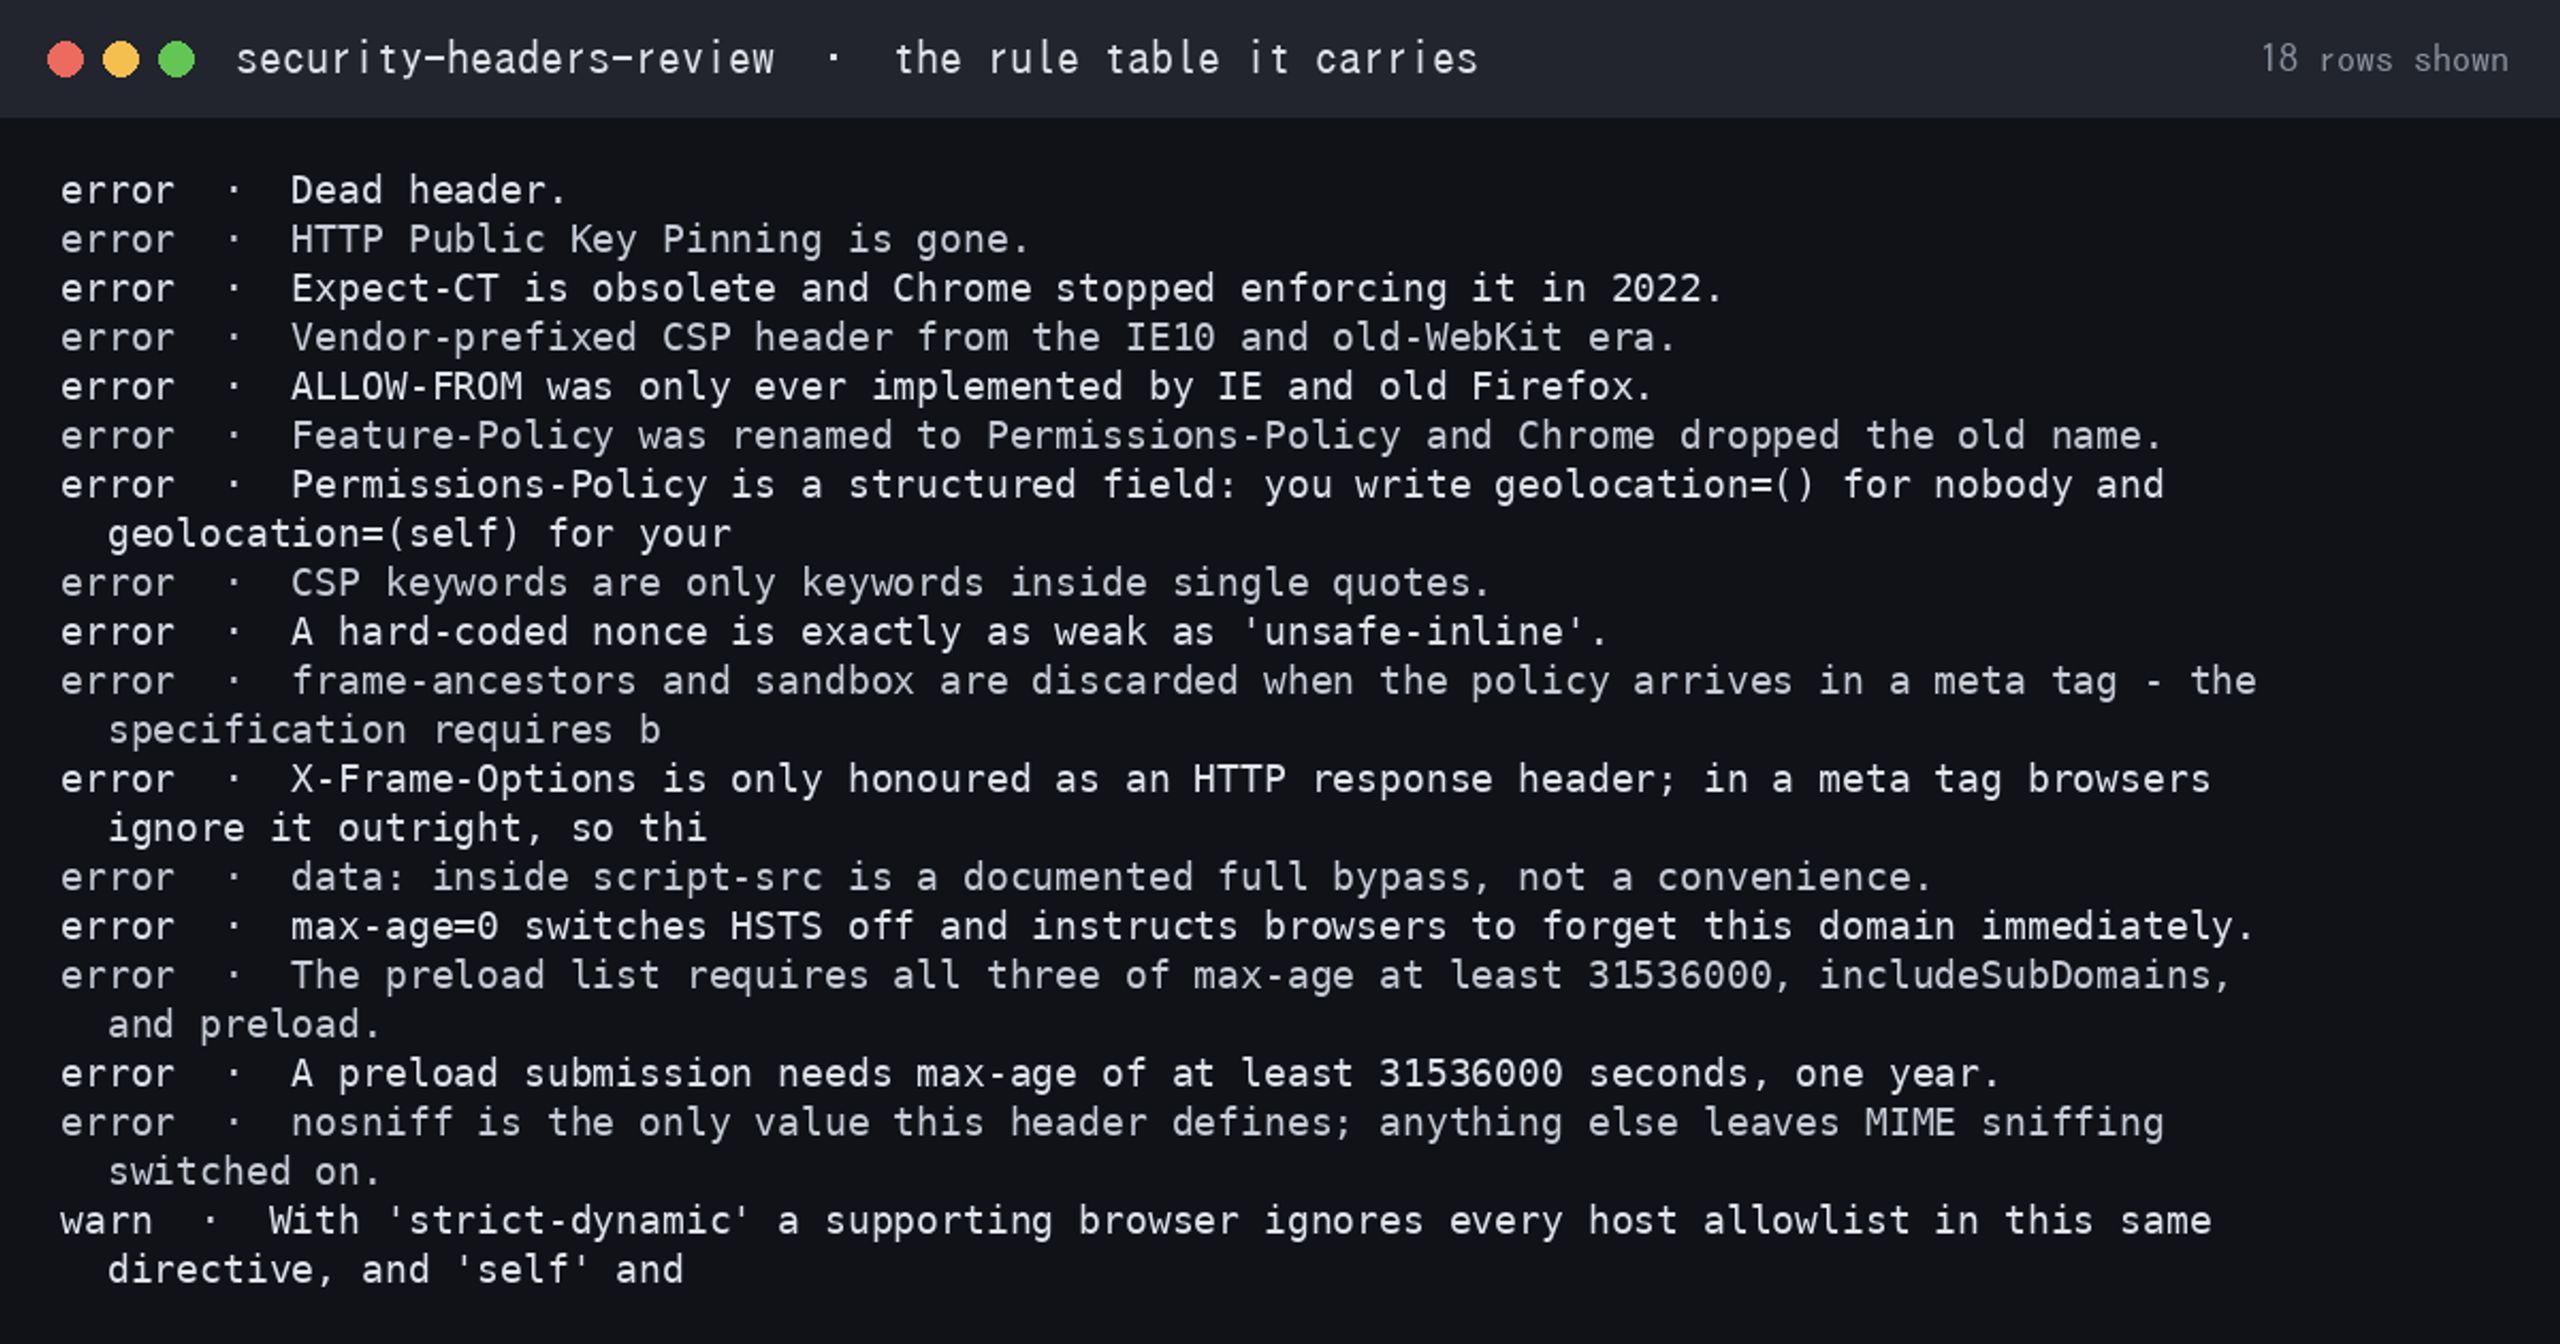
• SKILL.md, an offline Node scanner (scripts/scan.js) and the 28-rule table
• file:line, severity and why the browser ignores or weakens each header
See it first
The real output of the bundled example is on getreadystack.com/skills/security-headers-review/ — free, no sign-up, so you see what it finds before you pay.
Install in 30 seconds
Unzip into ~/.claude/skills/, then ask Claude Code: “Review the security headers in this repo. Is anything obsolete or not actually enforced? Don’t edit anything yet.”. Needs Node 16+.
What it does not do
It does not fetch your live site or see headers set by a CDN or app code; no network calls, no edits without your OK.
FAQ
Q: How is this different from asking Claude without the skill?
A: The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of guessing from memory.
Q: How do I get the files?
A: In your Whop library after paying: the lesson “security-headers-review.zip”.