
TLS cert validity Skill for Claude
Flags cert scripts, Terraform and cert-manager values that break under SC-081v3
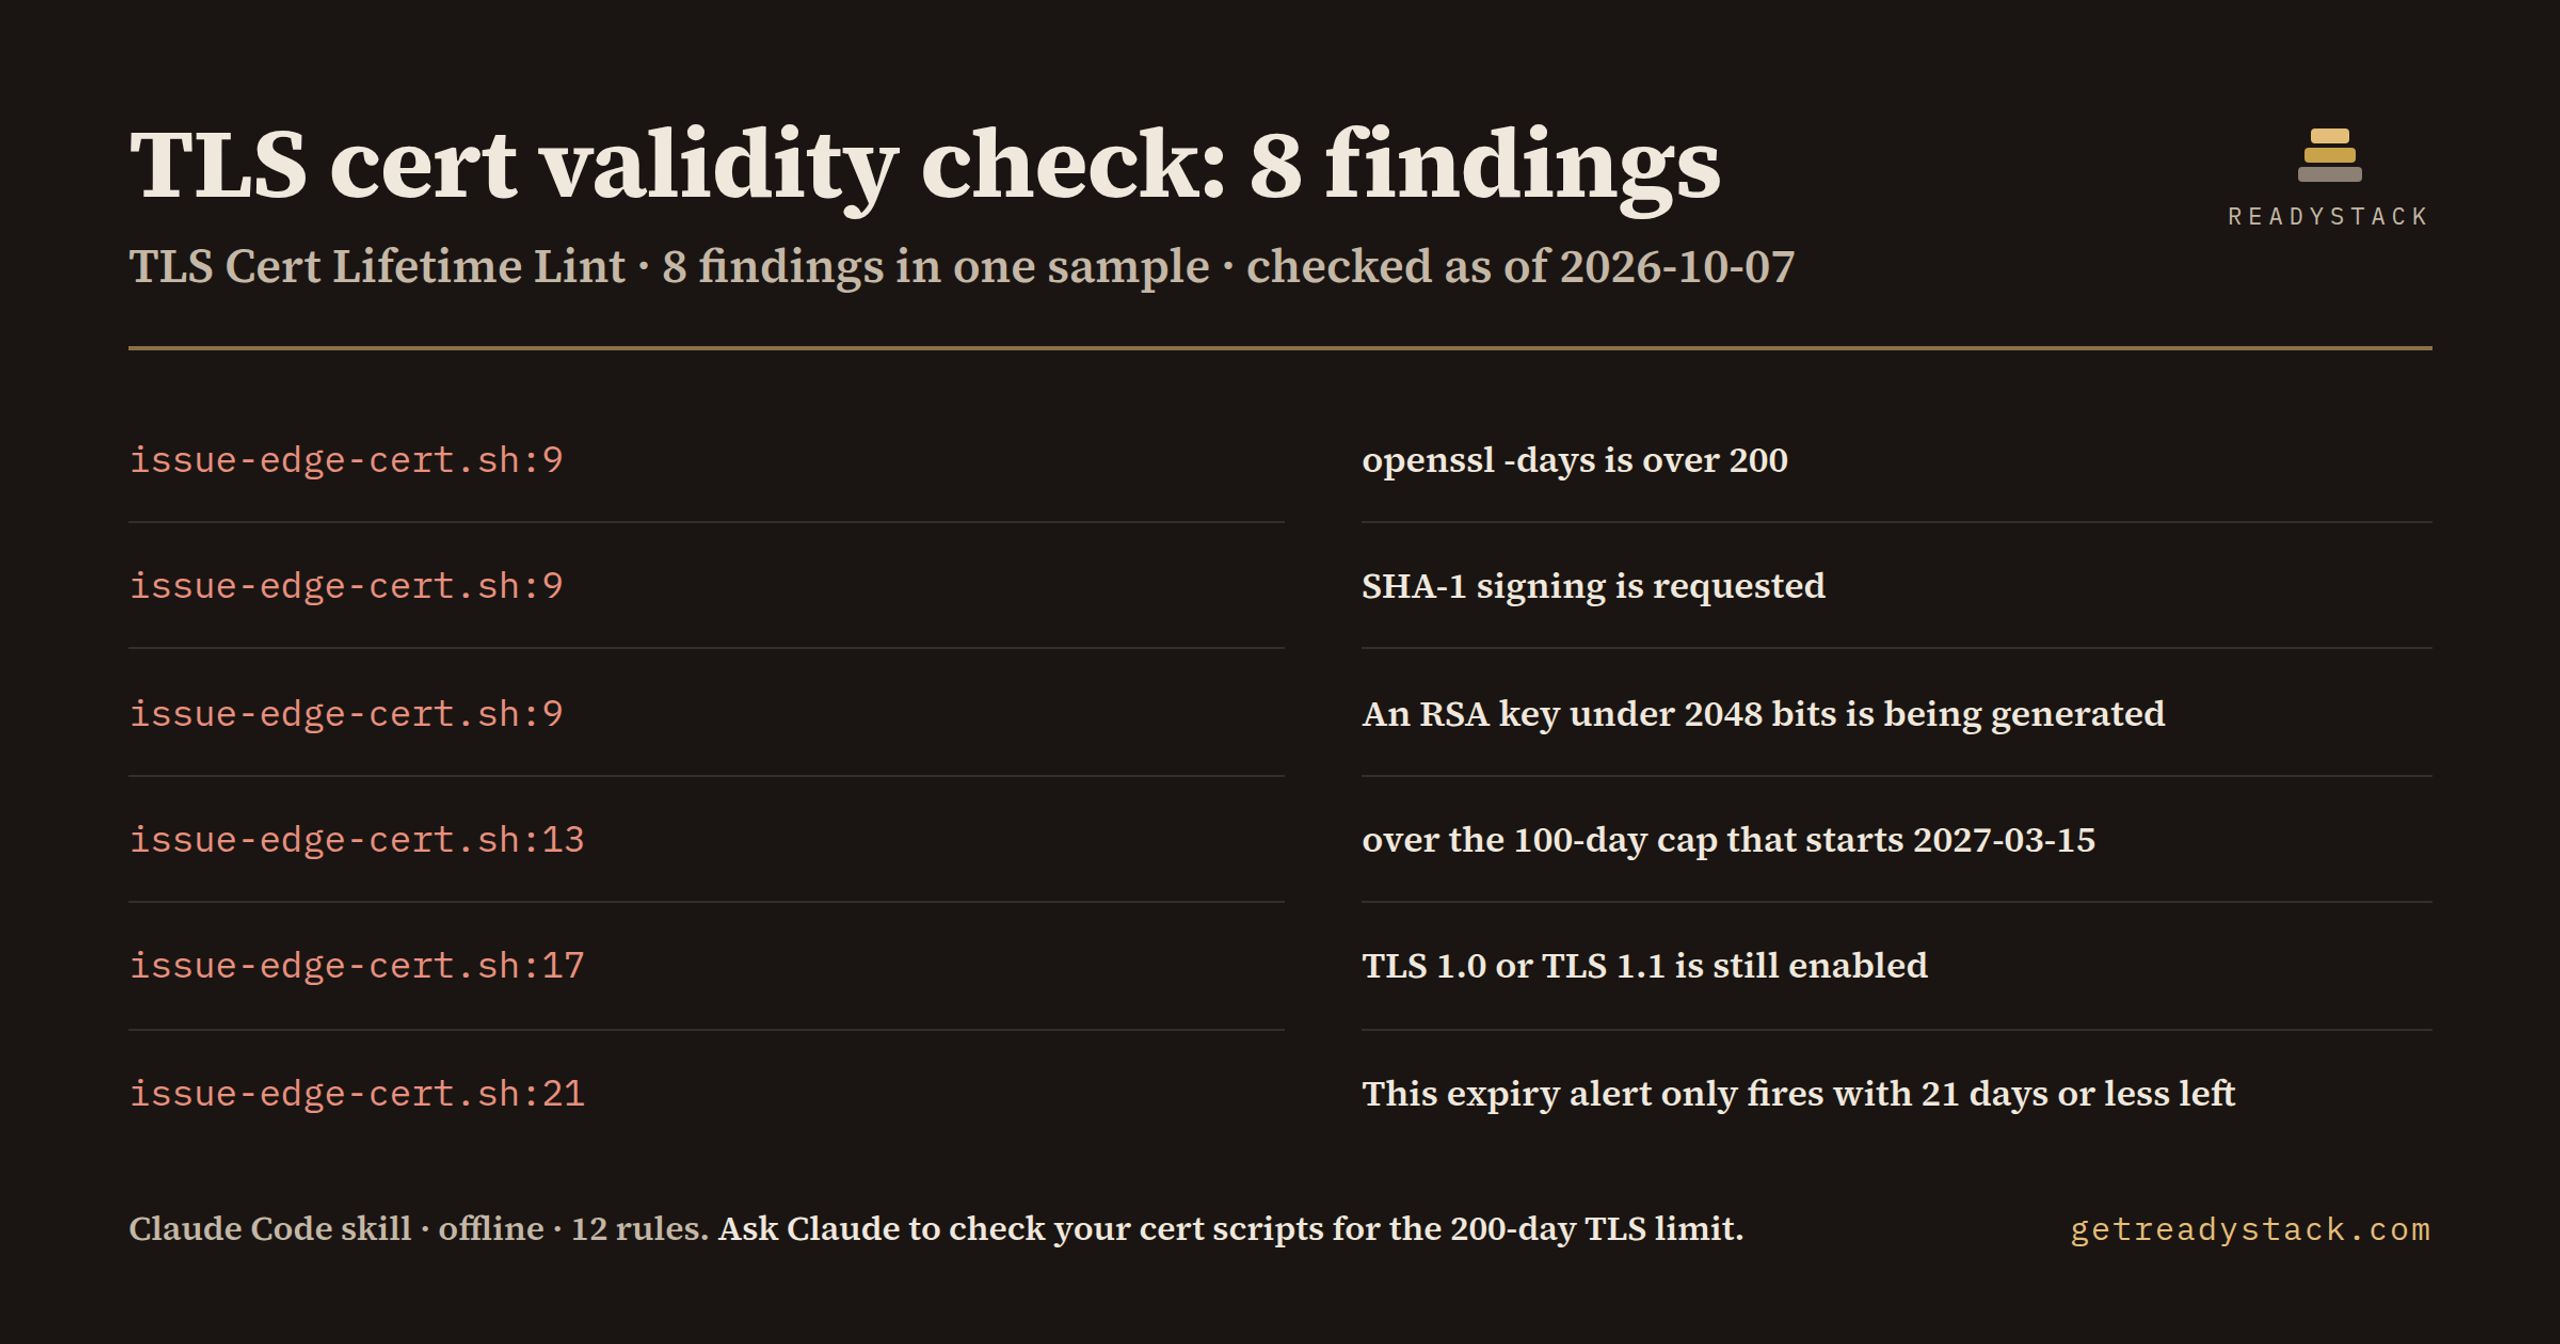
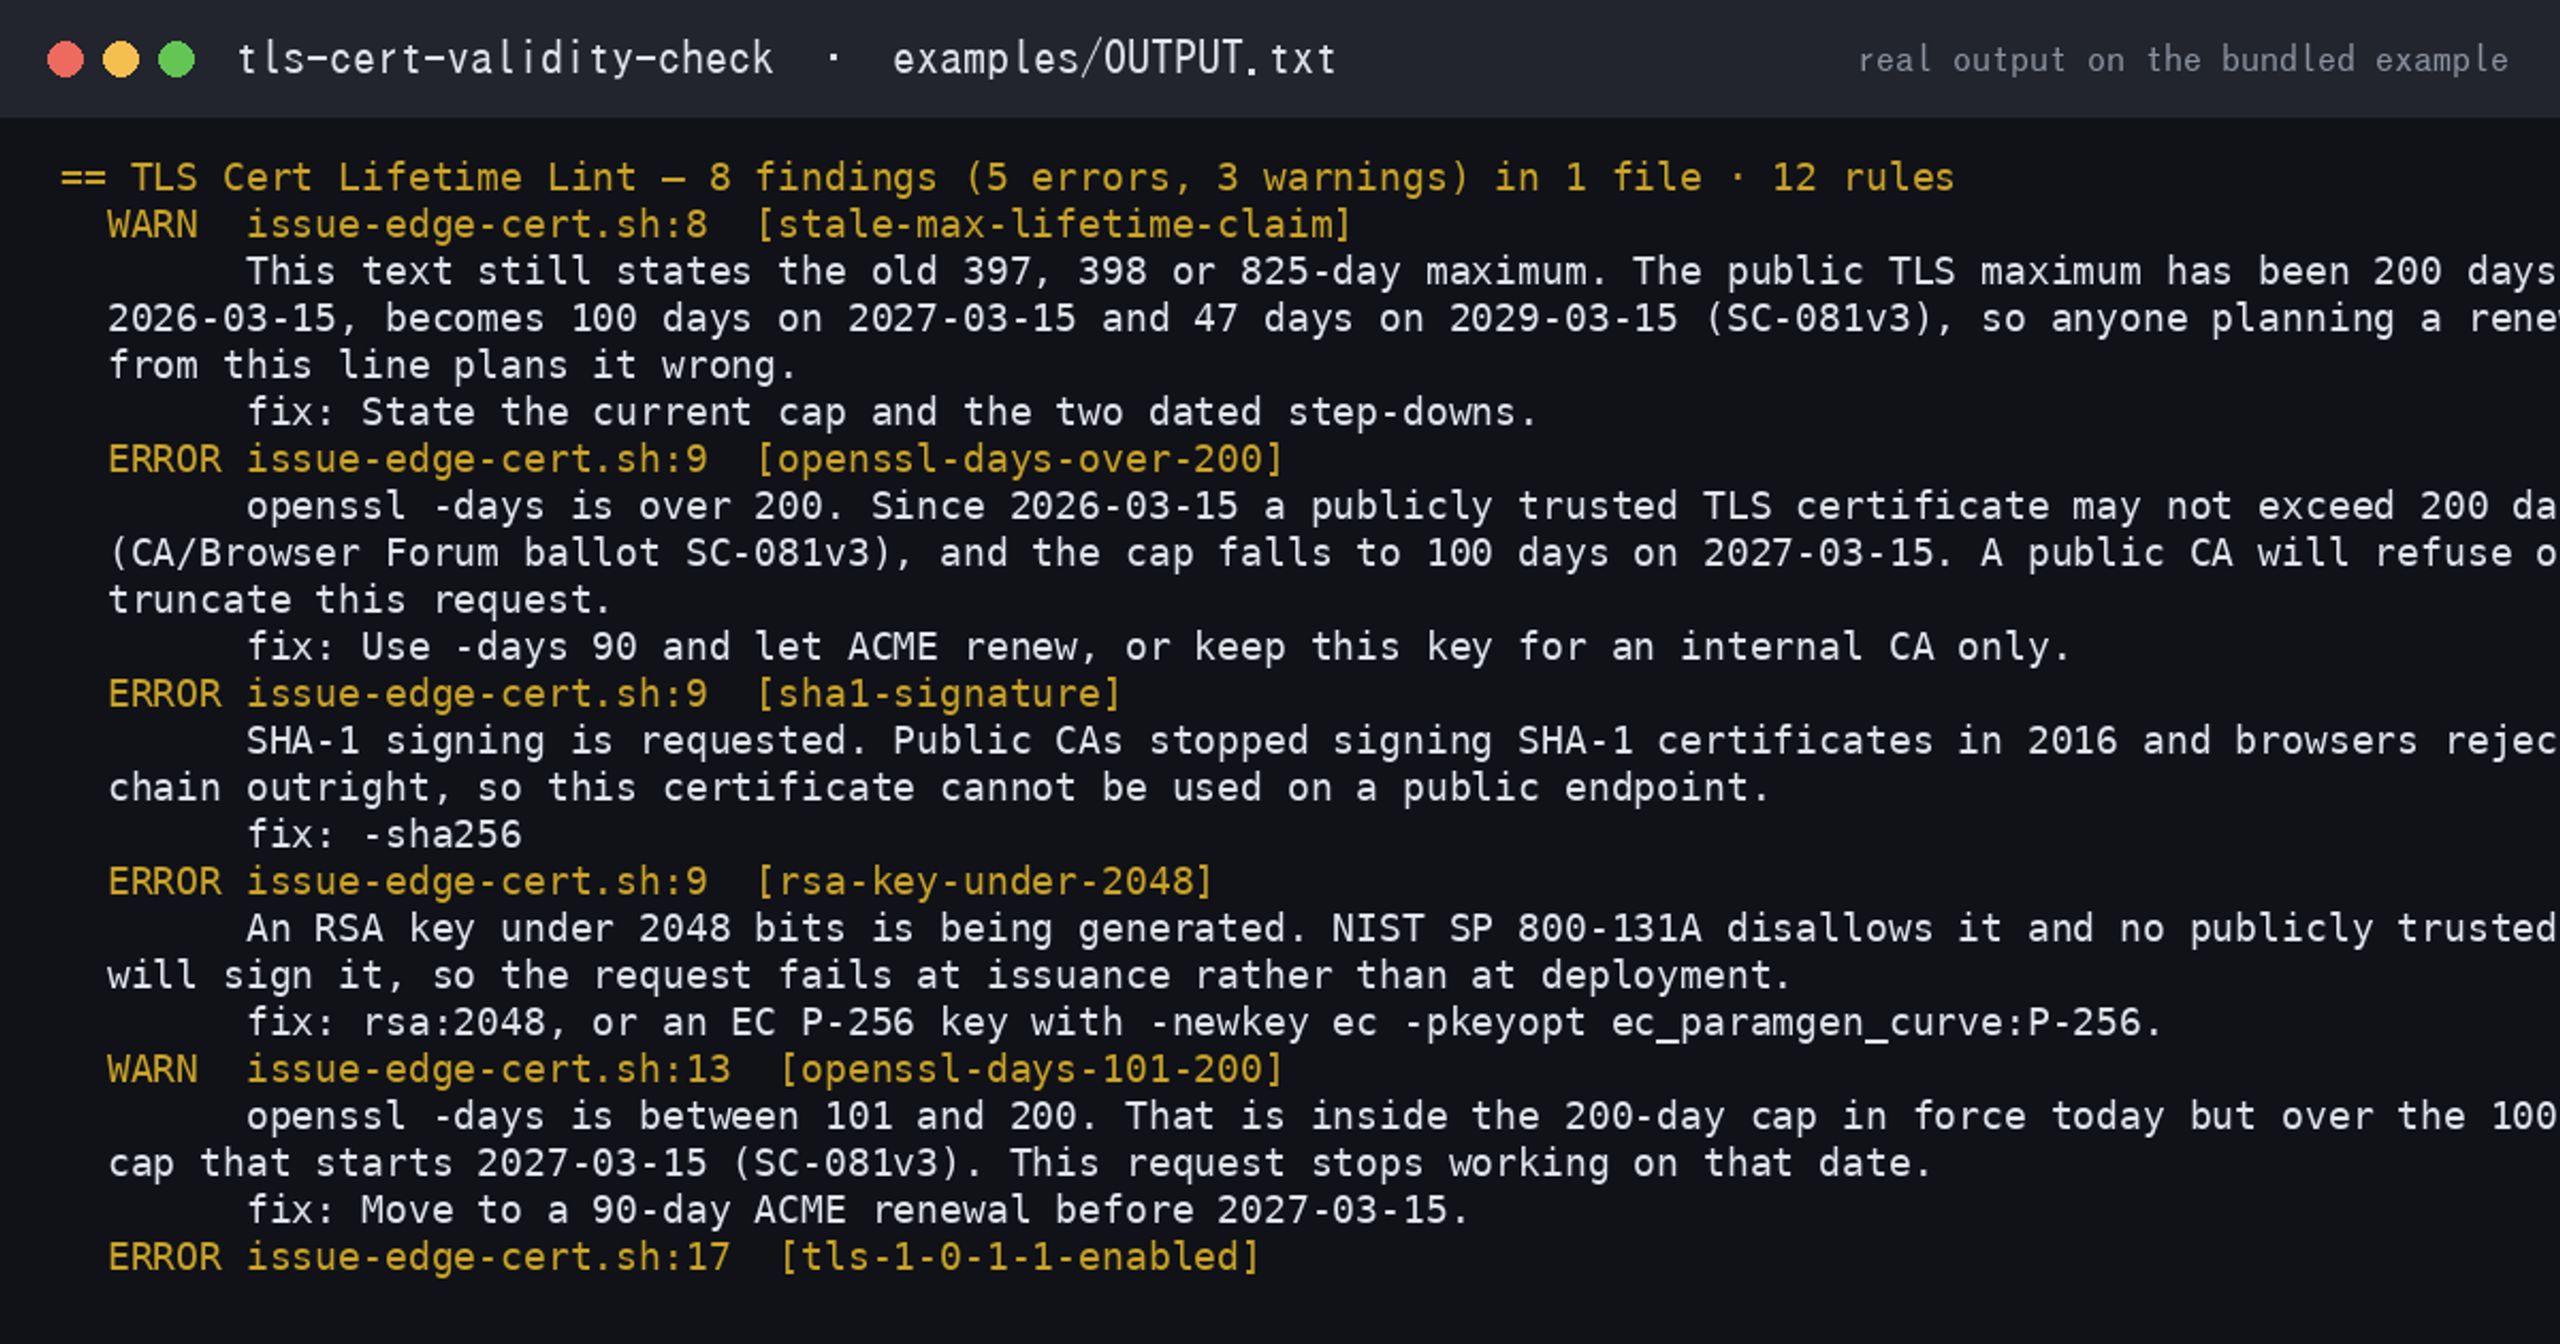
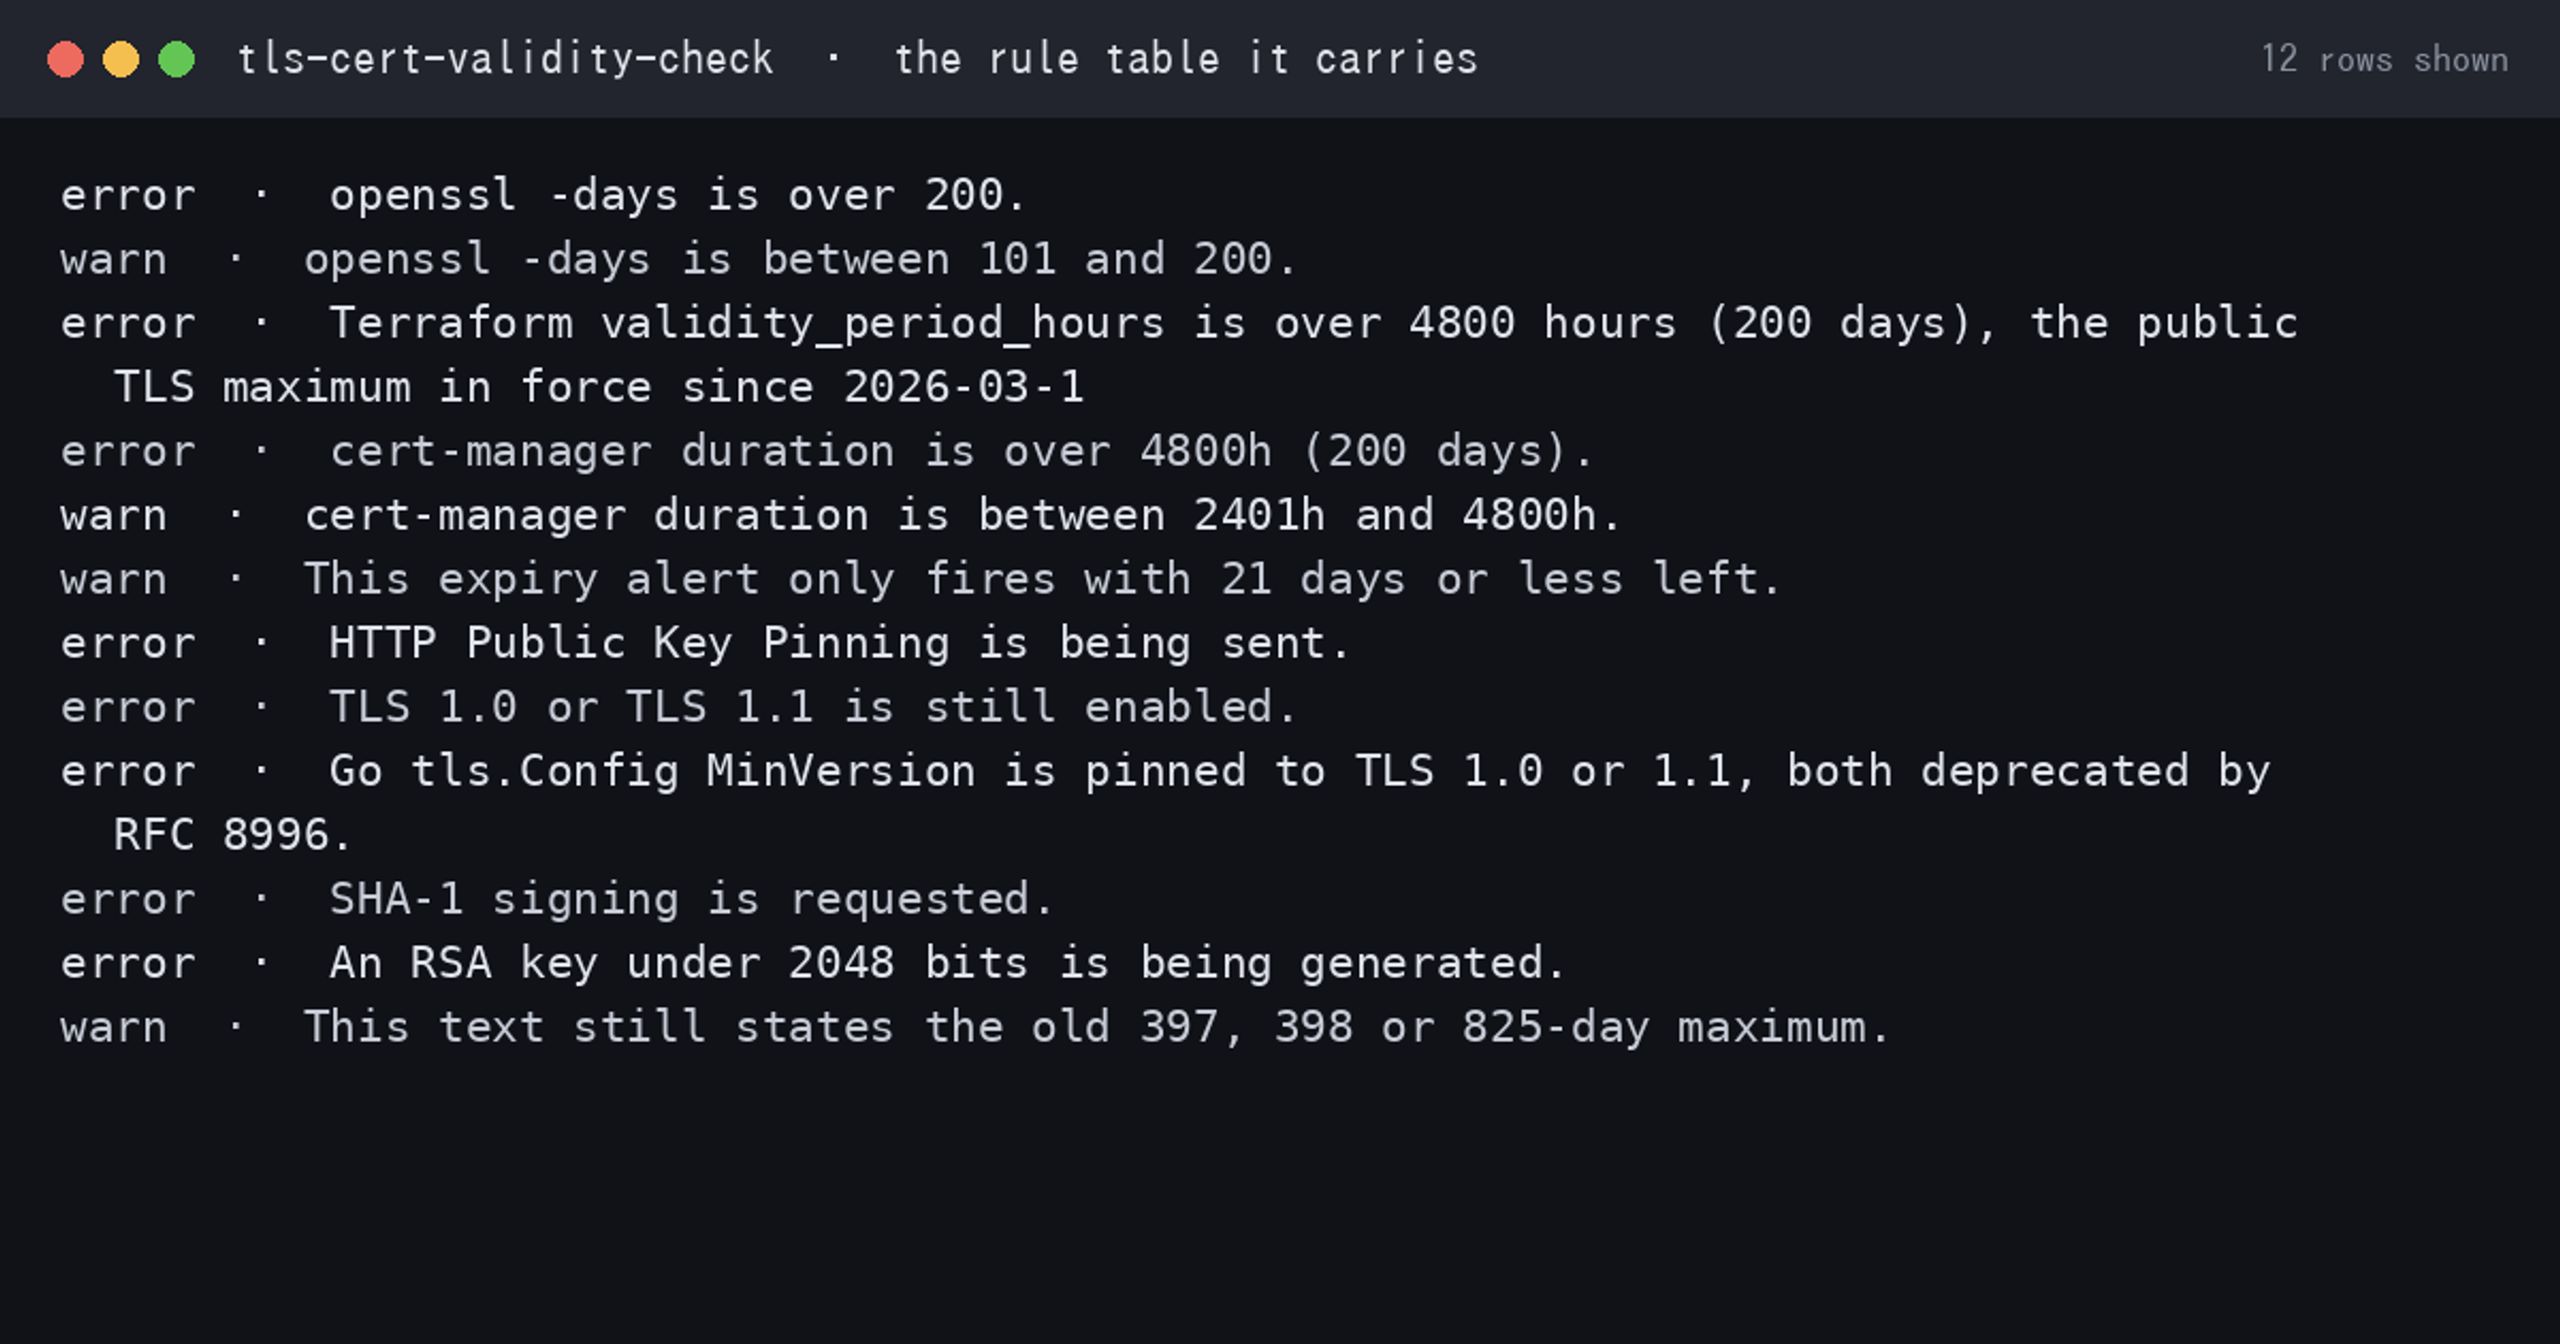
On one 22-line shell script it printed 8 findings (5 errors, 3 warnings) from 12 rules, each with file:line, what breaks, the date and the fix.
Who it’s for
For DevOps and platform engineers who issue TLS certificates from shell scripts, Terraform or cert-manager and own the renewal pipeline.
What breaks, and when
Since 2026-03-15 a public TLS certificate may not exceed 200 days, and on 2027-03-15 the cap falls to 100 days (SC-081v3): openssl -days 365 is refused or truncated.
What you get
• A scanner Claude runs over every .sh, .tf, .yaml, .conf, .go and .md file -…
See it first
The real output of the bundled example is on getreadystack.com/skills/tls-cert-validity-check/ — free, no sign-up, so you see what it finds before you pay.
Install in 30 seconds
Unzip into ~/.claude/skills/, then ask Claude Code: “Can you check whether our certificate scripts and cert-manager config will break with the new shorter TLS certificate validity periods? Don’t edit anything yet.”. Needs Node 16+.
What it does not do
No network calls; it checks the settings written in your repo, not the certificate a server is serving.
FAQ
Q: How is this different from asking Claude without the skill?
A: The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of guessing from memory.
Q: How do I get the files?
A: In your Whop library after paying: the lesson “tls-cert-validity-check.zip”.