
AuditLight
$79/ month
14 day trialRun the assessment, hand over the report, prove the fixes held.
Anyone can run six CLI tools. The hard part is turning their output into a document a client or auditor accepts, without taking production down — then proving the fixes held.
Features
- Nine built-in checks (ports, banners, HTTP, headers, TLS, DNS/email, subdomains, credential exposure, version signatures); nuclei, testssl.sh, lynis, nmap add depth if present
- Never exploits: no exploitation, brute force, DoS or fuzzing — a permanent boundary. Safe on production
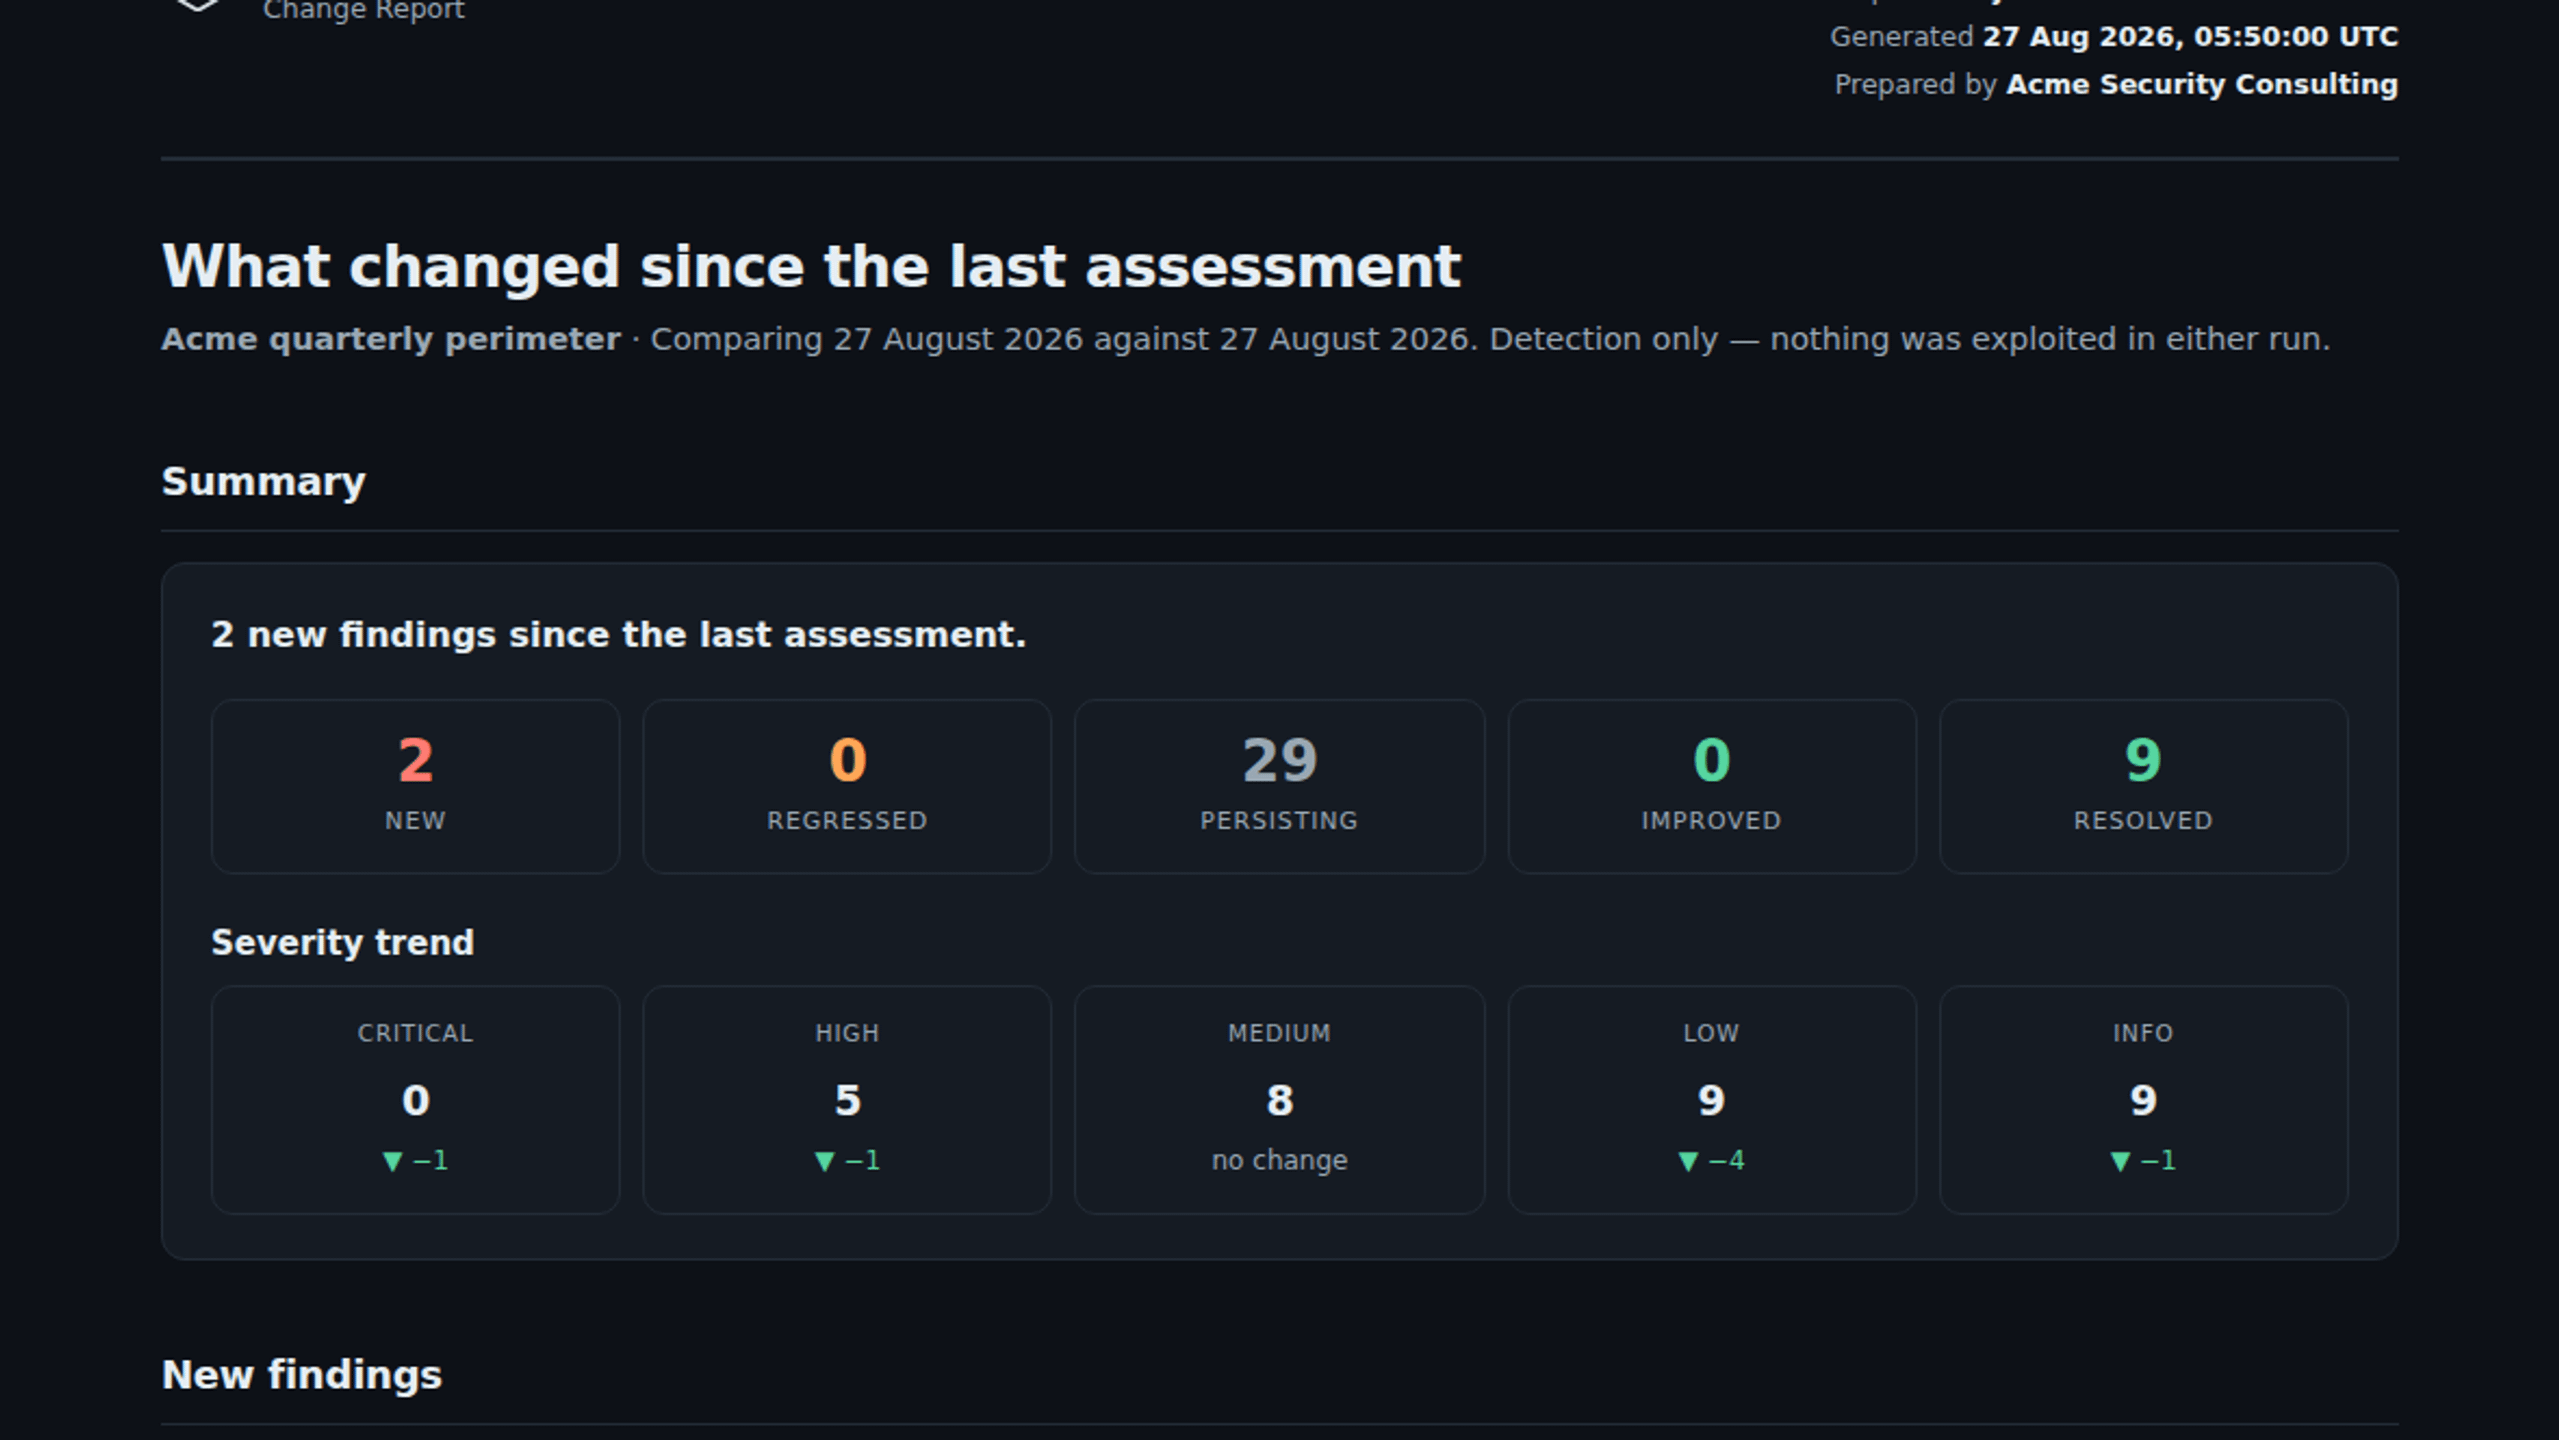
- Three HTML reports (print to PDF): Assessment, Process (every check and skip, why), Change (new/regressed/resolved)
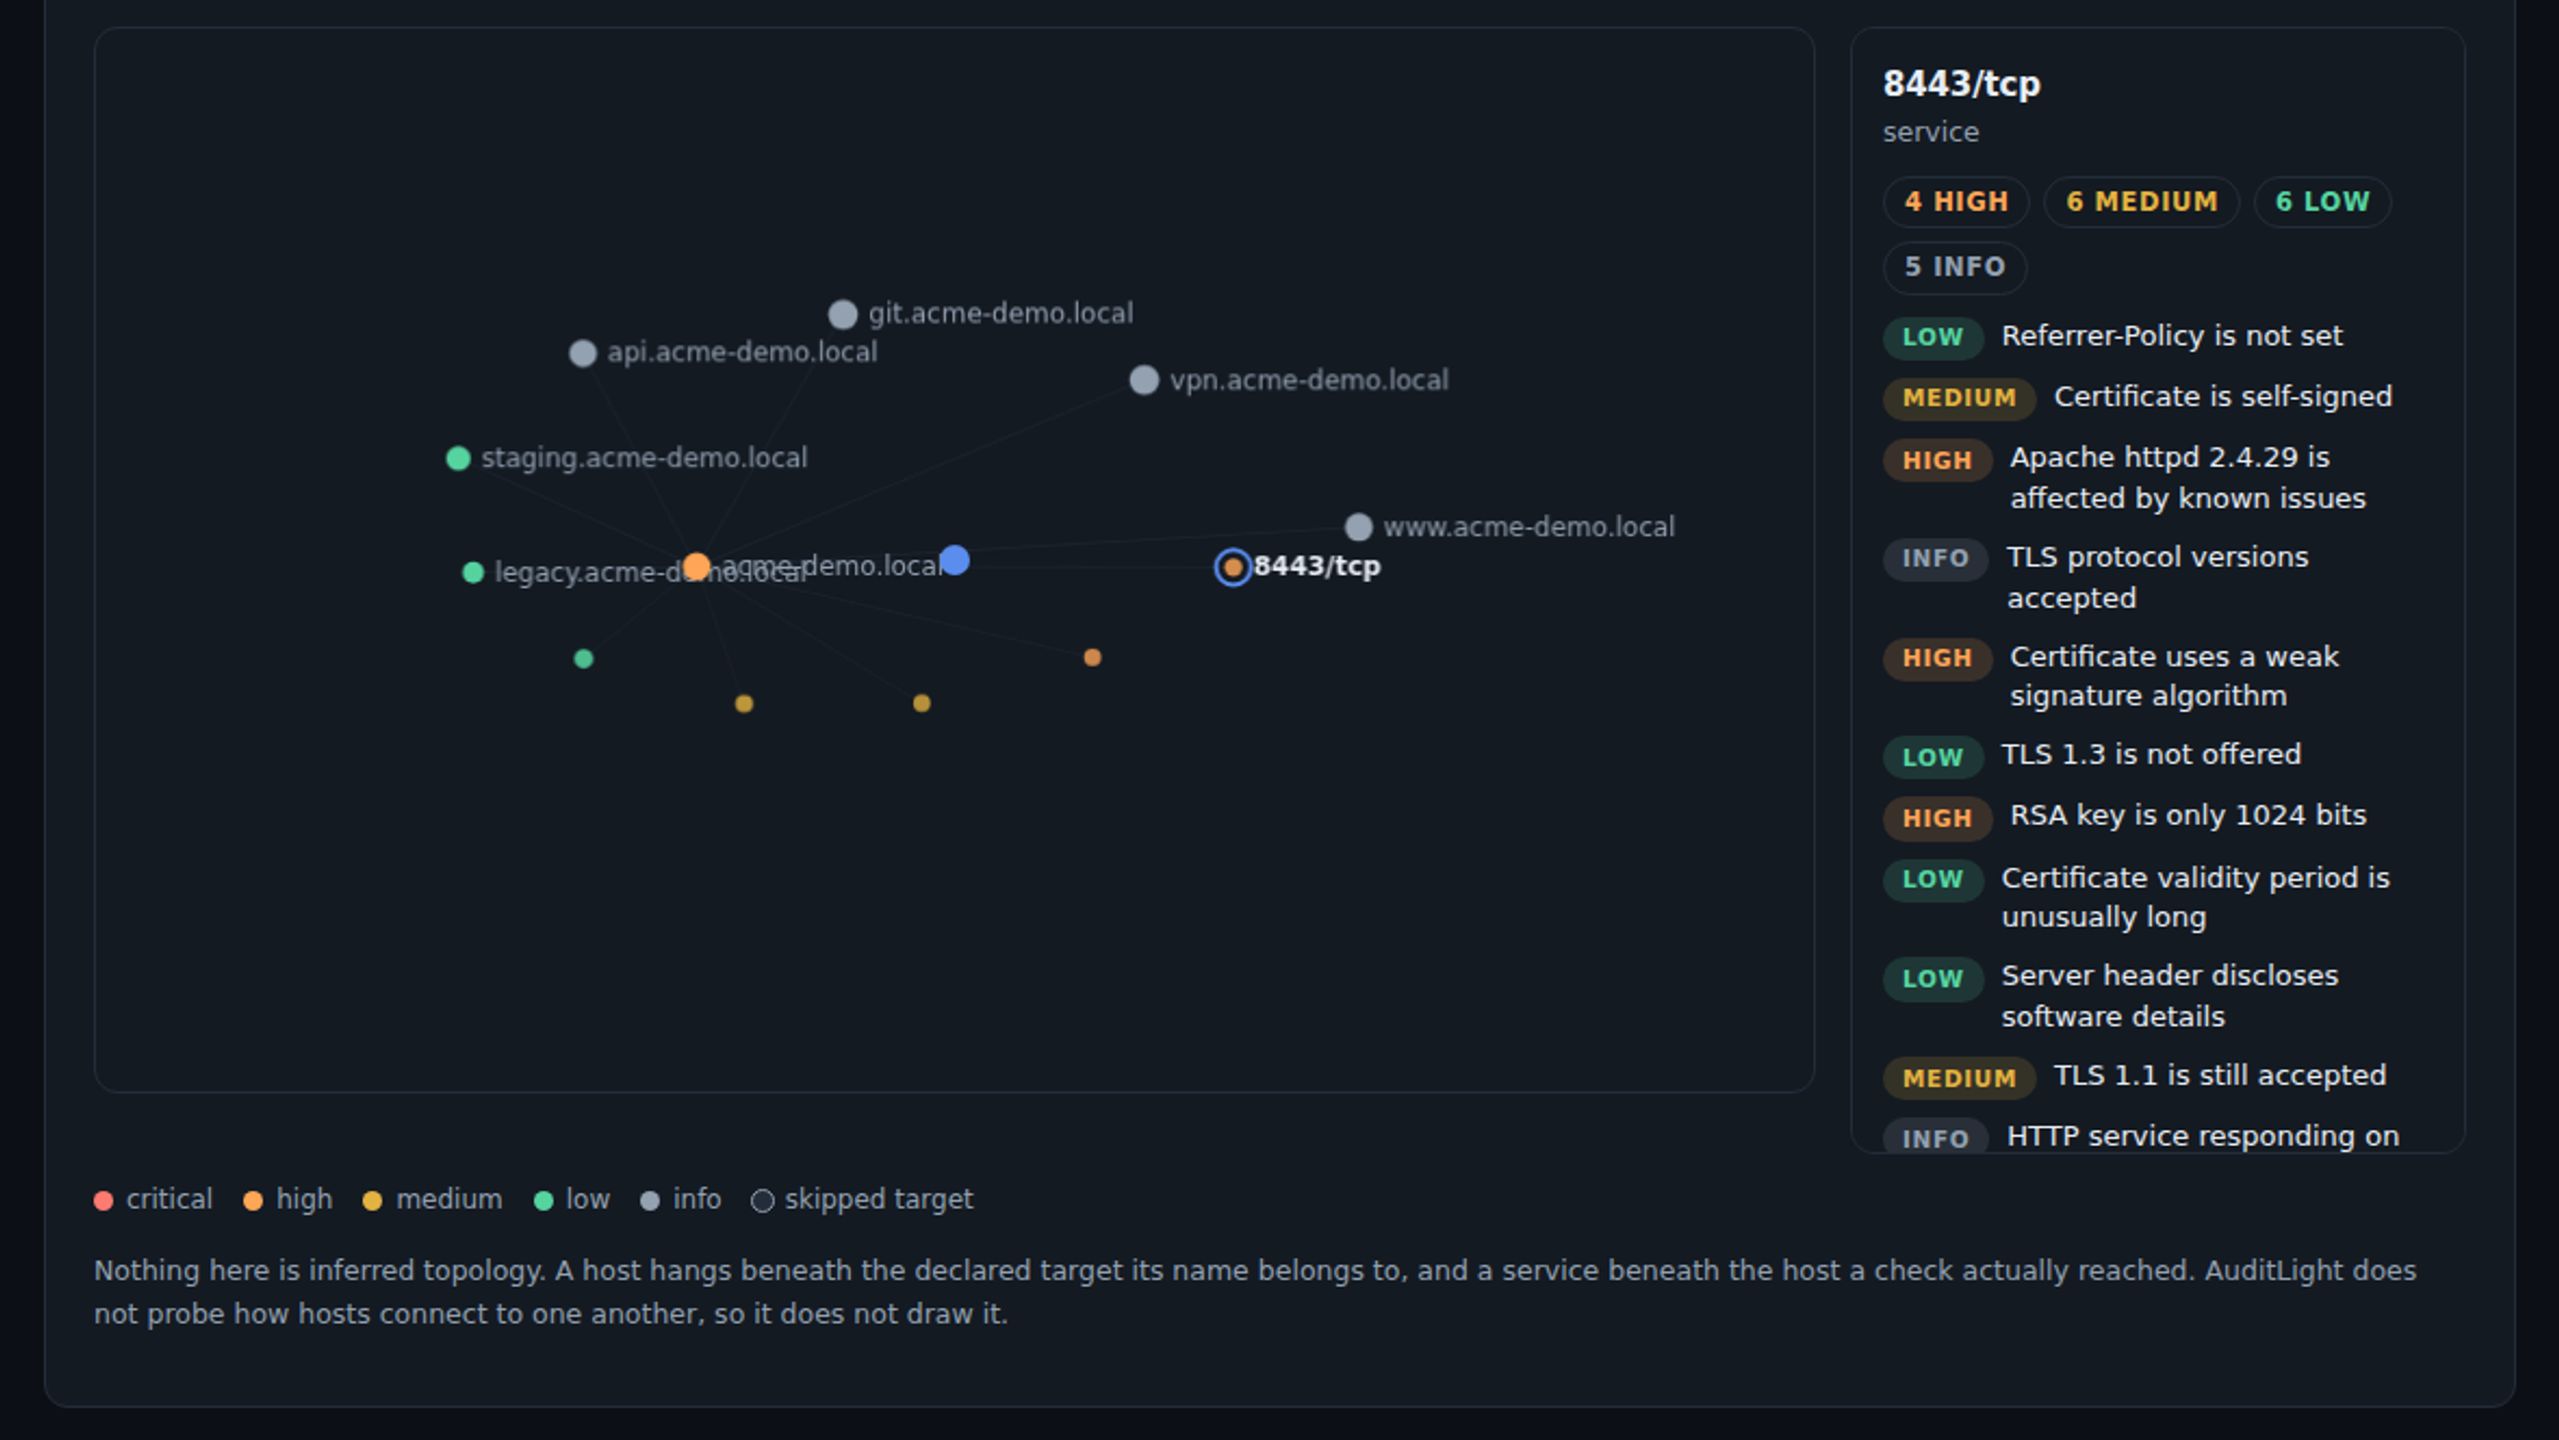
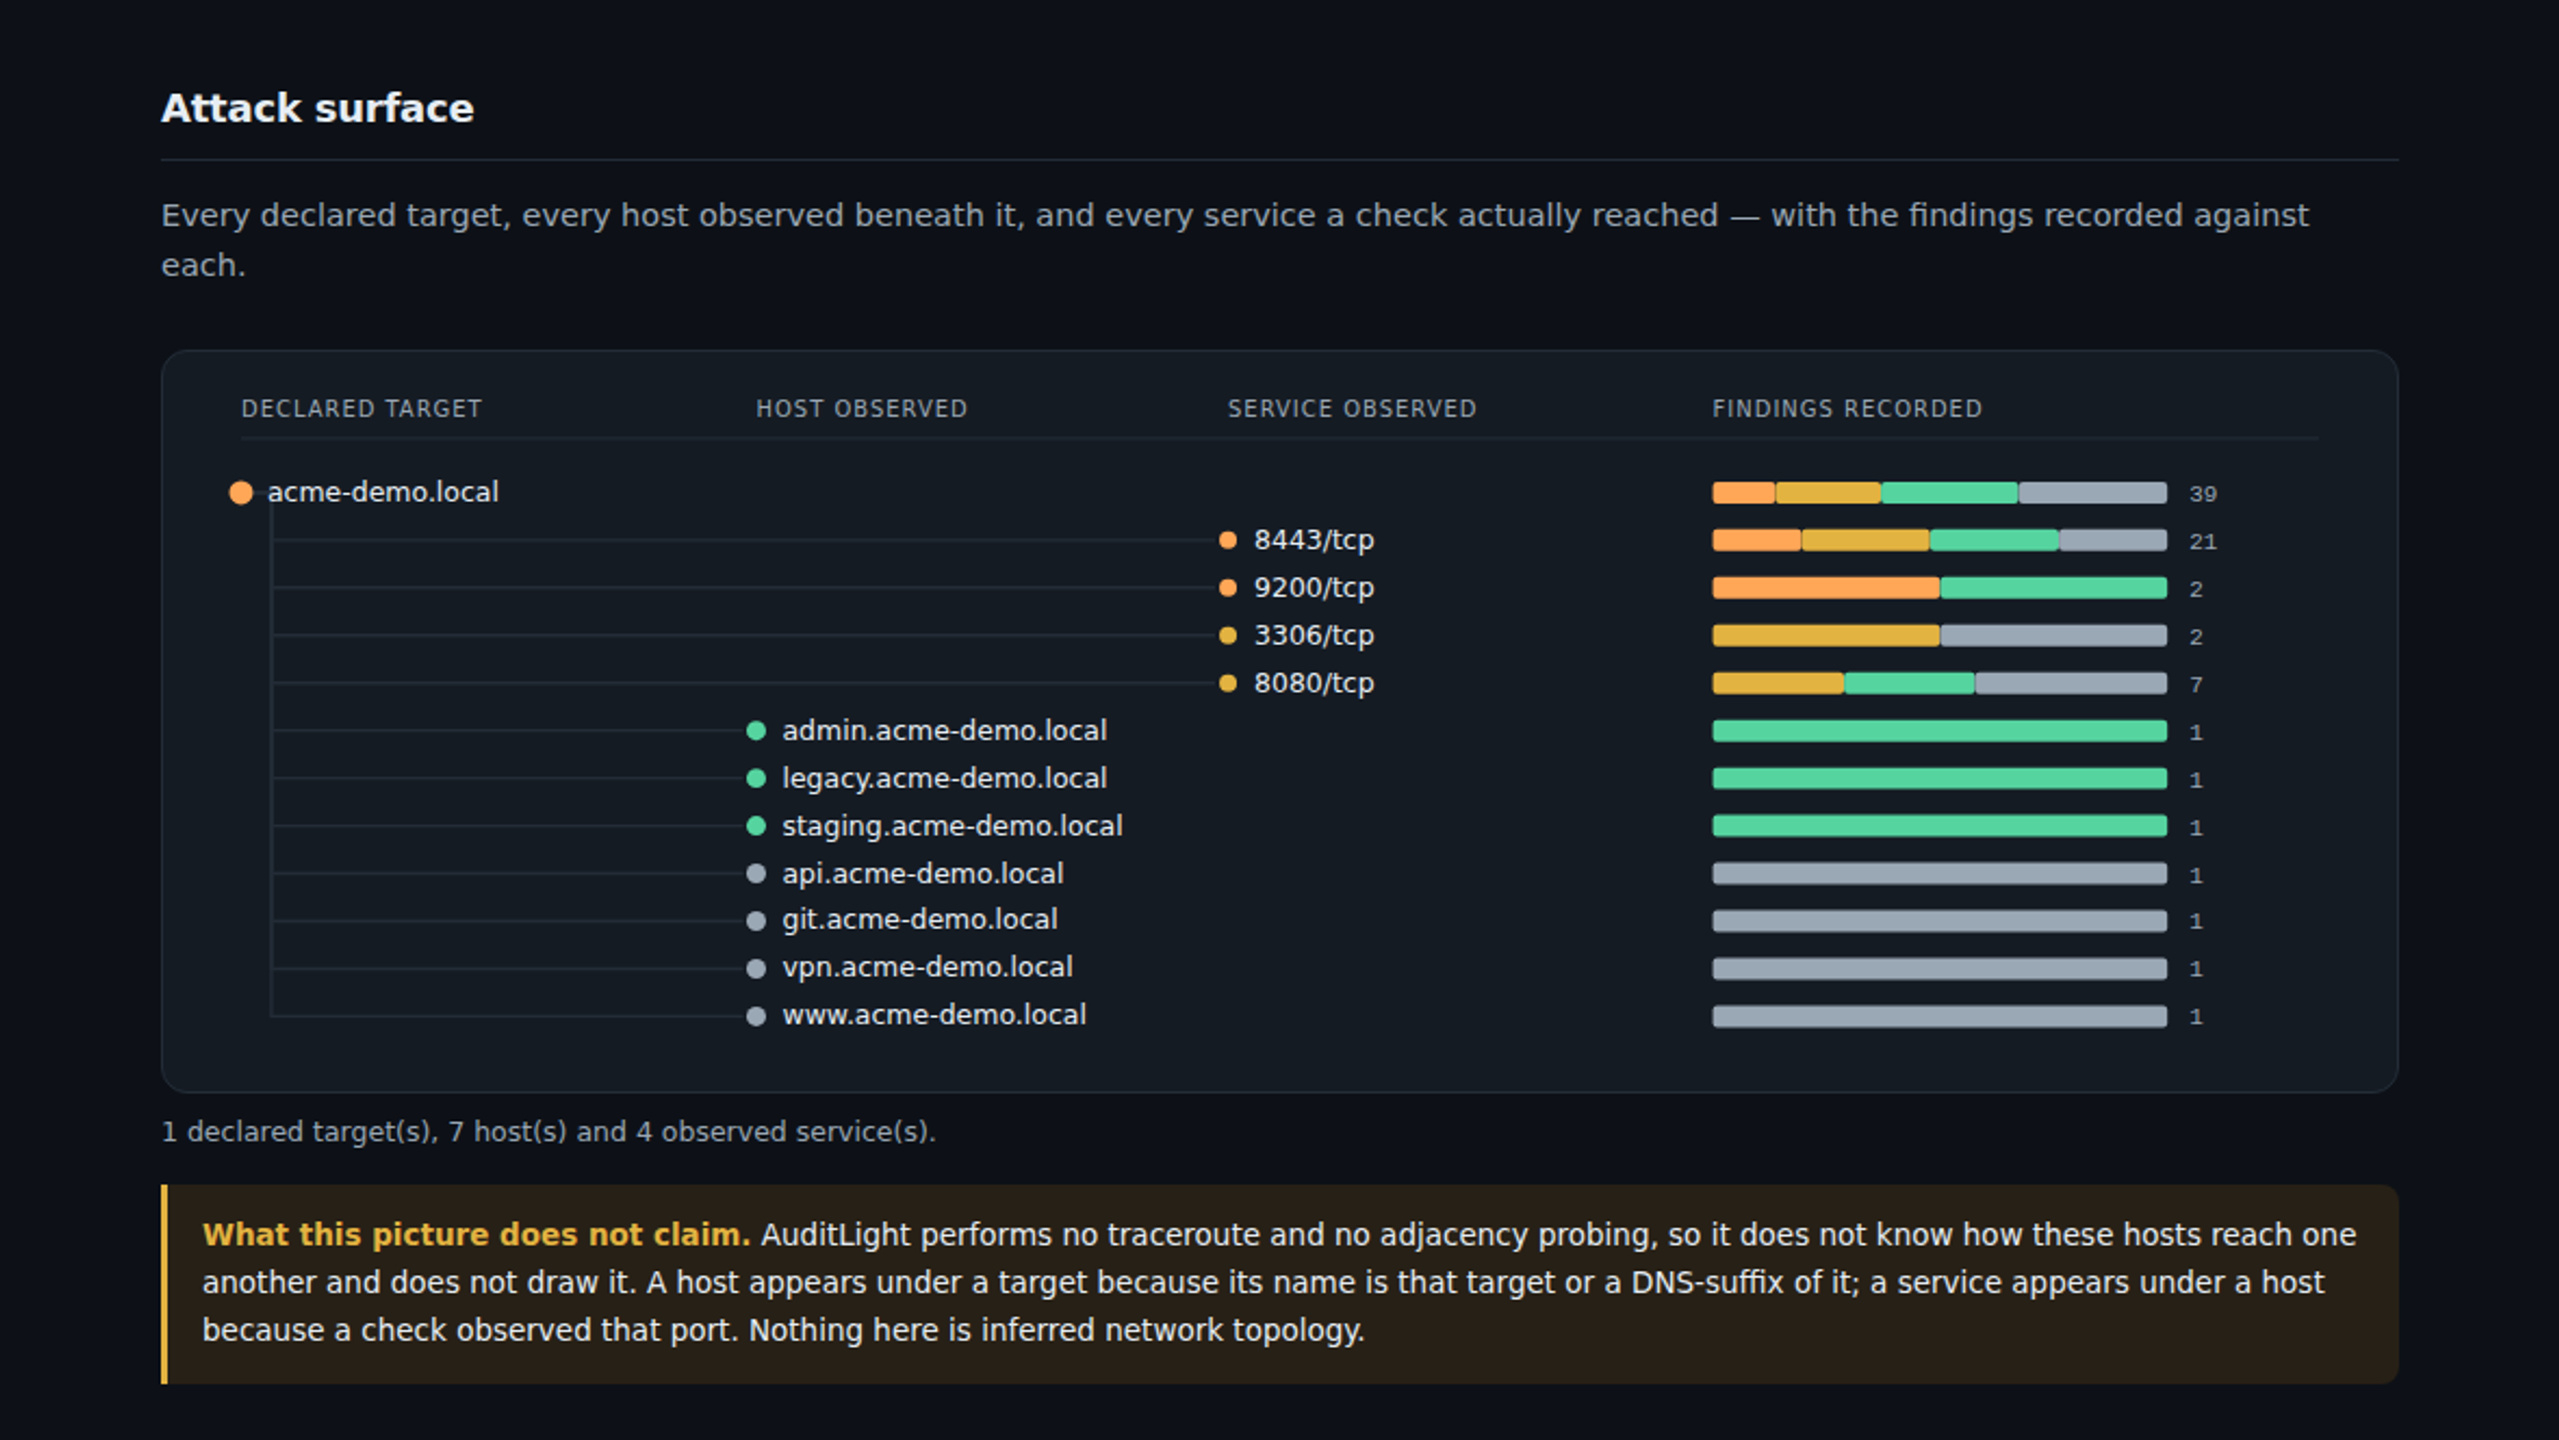
- Surface map: tree in the report, 3D graph in the dashboard
- Control mapping: ISO 27001:2022, CIS v8, NIST CSF 2.0, UU PDP — evidence, not certification
- Authorisation expires after 90 days; scheduled runs then wait for a human
Free limits: 3 targets per job, 50 findings shown (overflow counted), watermarked Assessment Report.
Server requirements
- Linux x86-64; single static binary, stdlib only, works air-gapped
- Measured: ~12 MB binary, ~11 MB RAM idle; jobs stored as files under -data
- Minimum: 1 vCPU, 512 MB RAM, 1 GB disk for report history
- Dashboard 127.0.0.1:8431; outbound only to targets you are authorised to assess
Not a penetration test. Linux only. Pro $79 / Team $249; 14-day trial.
AI Assist (optional, offline): Explain any finding on your own hardware; the engine still decides.
Whop sells paid licences only. Free: github.com/nizartuanku/auditlight