
Loglight
$29/ month
14 day trialSelf-hosted threat detection from logs & network flows — with a 3D network map
You have logs. Nobody reads them — so a brute force or a beacon is found a week too late. Loglight is the self-hosted SIEM-lite for that gap, and it sees your network flows too.
Features
- Inputs: syslog (RFC3164/5424), files, journald, Docker, Windows events, NetFlow v5/v9/IPFIX
- Seven detections: brute force, distributed auth-failure spikes, port and host scans, abnormal egress, new privileged accounts, beaconing, new listening service
- Correlation: scan → brute force → successful login from one source = one CRITICAL incident with timeline
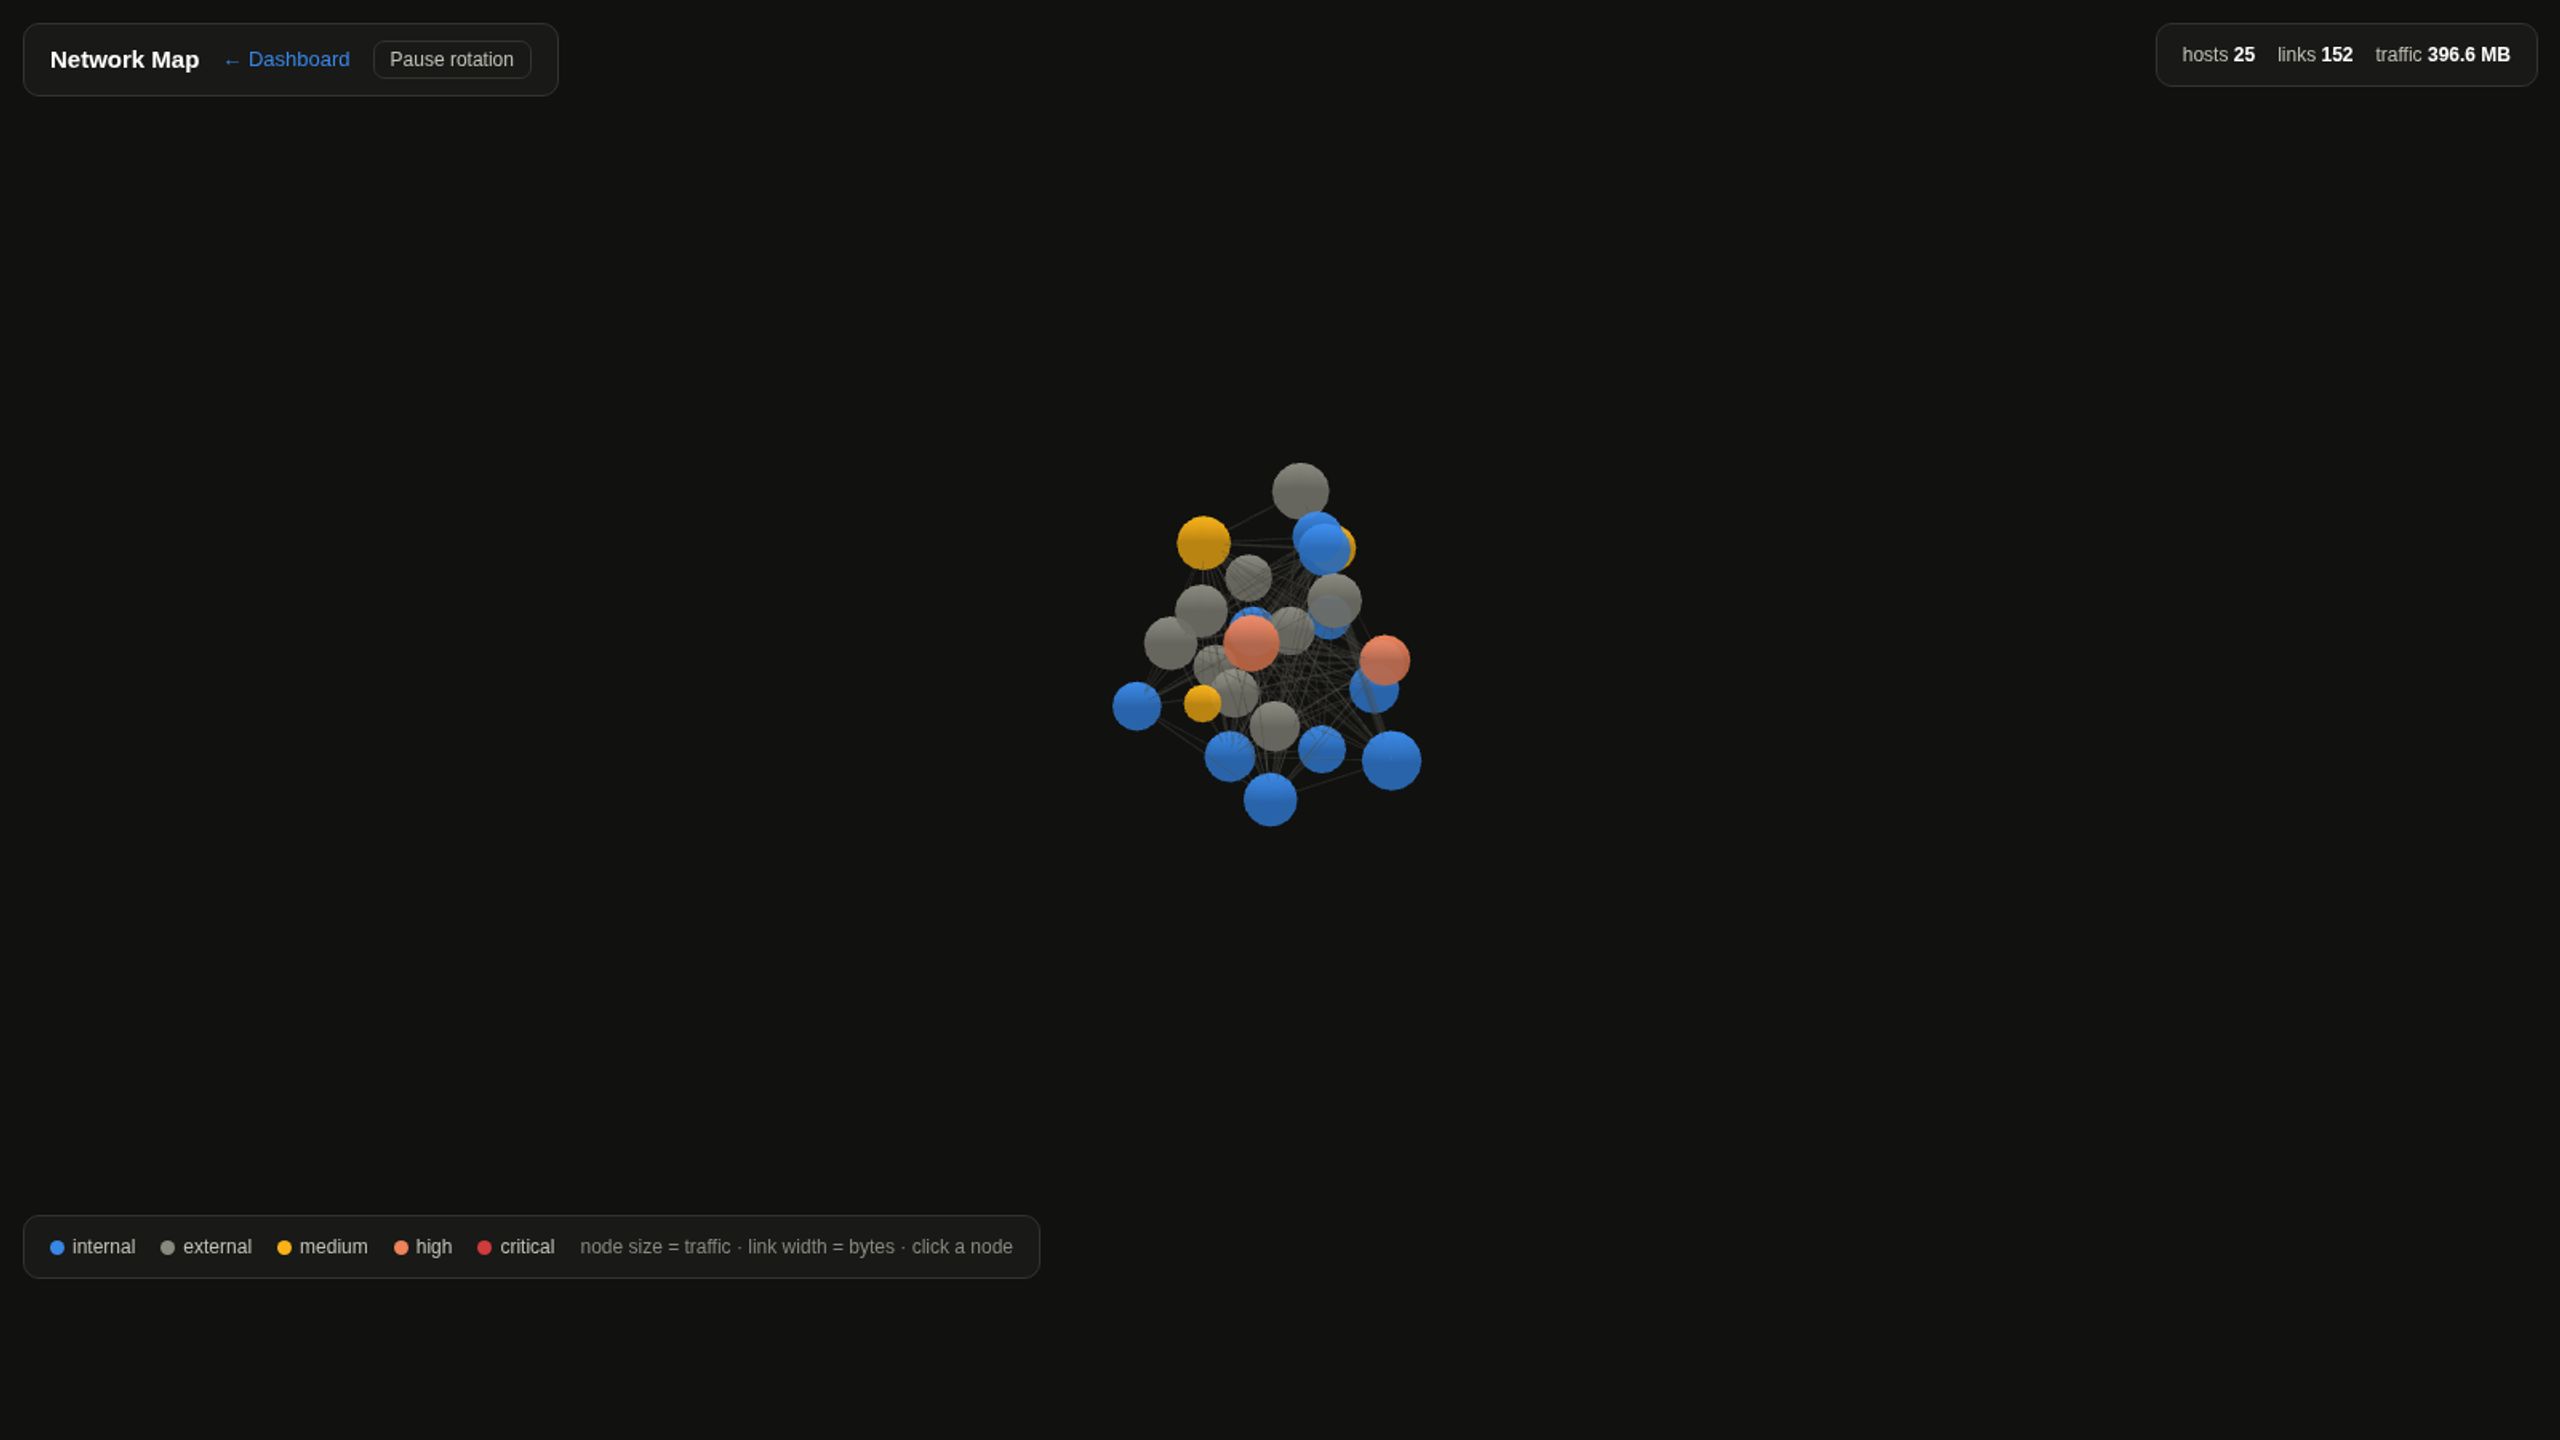
- 3D network map (offline): who talks to whom, sized by traffic, hosts glow by severity
- Receives other Hexward tools’ findings, and Wazuh alerts (a Wazuh brute force + Decoy trip = one incident)
Server
- Linux x86-64; static binary or Docker
- ~12 MB binary, ~10 MB RAM idle, SQLite (no DB server)
- Sizing: 1 vCPU/1 GB/5 GB for a few hosts; 2 vCPU/2-4 GB/20+ GB at 10 sources with flows
- Dashboard 127.0.0.1:8427; inbound syslog 5514 and the flow ports you configure
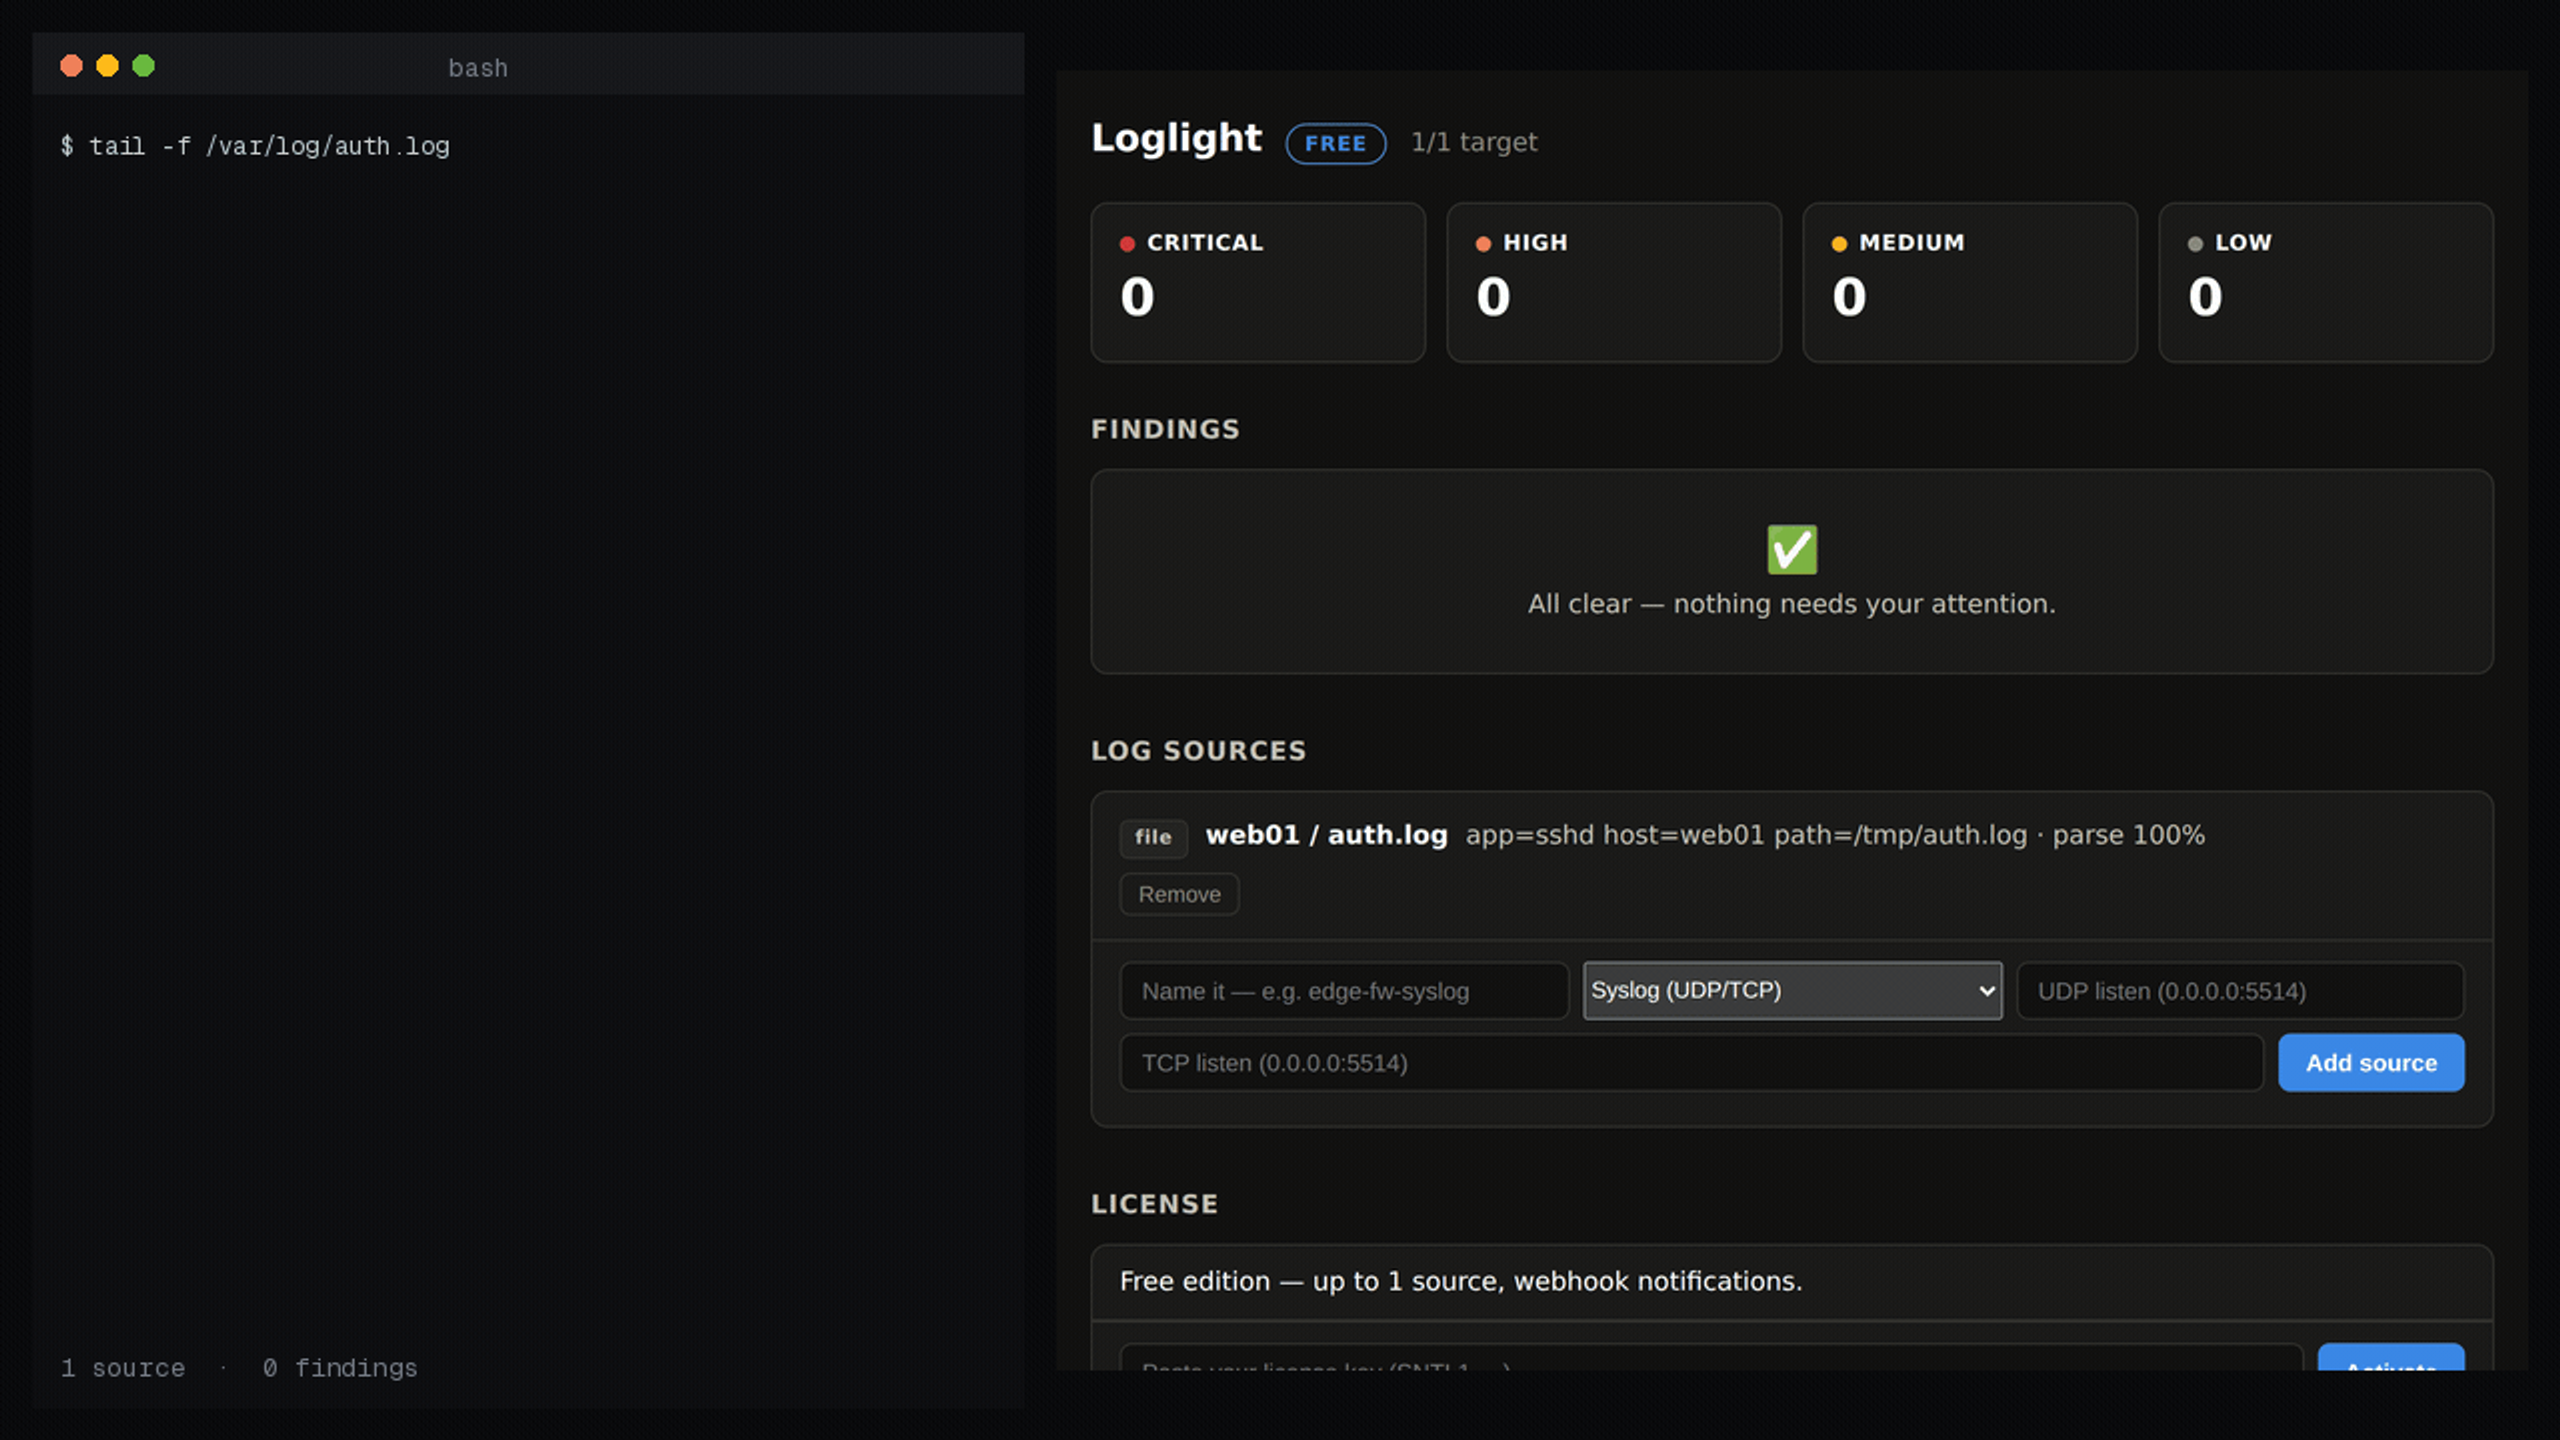
Tiers. Free: 1 source (GitHub, full chain needs 2+). Pro: 10 sources, email/Slack/Telegram. Team: unlimited, multi-user, PagerDuty/MS Teams. 14-day trial.
Exports to Wazuh & Splunk too (every tier): file, syslog JSON/CEF, Splunk HEC.
AI Assist (optional, offline): explains any finding on your hardware; the engine decides.
Delivery: key by Whop DM; files in Downloads.
Whop sells paid licences only. Free: github.com/nizartuanku/loglight