

RuleHawk
$29/ month
14 day trialSelf-hosted firewall auditor — find shadowed, permissive & drifting rules
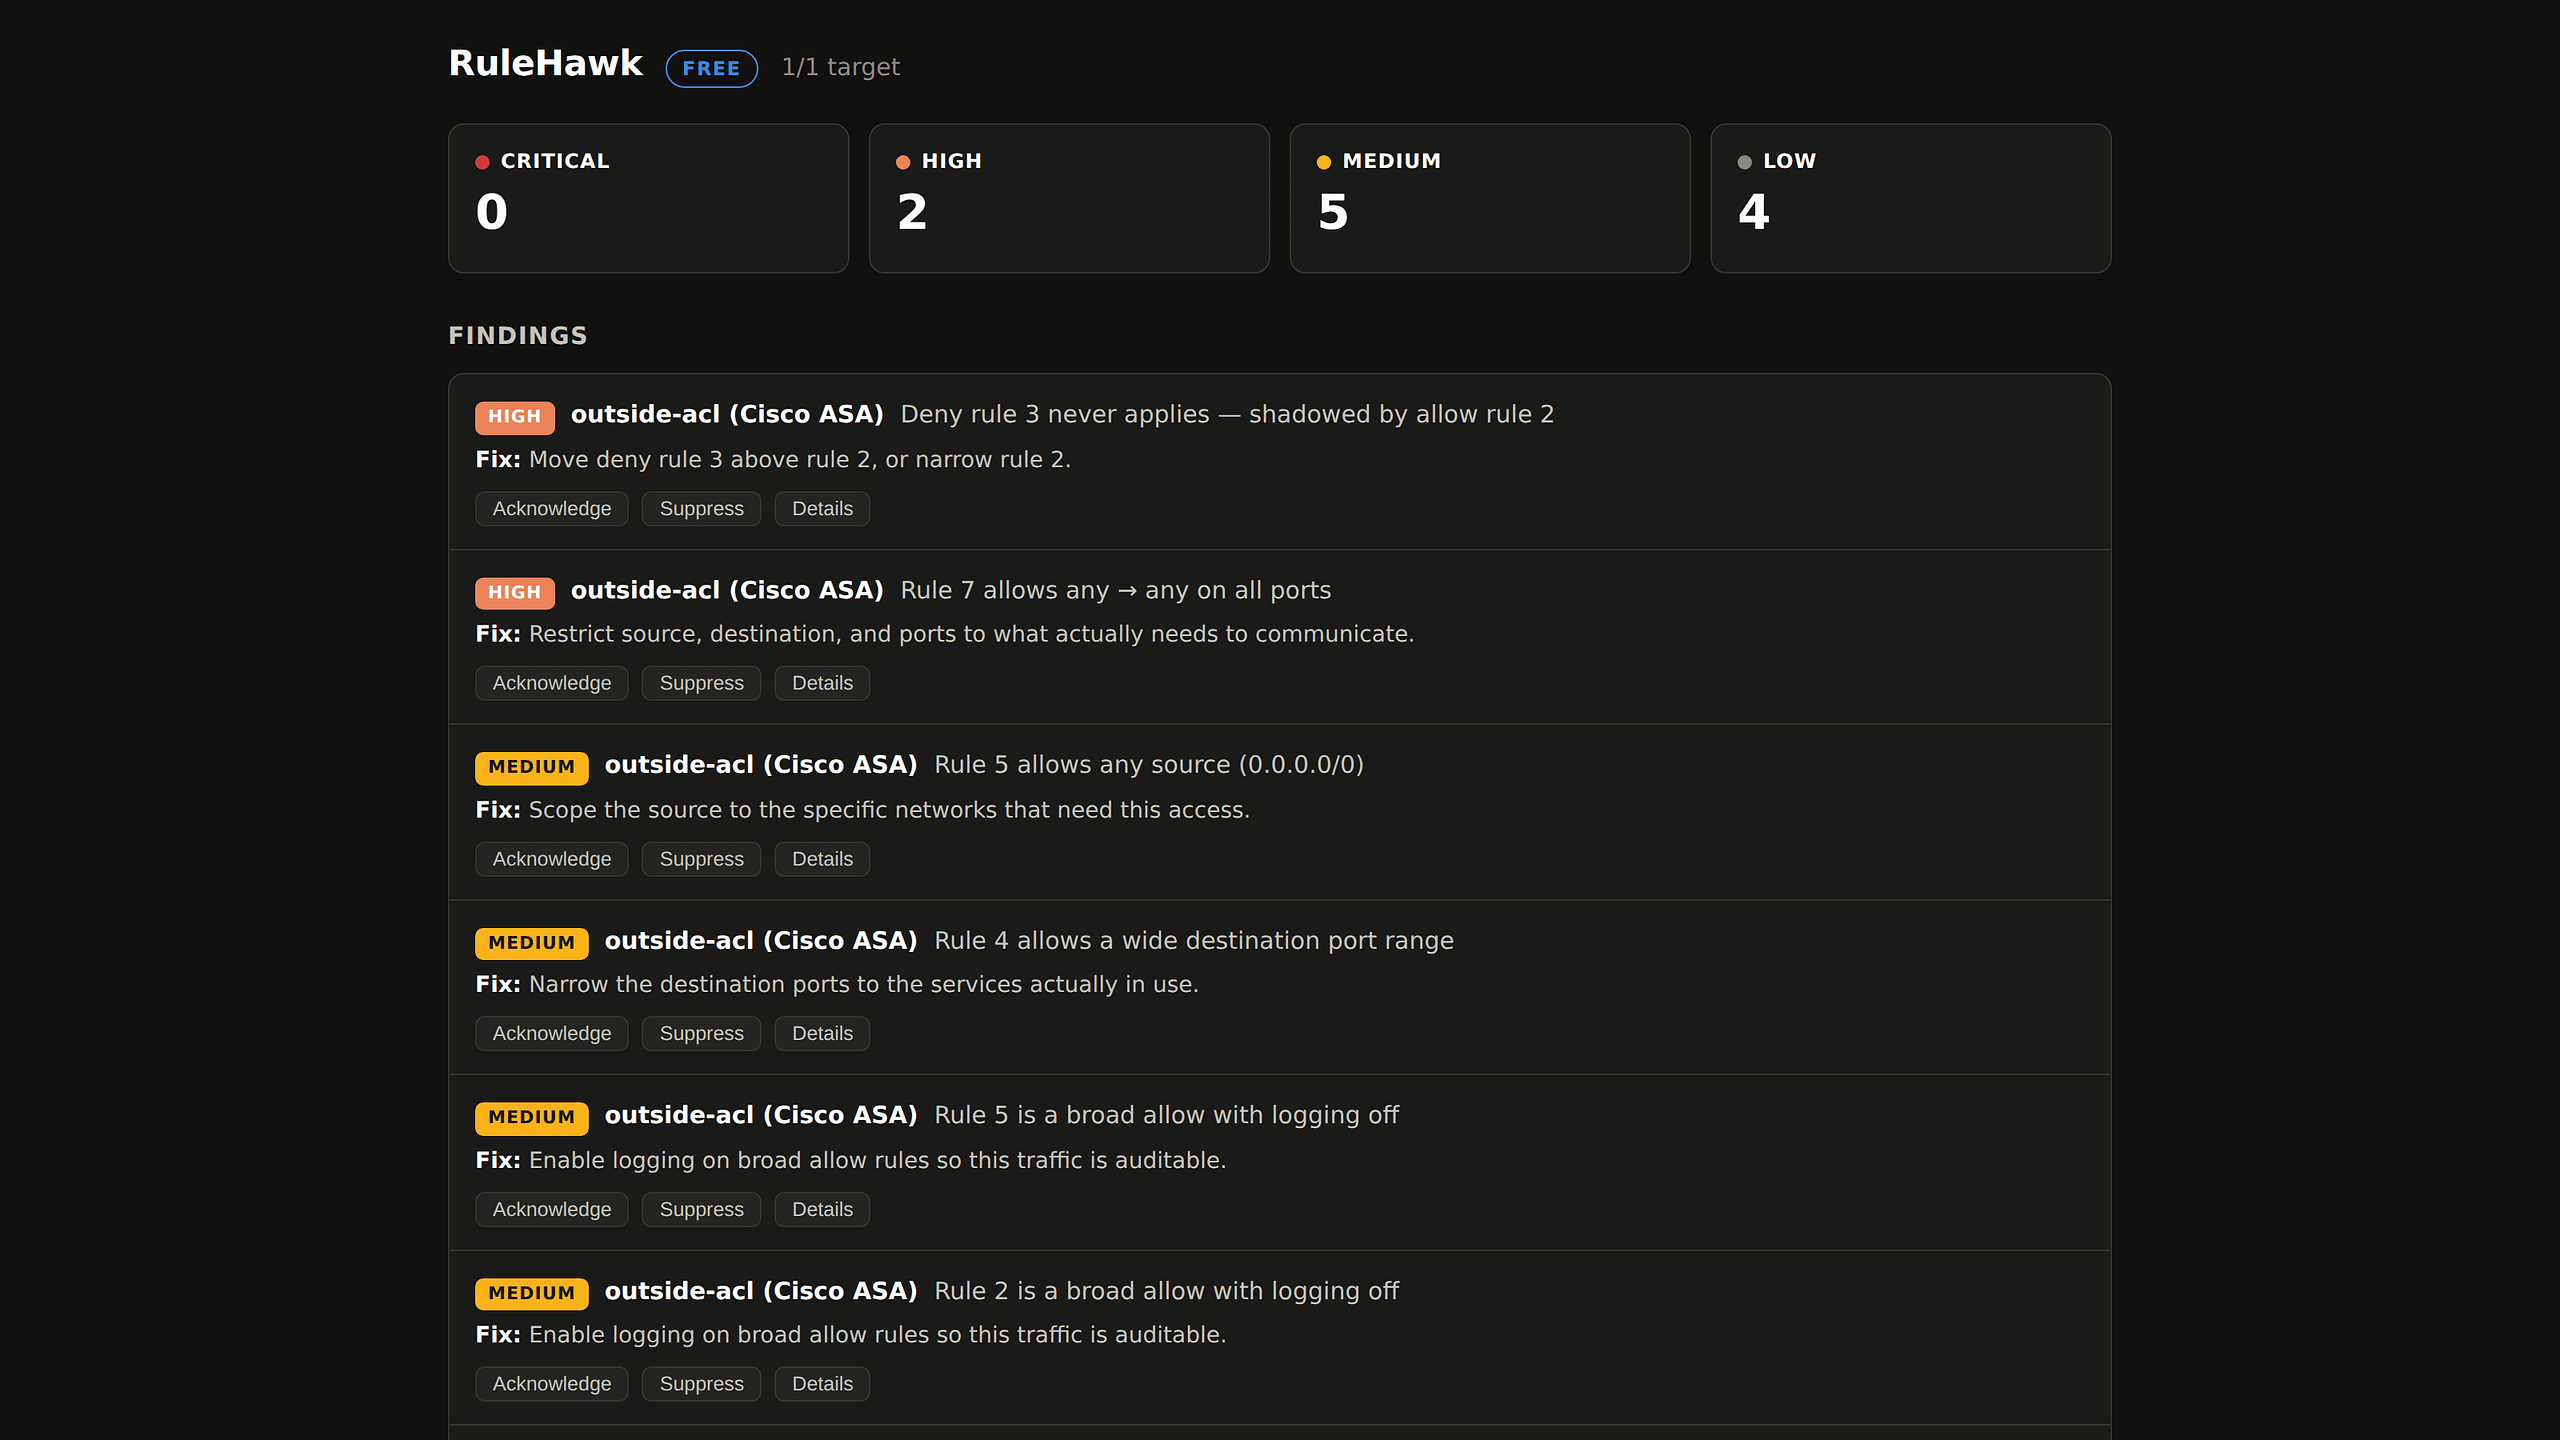
The rule that was meant to protect you, and doesn’t. A deny added after an incident sits below an old permit covering the same range — it never fires.
Features
- Four checks on an exported config: shadowed/duplicate rules, permissive rules, hygiene, drift from a baseline
- Accurate iptables: -i/-o, negation and per-chain scope honoured; rule numbers match --line-numbers
- Every finding names the rule and the fix, worst first; unparsed lines become a finding, never a silent drop
- Vendors: iptables/nftables, Cisco ASA, pfSense/OPNsense, FortiGate (FTD/Palo Alto on the roadmap)
- Audits rules as written, not packet flow; fully offline
Server requirements
- Linux, macOS or Windows (amd64/arm64); single static binary. Docker image hexward/rulehawk is the free edition; Pro/Team use the licensed binary
- Measured: ~10 MB binary, ~10 MB RAM idle, SQLite — no database server
- Minimum host: 1 vCPU, 512 MB RAM, 200 MB disk
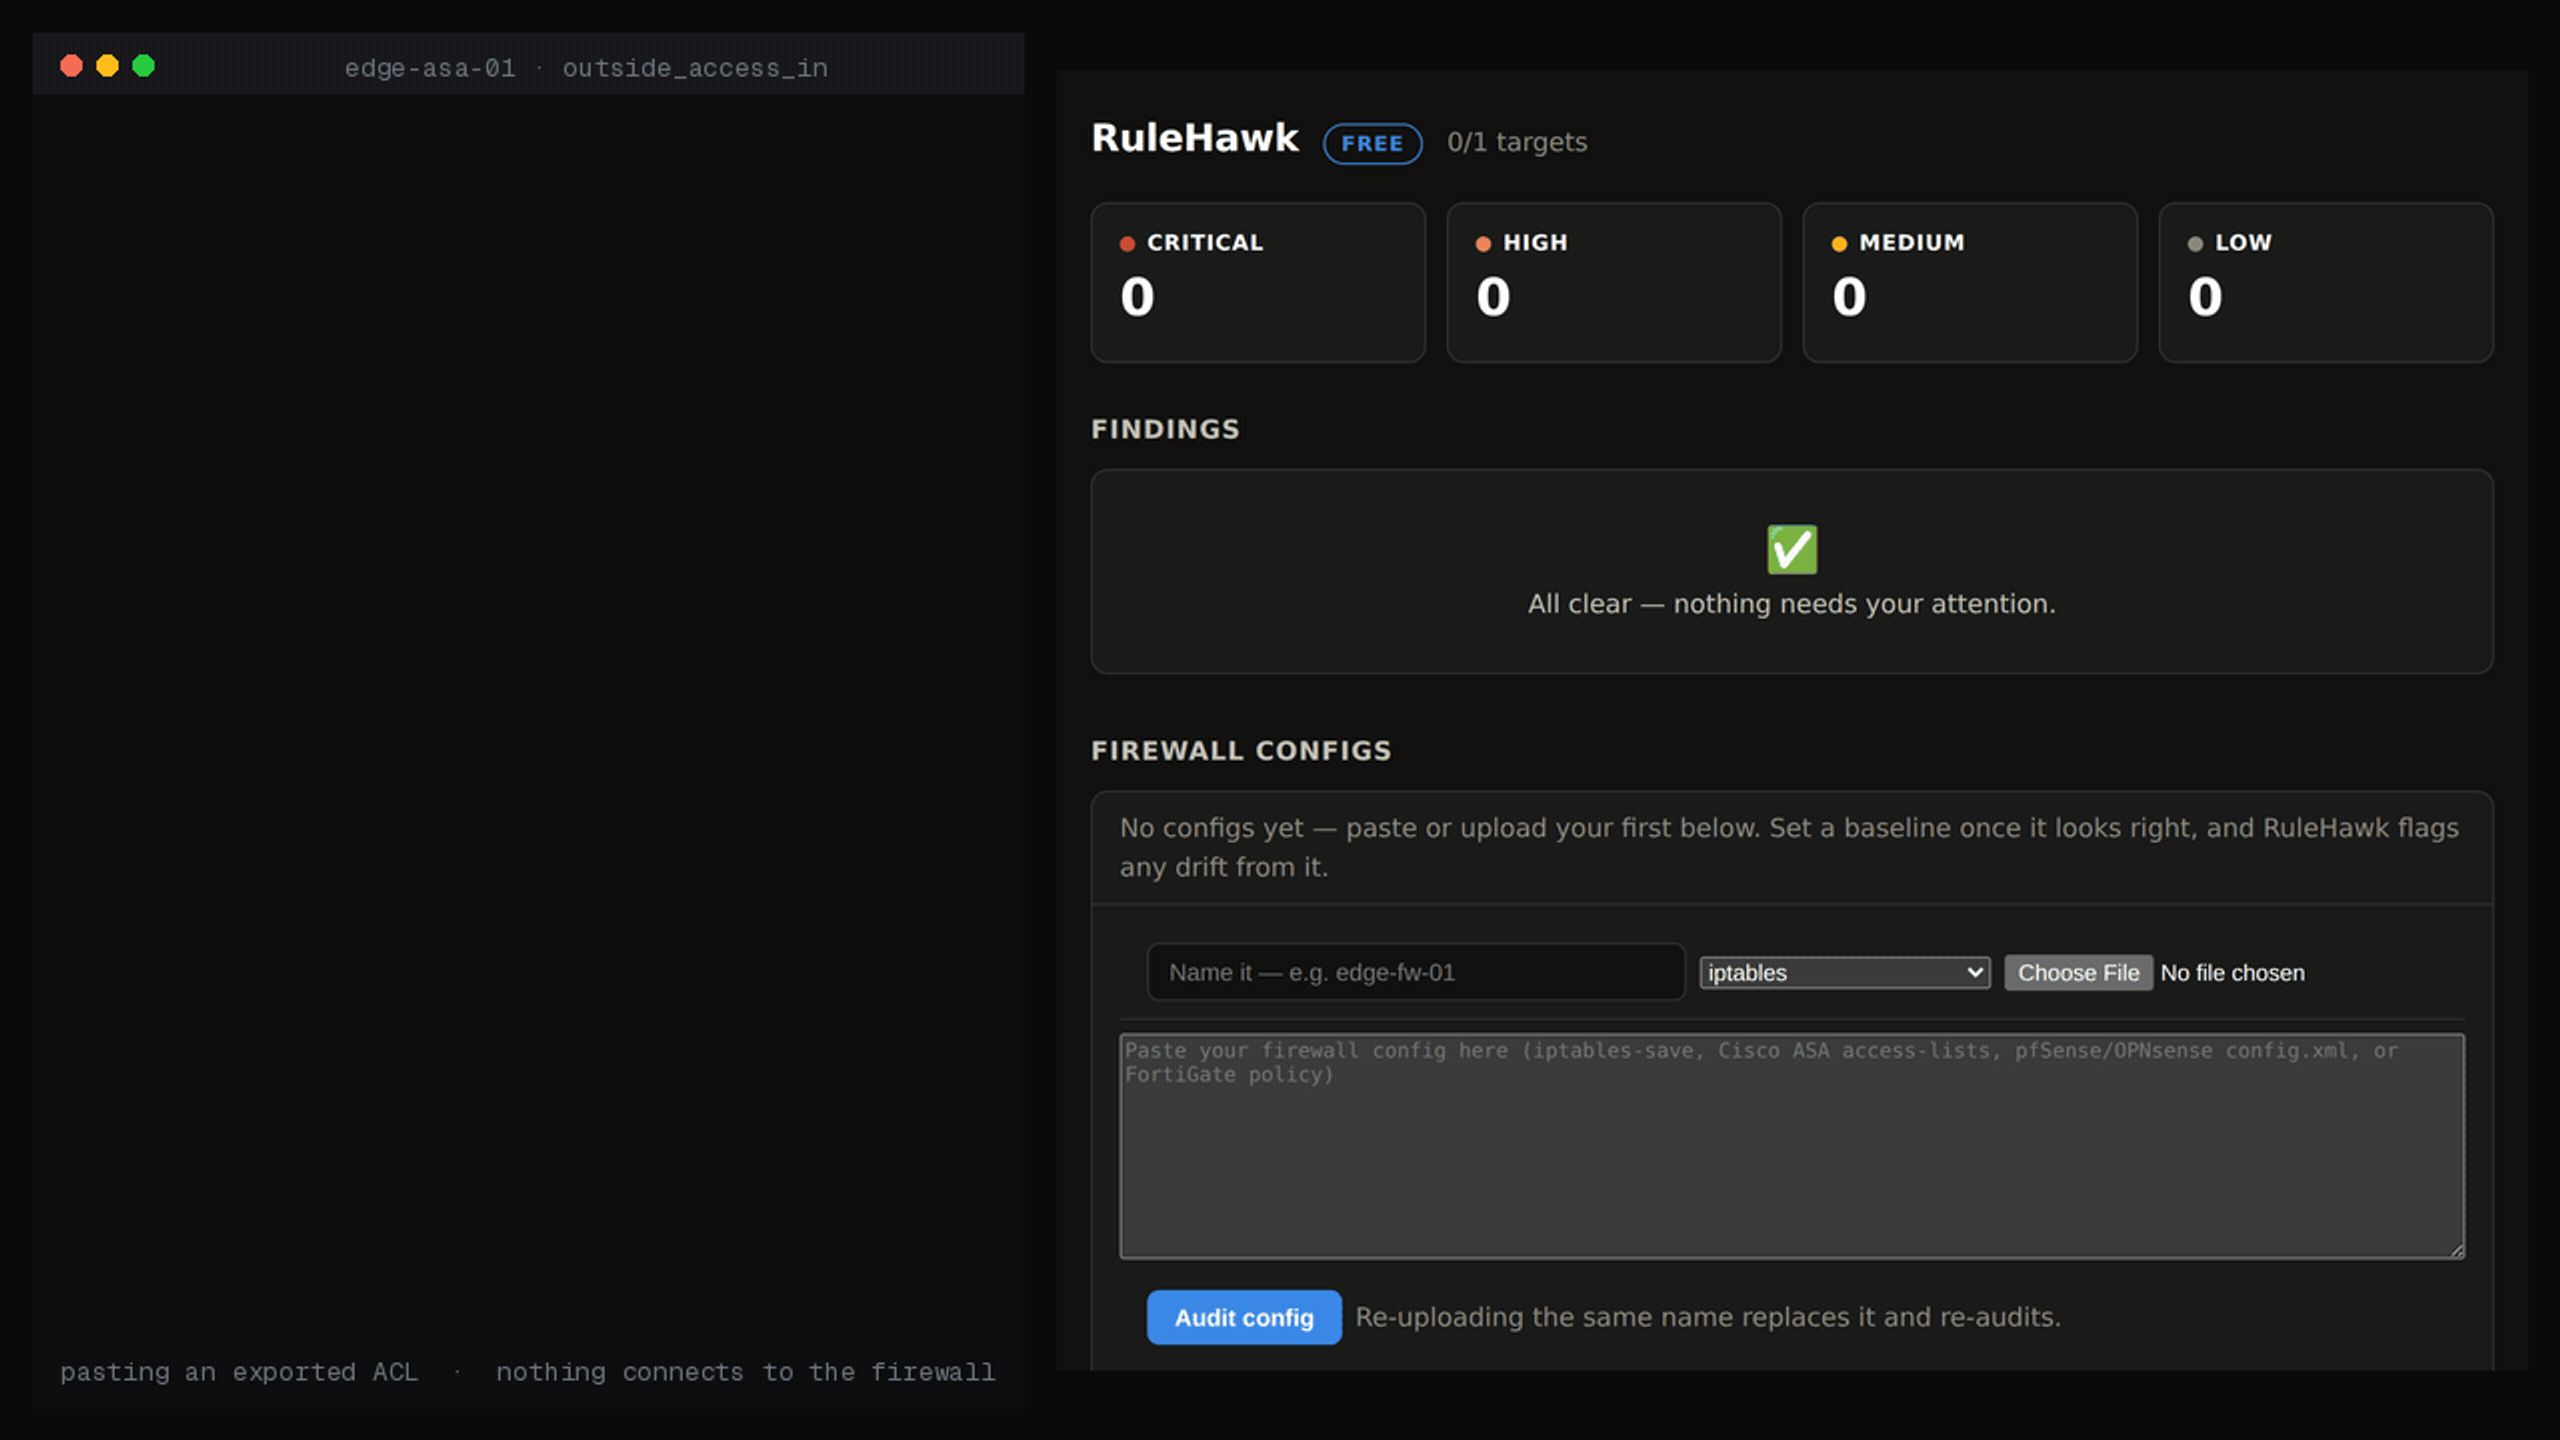
- Dashboard 127.0.0.1:8426; no network access needed
Tiers. Free: 1 config, all checks, webhook+syslog, 30-day history (GitHub). Pro: 25 configs, scan-now, email/Slack/Telegram, 1-year history. Team: unlimited, multi-user, PagerDuty/Teams. 14-day trial.
AI Assist (optional, offline): Explain any finding on your own hardware; the engine still decides.
Delivery. Key by Whop DM; download in the Downloads tab.
Whop sells paid licences only. Free: github.com/nizartuanku/rulehawk