
License Change Skill for Claude
Which of your dependencies changed licence, and on which date
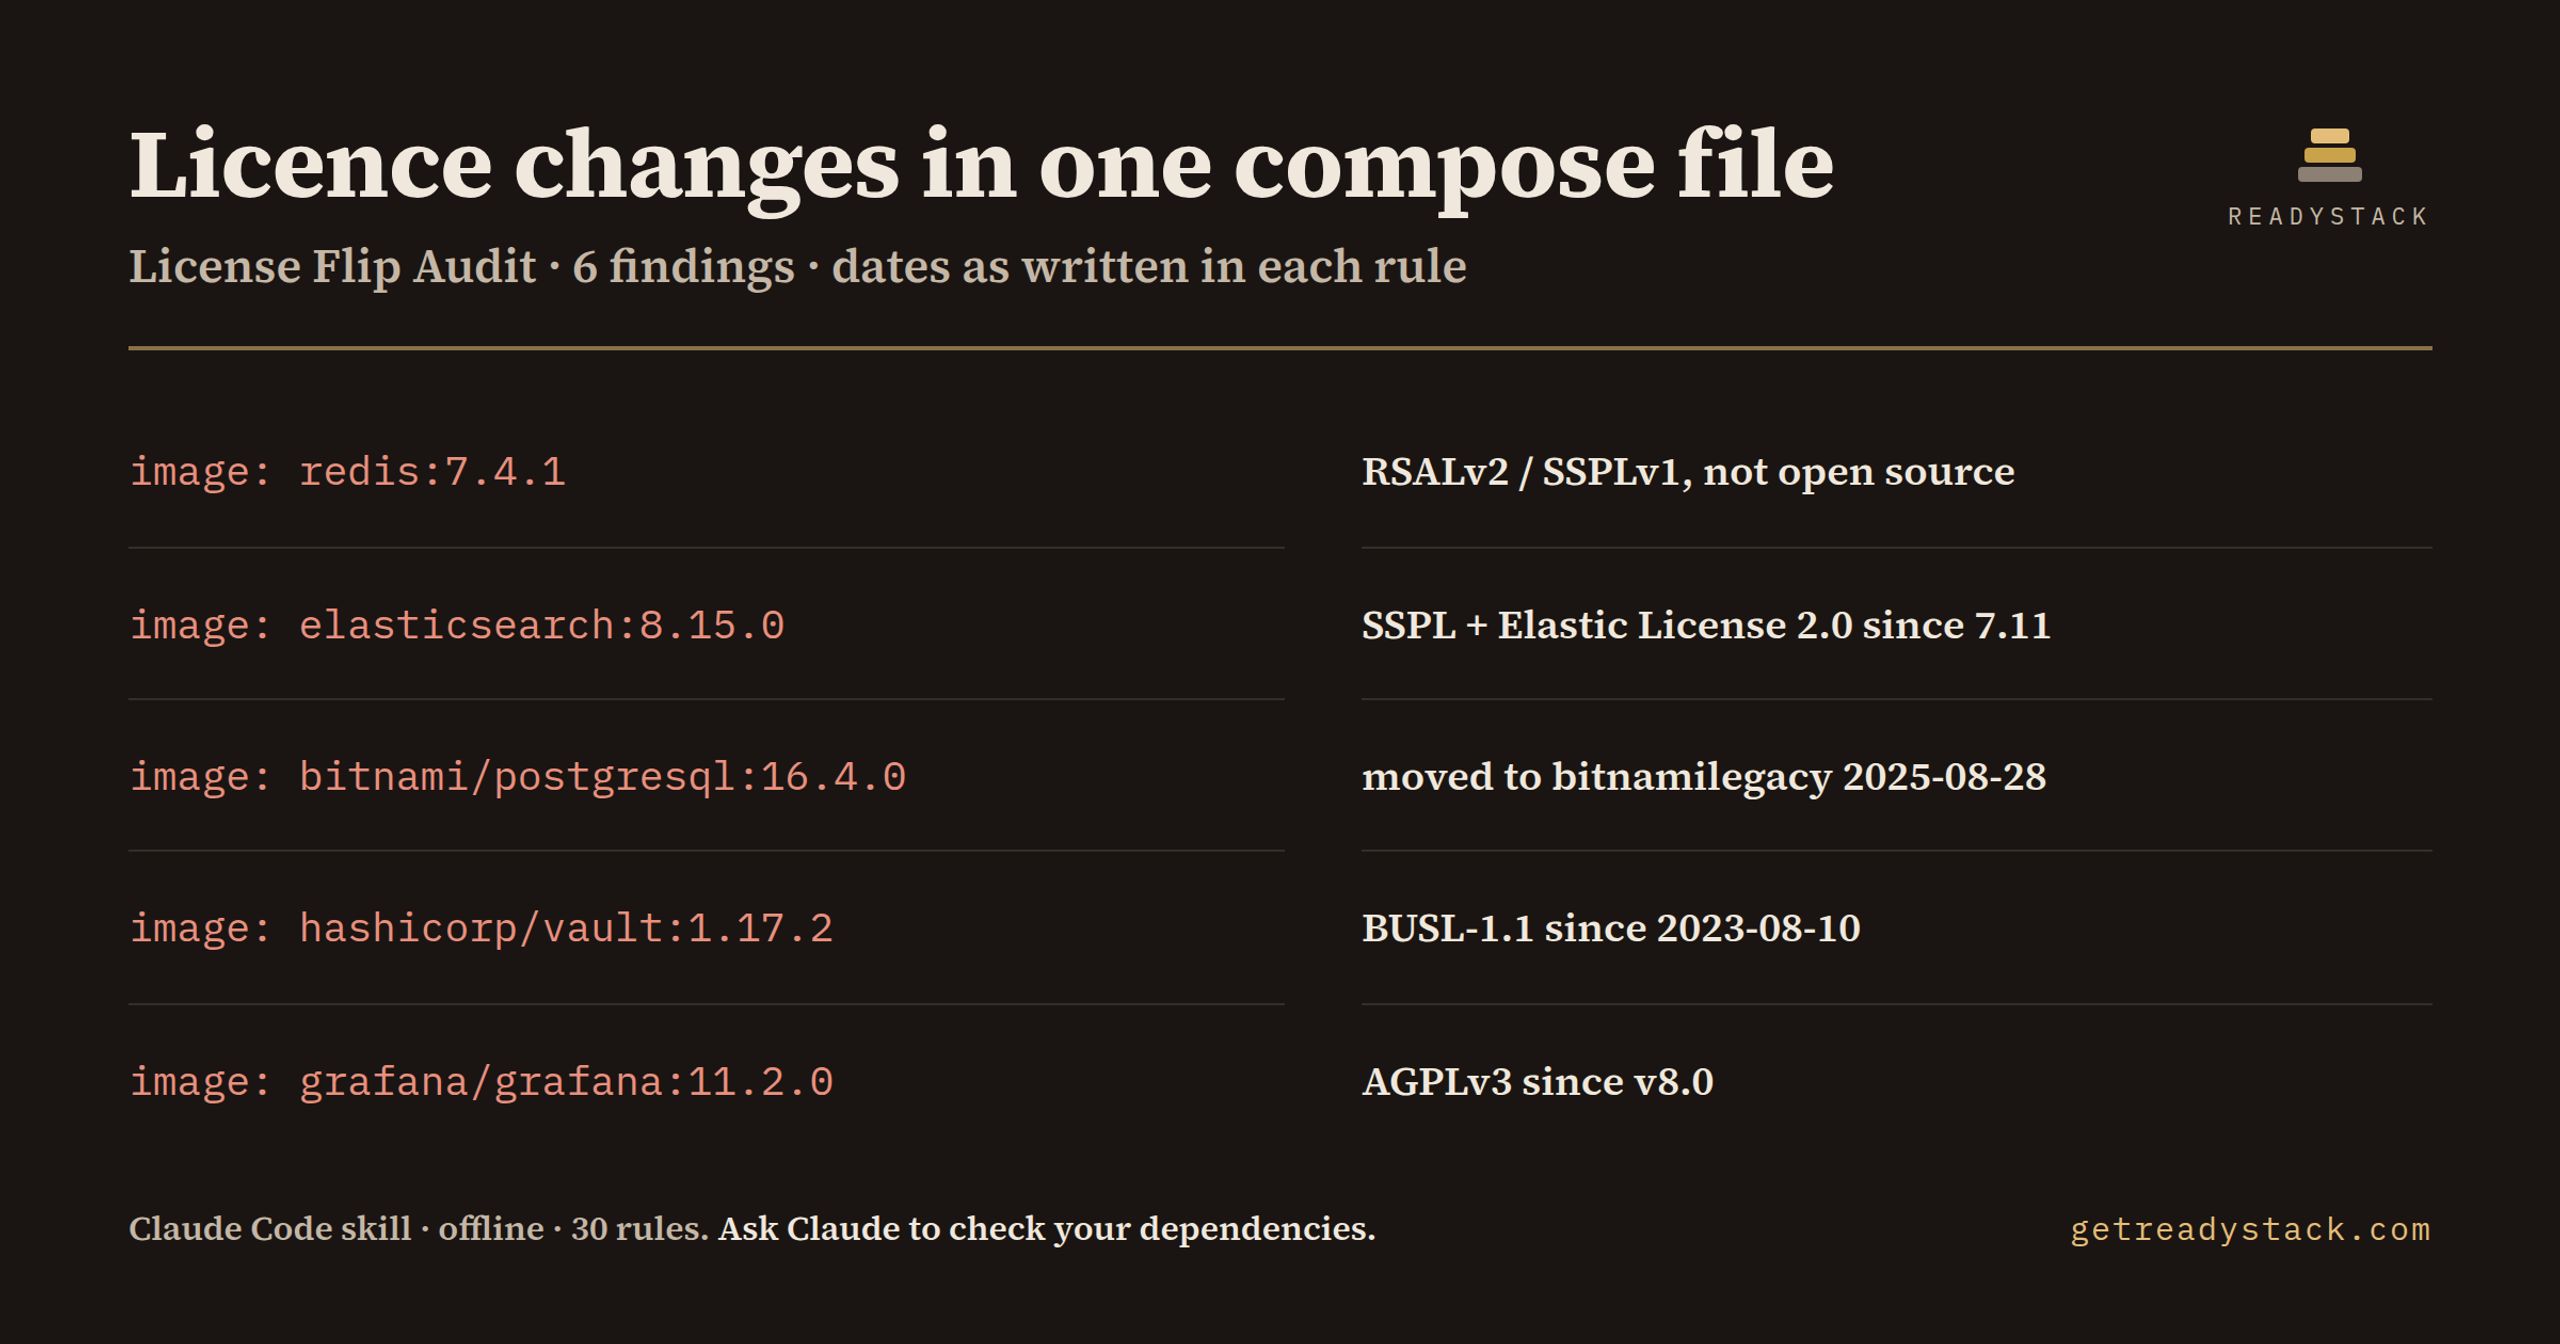
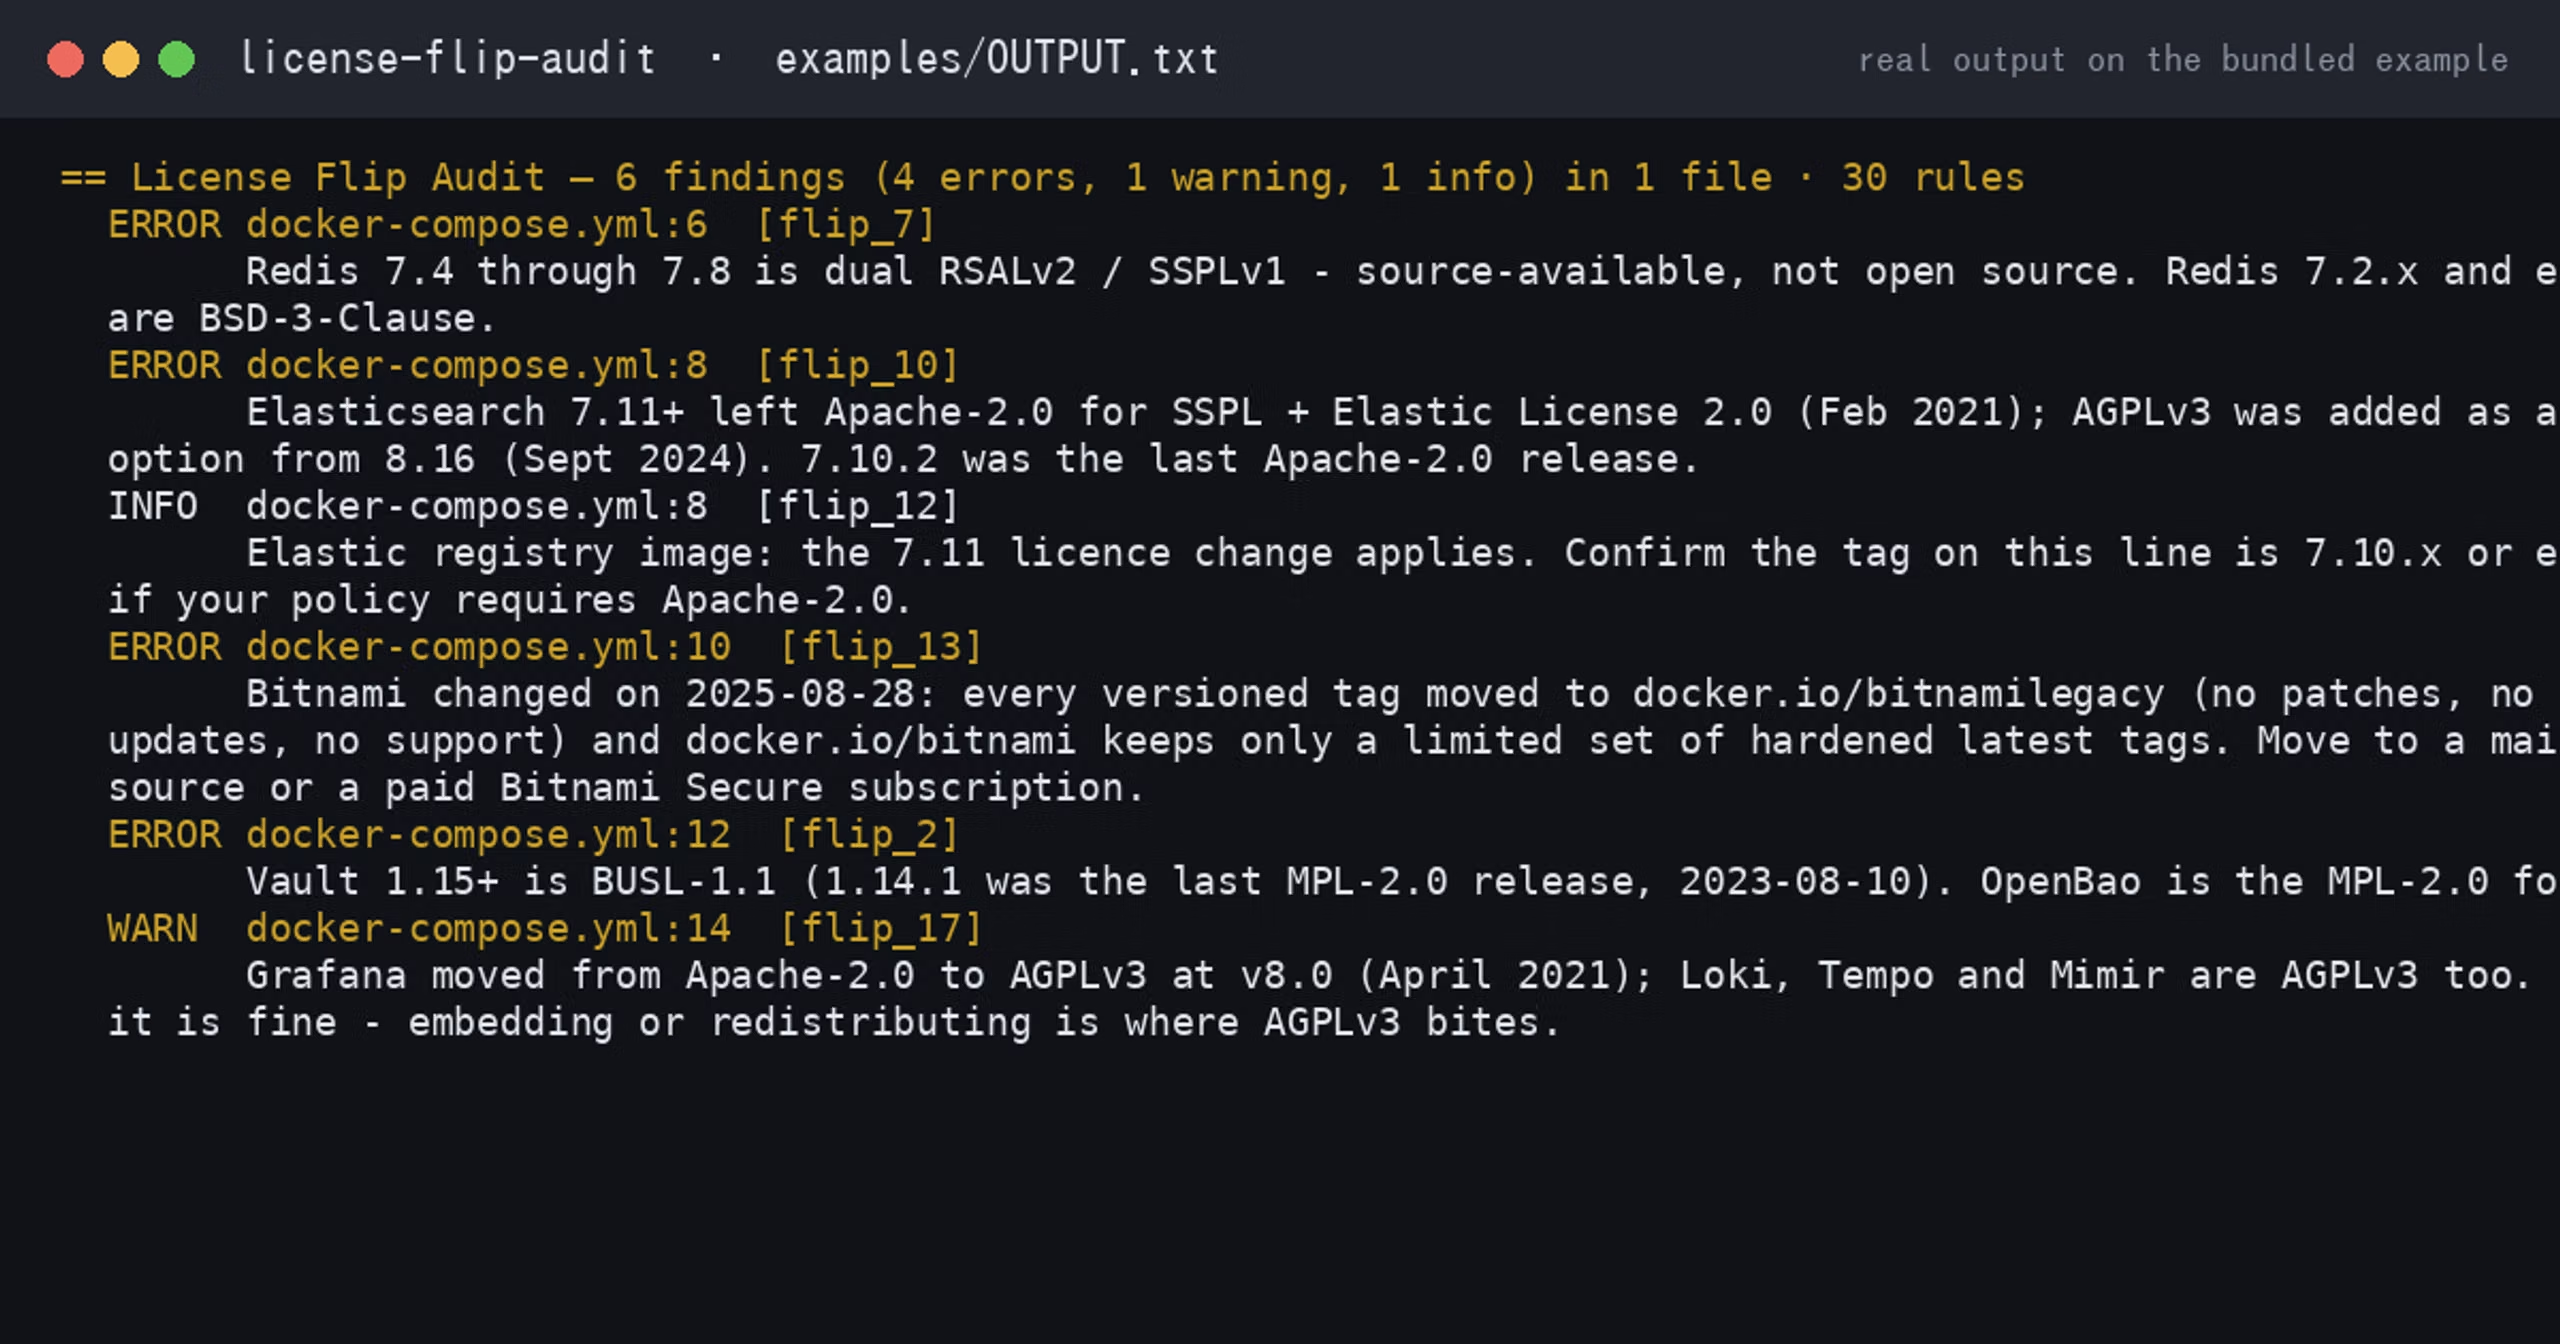
On one docker-compose file it found Redis 7.4 (RSALv2 / SSPLv1), Elasticsearch 8.15 (SSPL + Elastic License 2.0), Bitnami PostgreSQL (moved to bitnamilegacy on 2025-08-28), Vault 1.17 (BUSL-1.1) and Grafana 11 (AGPLv3) — with the date each licence changed.
Who it’s for
For founders and engineering leads who ship a closed-source or hosted product, before an audit, a sale or due diligence.
What breaks, and when
Redis moved to RSALv2/SSPLv1 with 7.4 in 2024 and Bitnami images moved to bitnamilegacy on 2025-08-28; a dependency whose licence changed can block a sale or force a rewrite.
What you get
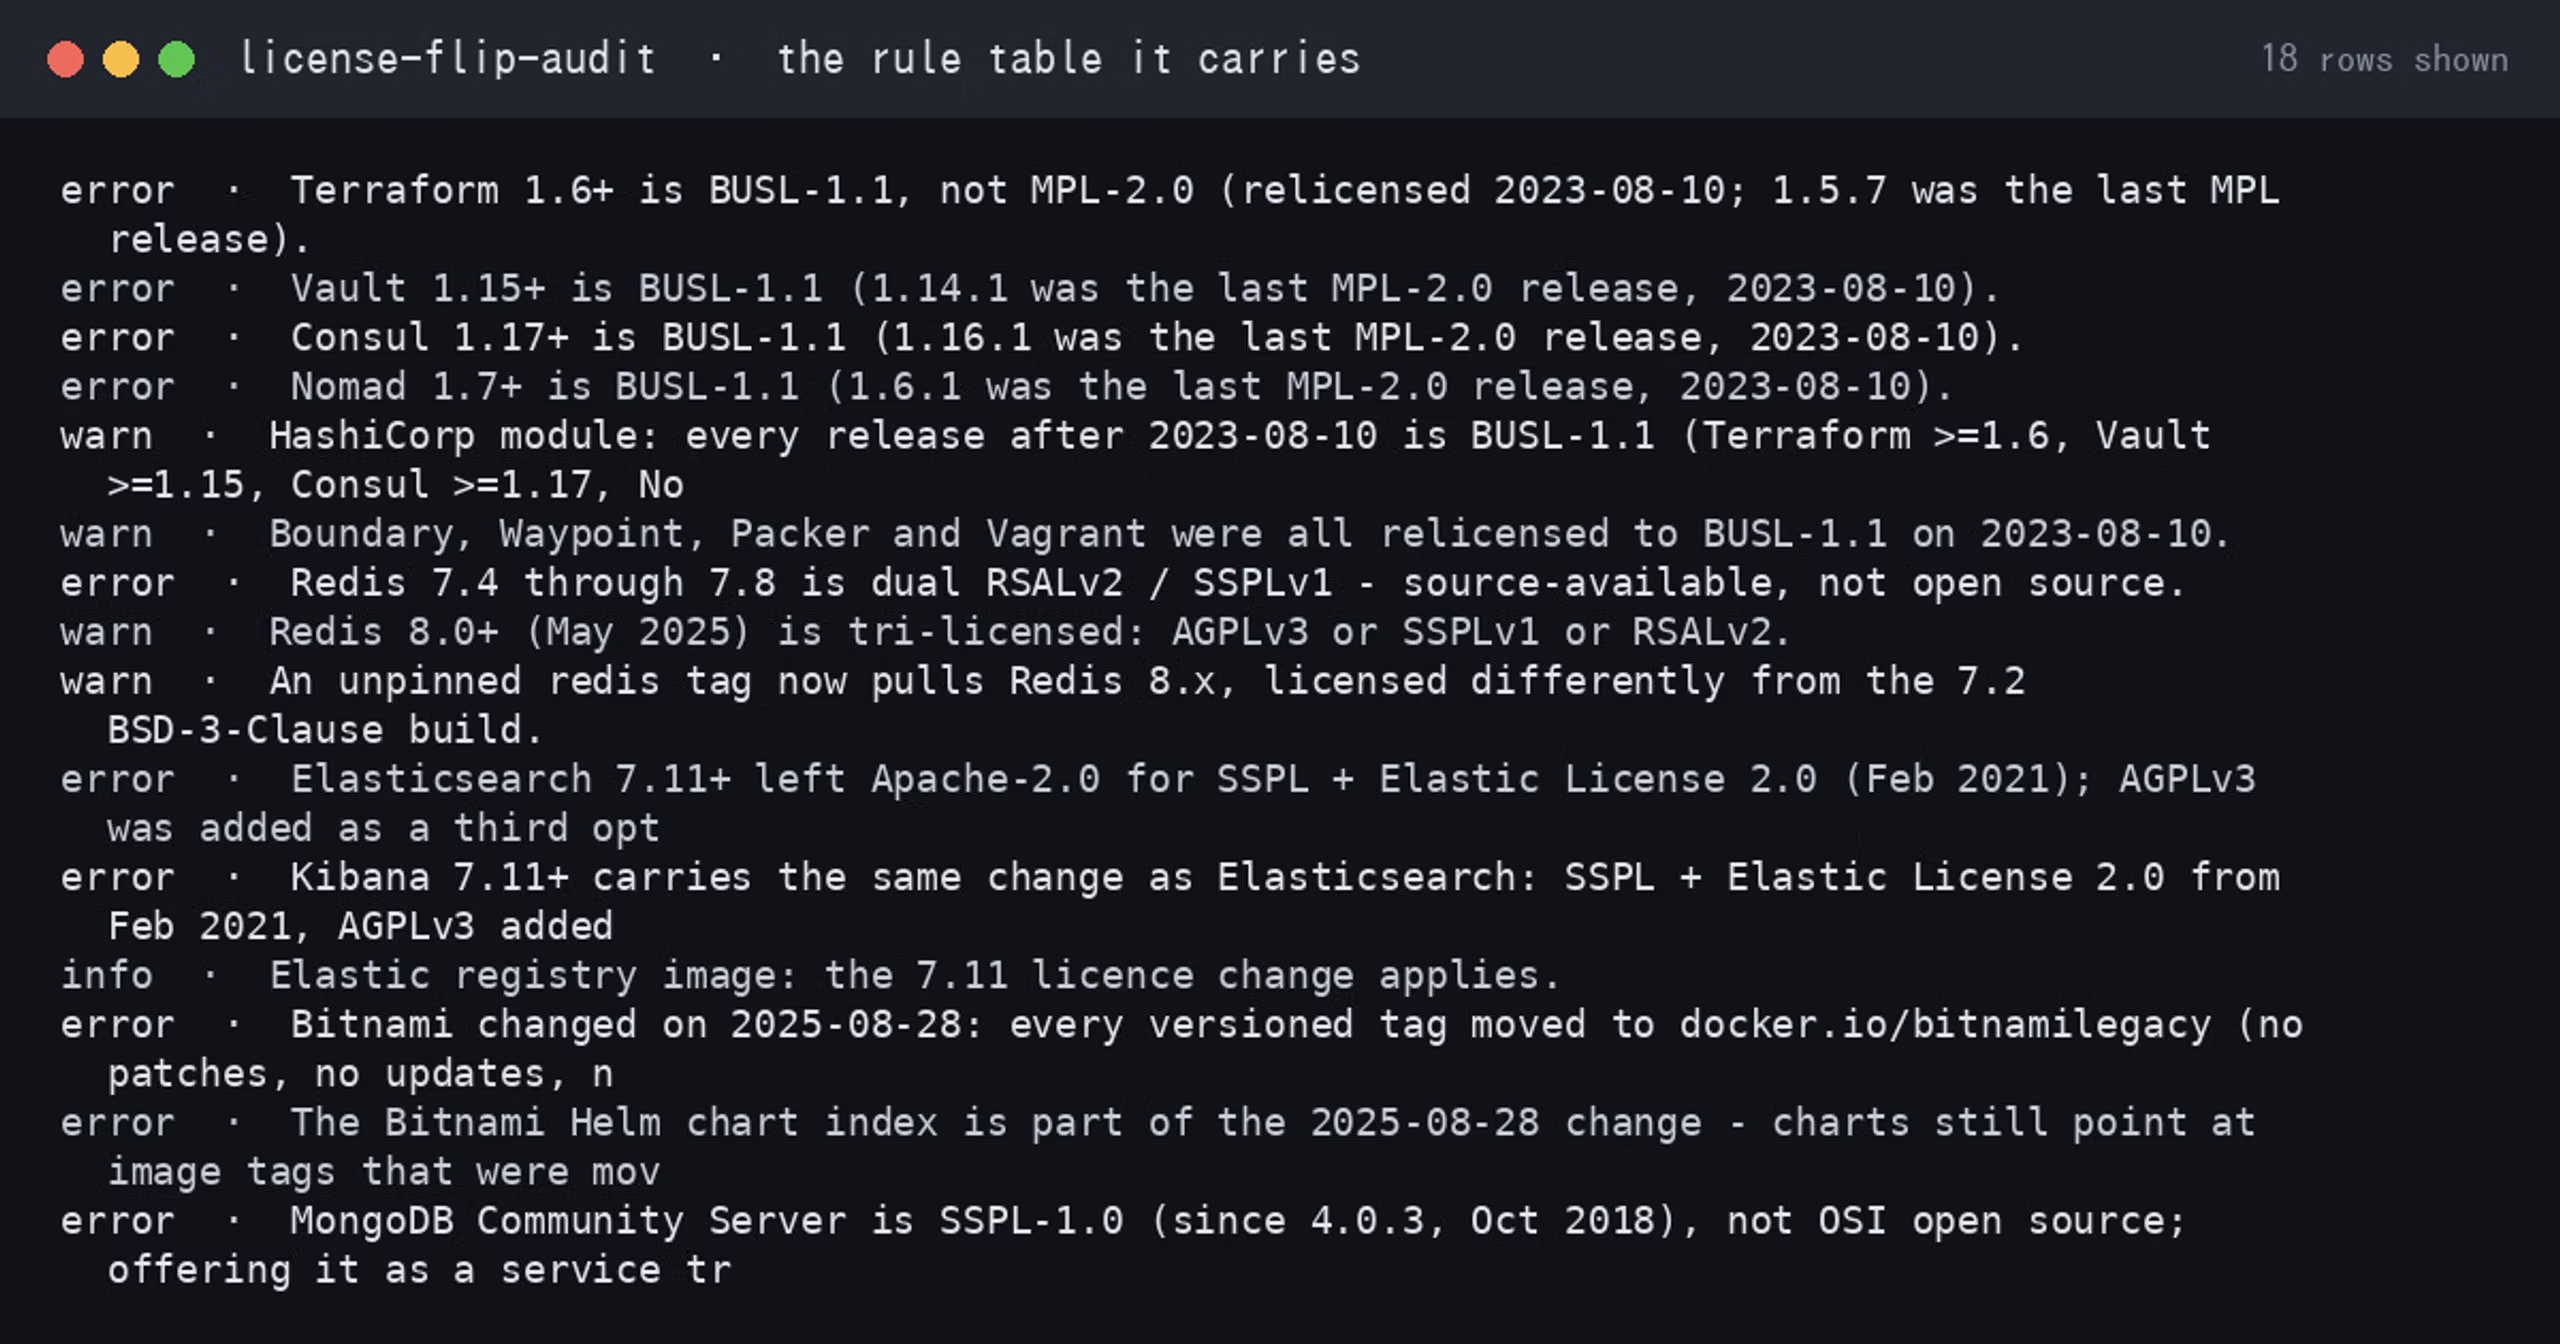
• 30 rules: HashiCorp BUSL releases, Redis, Elasticsearch, Kibana, MongoDB, CockroachDB, Grafana, MinIO…
• Ask Claude “do we use anything that is BUSL, SSPL or AGPL?” before shipping a closed-source or hosted product
See it first
The real output of the bundled example is on getreadystack.com/skills/license-flip-audit/ — free, no sign-up, so you see what it finds before you pay.
Install in 30 seconds
Unzip into ~/.claude/skills/, then ask Claude Code: “do we use anything that is BUSL, SSPL or AGPL?”. Needs Node 16+.
What it does not do
It works offline.
FAQ
Q: How is this different from asking Claude without the skill?
A: The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of guessing from memory.
Q: How do I get the files?
A: In your Whop library after paying: the lesson “license-flip-audit.zip”.